ClickFix Attacks Hide Malware in PNGs and Reach Windows Domain Controllers
Attack Tradecraft · 3 sources · Updated 6d ago · First seen Nov 11, 2026
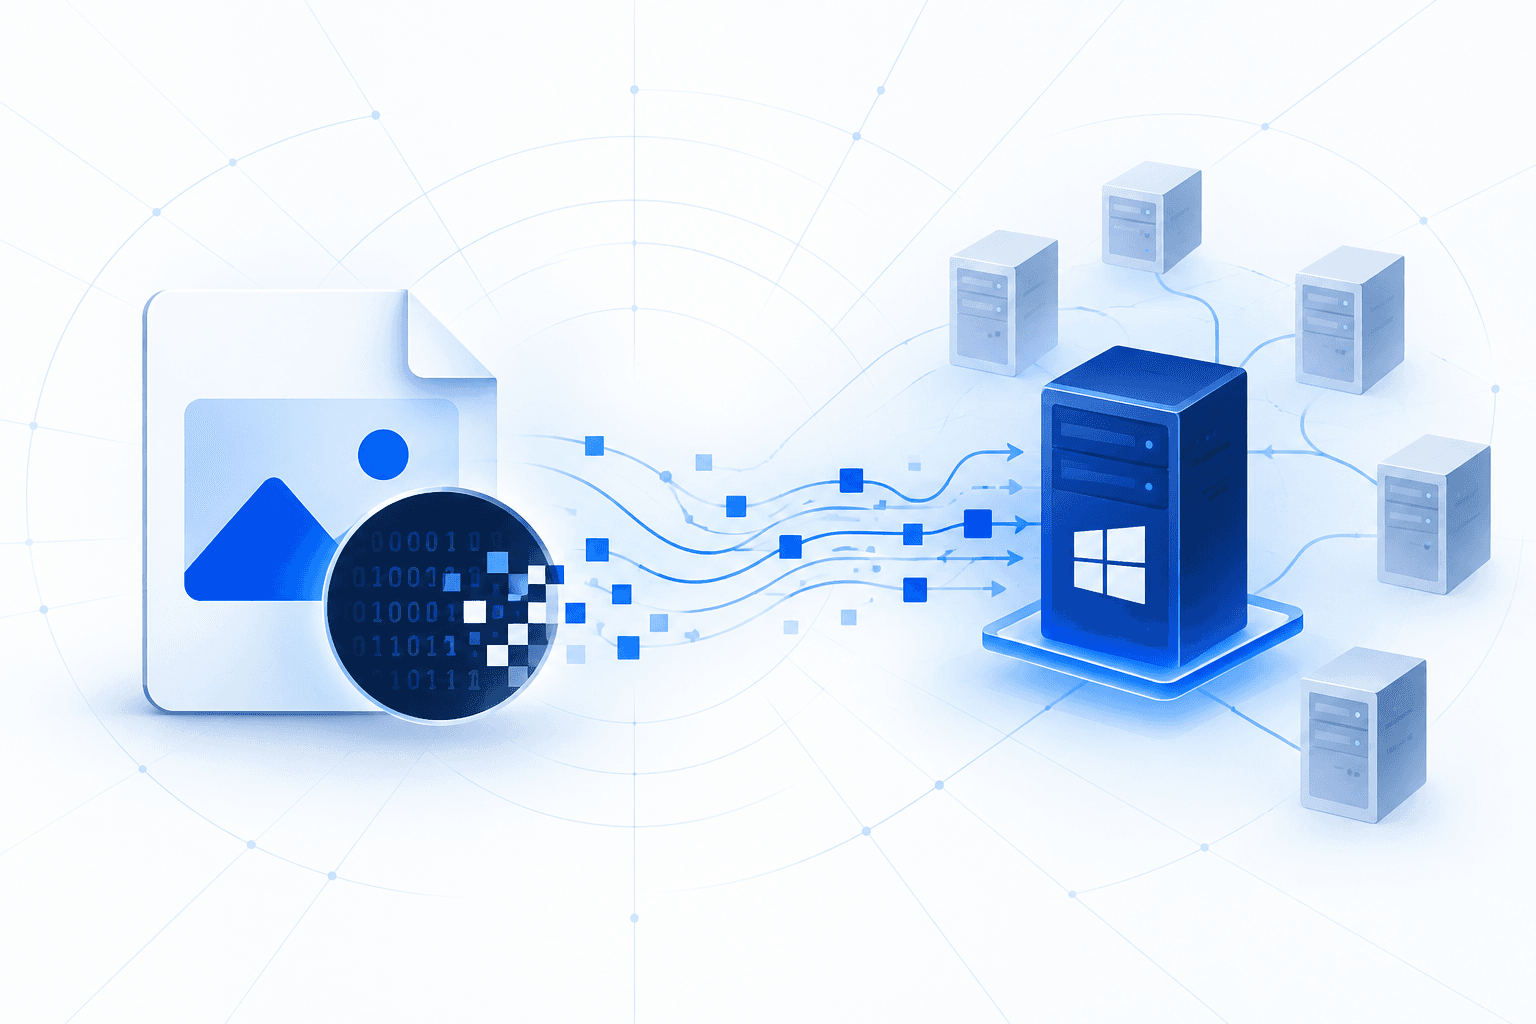
Huntress investigations detailed in a November 10 report show ClickFix attacks progressing from deceptive browser-verification prompts to persistent malware access, credential theft, and Windows domain-controller compromise. In separate attack chains, attackers reconstructed complete executables from data hidden in PNG pixels or executed a batch script recovered from browser cache, extending the technique beyond its initial reliance on users running webpage-provided commands.
Other investigated intrusions used DLL sideloading, remote administration tools, and SSH tunnels to establish access and move through corporate networks. Earlier incidents reached two domain controllers or compromised 11 hosts, demonstrating the potential for a user-driven execution event to escalate into broader enterprise compromise. Huntress recommends preventing users from pasting webpage-provided commands into terminals, restricting untrusted execution, and correlating suspicious scripting activity with persistence changes and unexpected SSH traffic.