Exposed Silent Lynx Server Reveals AI-Assisted Theft of Tajik Government Documents
Emerging Technology Risk · 6 sources · Updated 5d ago · First seen Nov 11, 2026
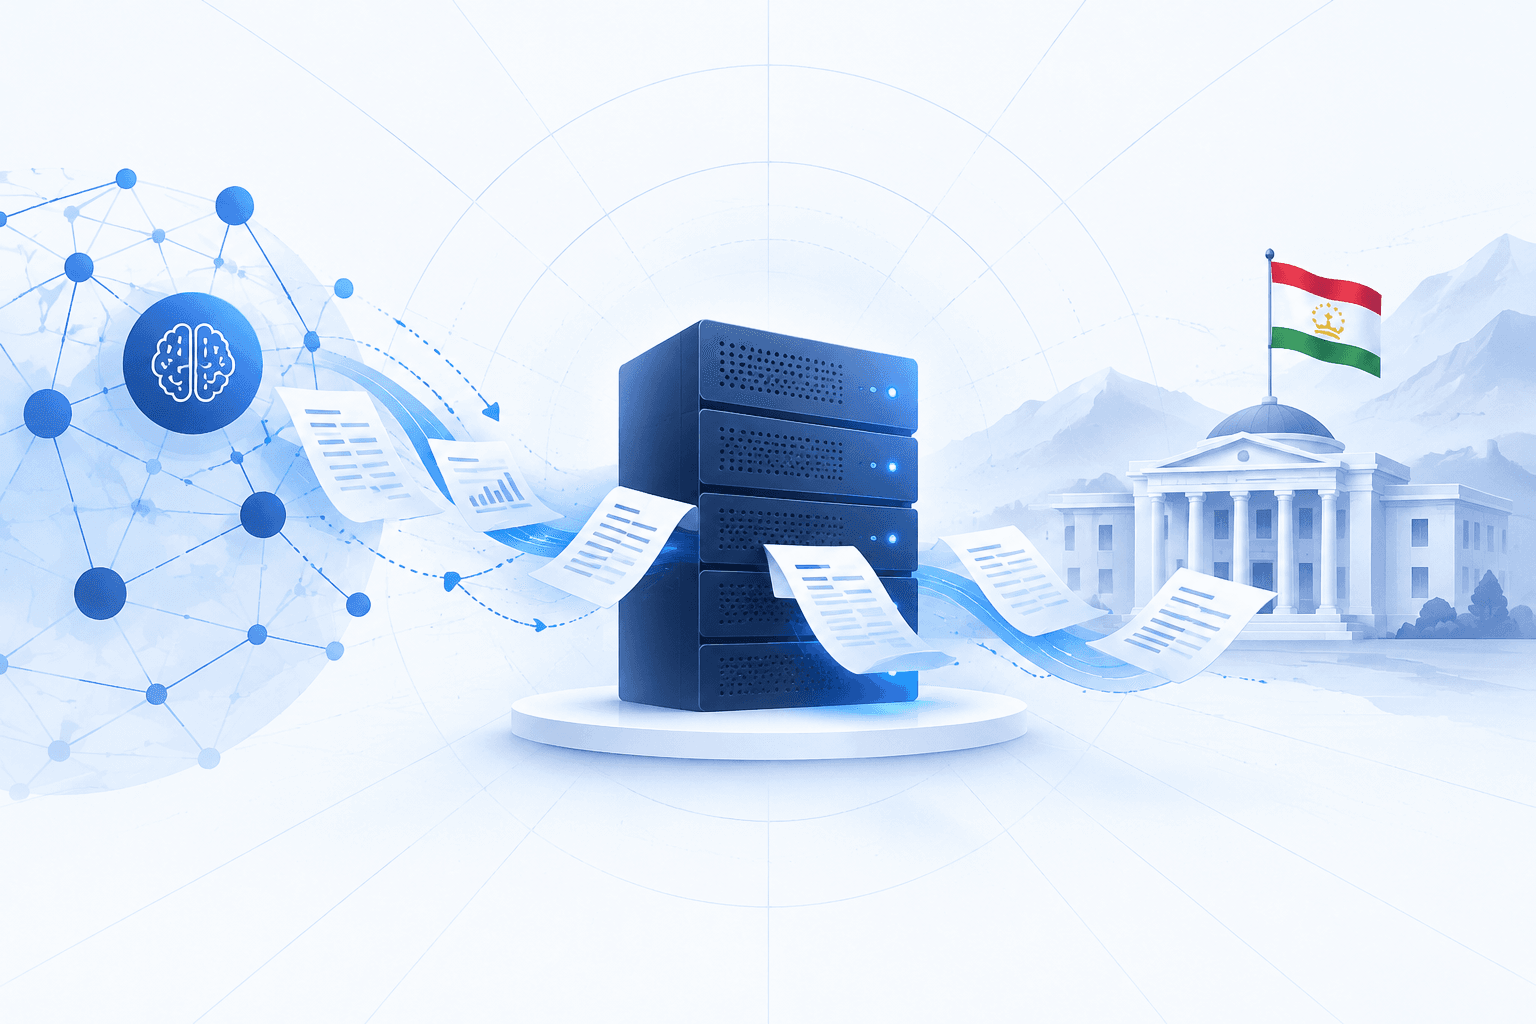
CloudSEK discovered an unauthenticated server exposing Silent Lynx tooling, stolen government documents, credentials and AI-agent conversations covering April–October 2026. Researchers reported the theft of more than 2,000 national security-related documents from Tajikistan, persistent access to Tajikistan Railway, and host-level command execution on Uzbekistan’s Smart Forestry platform. The operator used a self-hosted Hermes autonomous AI agent, primarily backed by DeepSeek models, for reconnaissance, intrusion support, document collection, preparation for exfiltration and evidence cleanup.
CloudSEK attributed the infrastructure to Silent Lynx with high confidence, citing Chvost and Laplas code markers, while assessing a Kazakhstan nexus with medium confidence. Supporting indicators included residential connections from Kazakhstan, Russian-language communications and activity during Kazakh business hours; these do not establish state sponsorship. Phishing preparations impersonating Turkmenistan Railways and the Ahal regional administration indicated prospective targeting, not a confirmed compromise. Centralizing victim data, credentials, malware and agent transcripts on the exposed server revealed operations despite the attacker’s use of Tor and other concealment measures.