AllUnited Breach Exposes Dutch Sports Members’ Data, Bank Details and Passwords
Active Exploitation · 3 sources · Updated 4d ago · First seen Nov 11, 2026
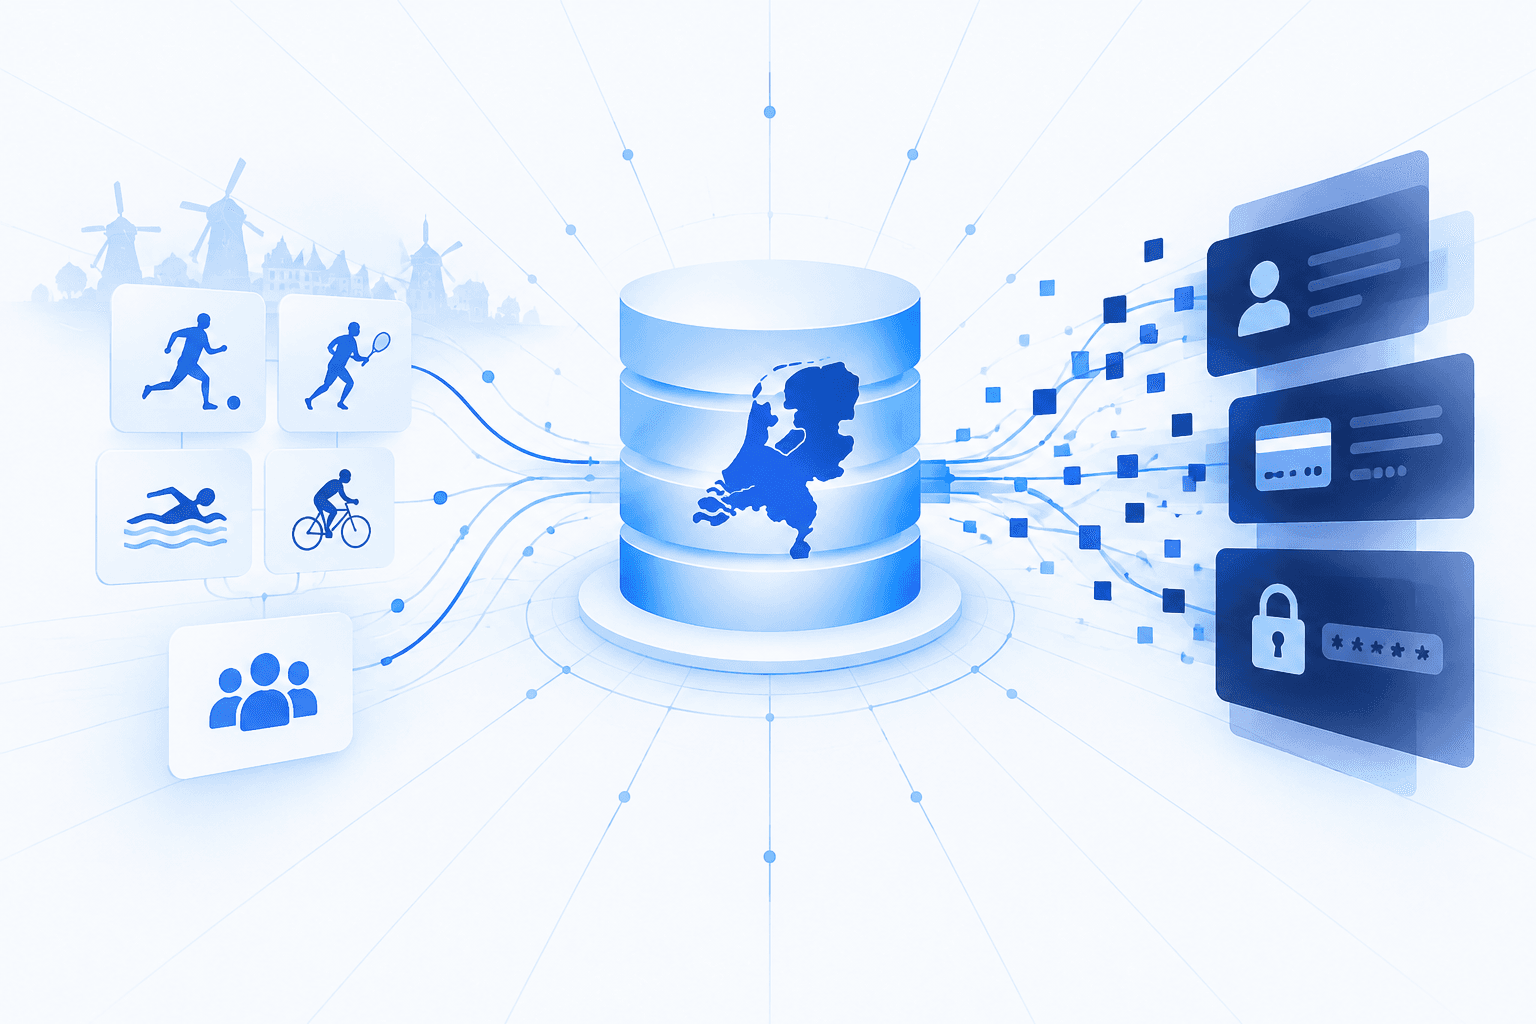
An attacker exploited a software flaw in a club website registration form on November 9 to copy database records covering all clubs and federations on AllUnited’s Dutch sports administration platform. AllUnited confirmed that exposed information included personal details, IBAN bank account numbers, encrypted passwords and readable temporary passwords, as well as potentially sensitive free-text member records, including children’s data. More than 350 sports clubs had reported breaches to the Dutch Data Protection Authority by November 11, and the regulator expected that number to rise. The total number of affected individuals remained unknown.
AllUnited discovered the intrusion and fixed the flaw on November 10, began invalidating passwords and notified customers. Several national federations and local clubs confirmed their exposure, while several federation API connections were disabled as a precaution. AllUnited reported no observed misuse of the stolen information, but the combination of identity, banking and membership data creates risks of targeted phishing and impersonation. Affected organizations should verify password resets, review potentially exposed free-text records and warn members about messages exploiting their club affiliation or financial details.