Mallory
← Back to News
phishing-campaign-intelligenceidentity-impersonation-fraudinitial-access-method

Fake INPS Website Promoted by SMS Appears Set Up for Android Malware Delivery

Social Engineering & Fraud · 3 sources · Updated 6d ago · First seen Nov 11, 2026
Fake INPS Website Promoted by SMS Appears Set Up for Android Malware Delivery

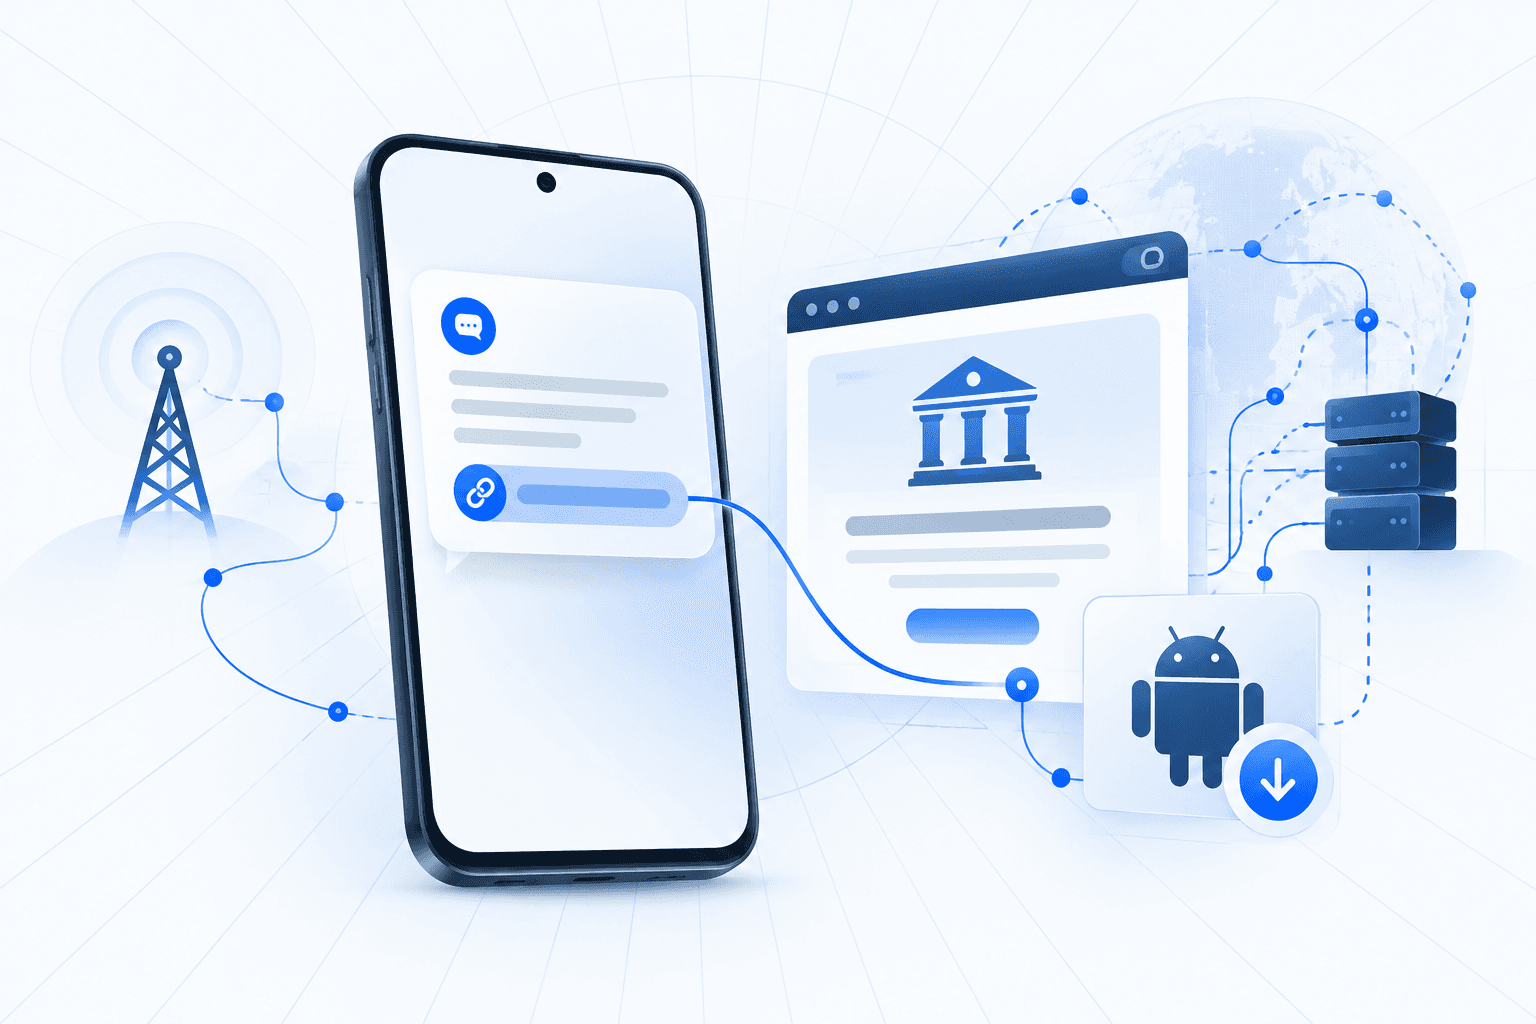
CERT-AgID, working with Italy’s social security institute INPS, identified a fraudulent website impersonating the agency’s portal and promoted through SMS messages. The domain combined “INPS” with “Italy” and had been registered two days before the report. The page offered a “Download APK” button and instructions for installing an Android application outside official app stores, but the download produced only a 40-byte text file that could not be installed. No functioning malware payload was confirmed.

The placeholder download and an inactive language selector suggested the website was still under construction. Given previous INPS-themed campaigns distributing malicious Android applications, CERT-AgID considered it plausible that attackers would replace the placeholder with malware. The agency requested the domain’s takedown, but it remained accessible at the time of reporting. Users should avoid installing applications obtained through unsolicited INPS-themed SMS links and access the institute through its official channels.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Nov 9, 2026
  1. Reported Nov 11, 20266d ago

    CERT-AGID requests takedown of the fraudulent domain

    CERT-AGID requested that the fraudulent domain be taken down. The website remained accessible at the time of reporting.

    Falso sito INPS distribuisce app infetta per Android
  2. Reported Nov 11, 20266d ago

    CERT-AGID and INPS analyze the site and identify a placeholder download

    CERT-AGID, working with INPS, analyzed the impersonation site and found that its “Download APK” button delivered a 40-byte text file rather than an installable Android application. Inactive controls suggested the site was still under construction; future malware delivery was considered plausible, but no functioning malicious payload was confirmed.

    Falso sito INPS distribuisce app infetta per Android
  3. Reported Nov 11, 20266d ago

    SMS messages distribute links to the fake INPS website

    Links to the fraudulent INPS website were distributed through SMS messages. The site purported to offer an official INPS Android application and provided instructions for installing applications outside official app stores.

    Falso sito INPS distribuisce app infetta per Android
  4. Reported Nov 11, 20266d ago

    CERT-AGID distributes indicators for the fraudulent INPS website

    CERT-AGID distributed indicators of compromise associated with the fraudulent INPS website to organizations accredited to its Flusso IoC sharing service.

    Falso sito INPS in allestimento per futura distribuzione di APK malevolo - CERT-AGID
  5. Nov 9, 20268d ago

    Fraudulent INPS-themed domain registered

    A domain combining “INPS” with “Italy” was registered through Hosting Concepts B.V. It was subsequently used for a website impersonating Italy’s social security institute.

    Falso sito INPS distribuisce app infetta per Android
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Organizations

1 linked
Istituto Nazionale della Previdenza Sociale
Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.