PowerShell ScriptBlock Smuggling Can Mislead Logging and Evade AMSI
Attack Tradecraft · 2 sources · Updated 2d ago · First seen Nov 11, 2026
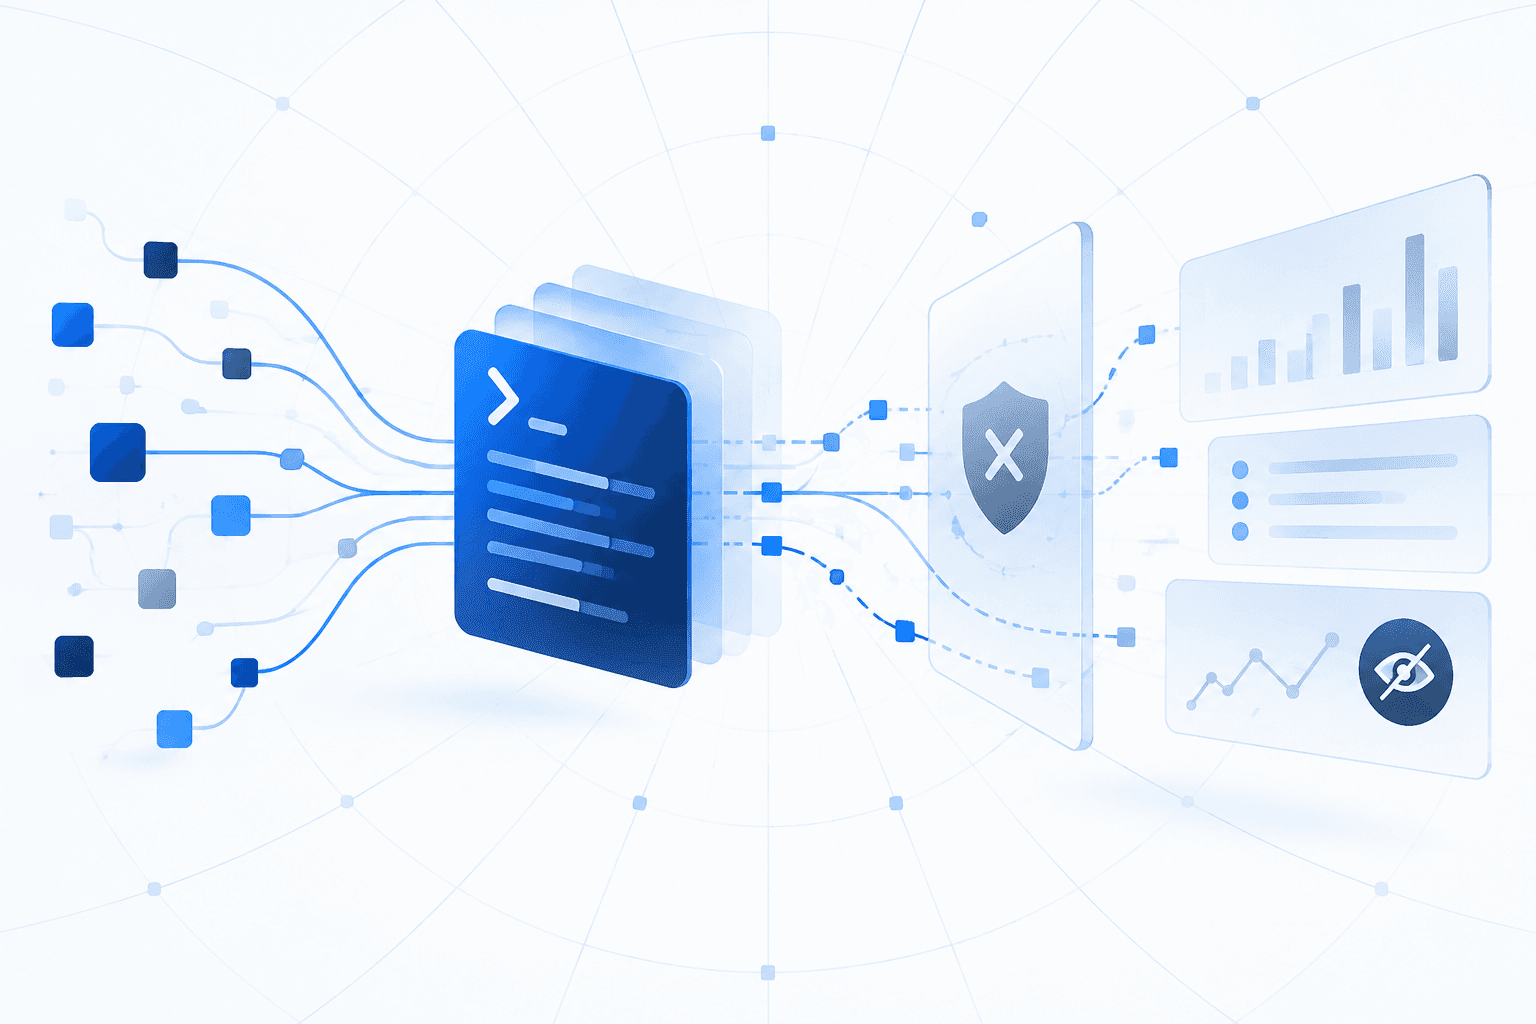
ScriptBlock Smuggling is a PowerShell evasion technique that manipulates the Abstract Syntax Tree (AST) to separate the script text presented to security controls from the instructions actually executed. The technique can make ScriptBlock logging records appear benign while different code runs, and could potentially bypass Antimalware Scan Interface (AMSI) inspection of the executed code. iPurple published research on the technique, which was also described in a technical security discussion.
The reported behavior highlights a visibility gap for organizations relying on PowerShell script logs and AMSI as evidence of what executed. Defenders should correlate those signals with process activity, endpoint telemetry, and downstream behavior rather than treating benign-looking script records as conclusive. The supplied references do not establish active exploitation, affected PowerShell versions, or an available remediation.