MCP Server Dependency Drift Creates Supply-Chain Risk to Privileged Credentials
Emerging Technology Risk · 4 sources · Updated 3d ago · First seen Nov 11, 2026
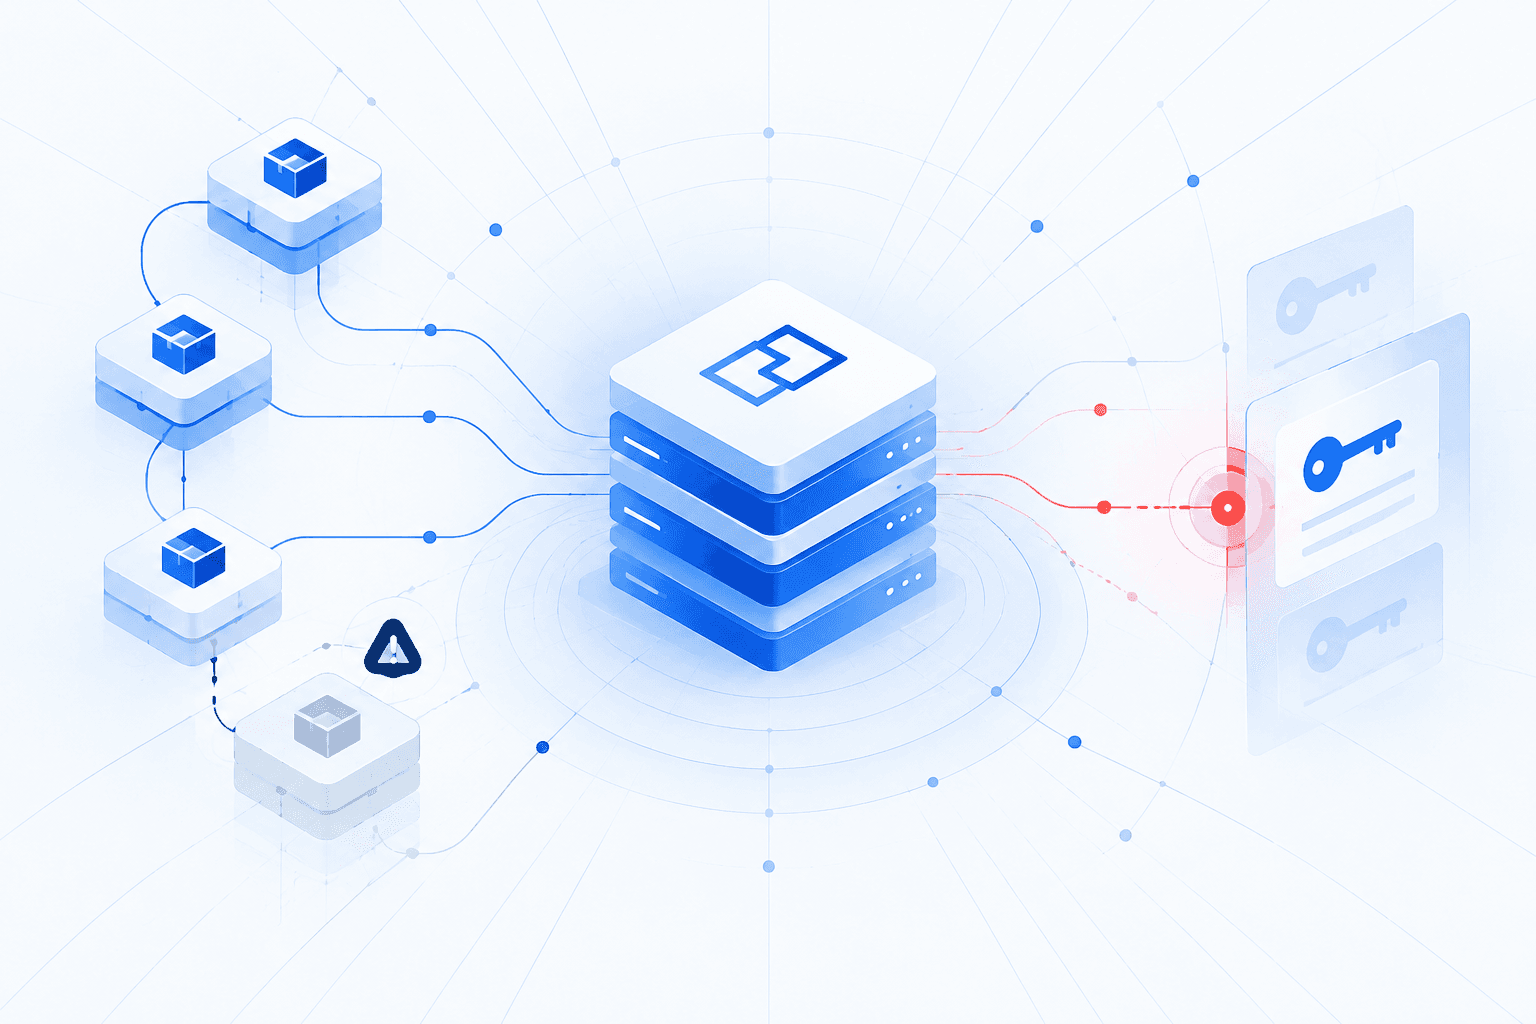
Corelight researchers found that common Model Context Protocol (MCP) server deployment methods can silently refresh dependencies at startup, even when the server package version is pinned, creating opportunities for supply-chain compromise. Of 35 servers reviewed, 23 recommended installation methods that fetched dependencies dynamically from public registries. One unchanged server produced 15 different dependency sets across 19 rebuilds. Because MCP servers can inherit privileged credentials and access management systems, a malicious dependency could steal API keys, administrator credentials and other secrets or access internal resources.
The findings identify deployment risks, not a vulnerability in MCP itself; researchers found no malware on the administrator workstation that prompted the investigation. Corelight recommended hash-pinned dependency lock files, direct server execution without startup updates, least-privilege service accounts and scheduled update reviews. Testing supported the effectiveness of frozen environments: five frozen servers retained identical package lists across 457 starts. Organizations should audit MCP launch configurations and dependency controls, prioritizing servers with administrative access or sensitive credentials.