Critical MongoDB Pre-Auth Flaw Can Crash Lagging Replica Set Members During Failover
Vulnerability Disclosure · 10 sources · Updated 23h ago · First seen Nov 11, 2026
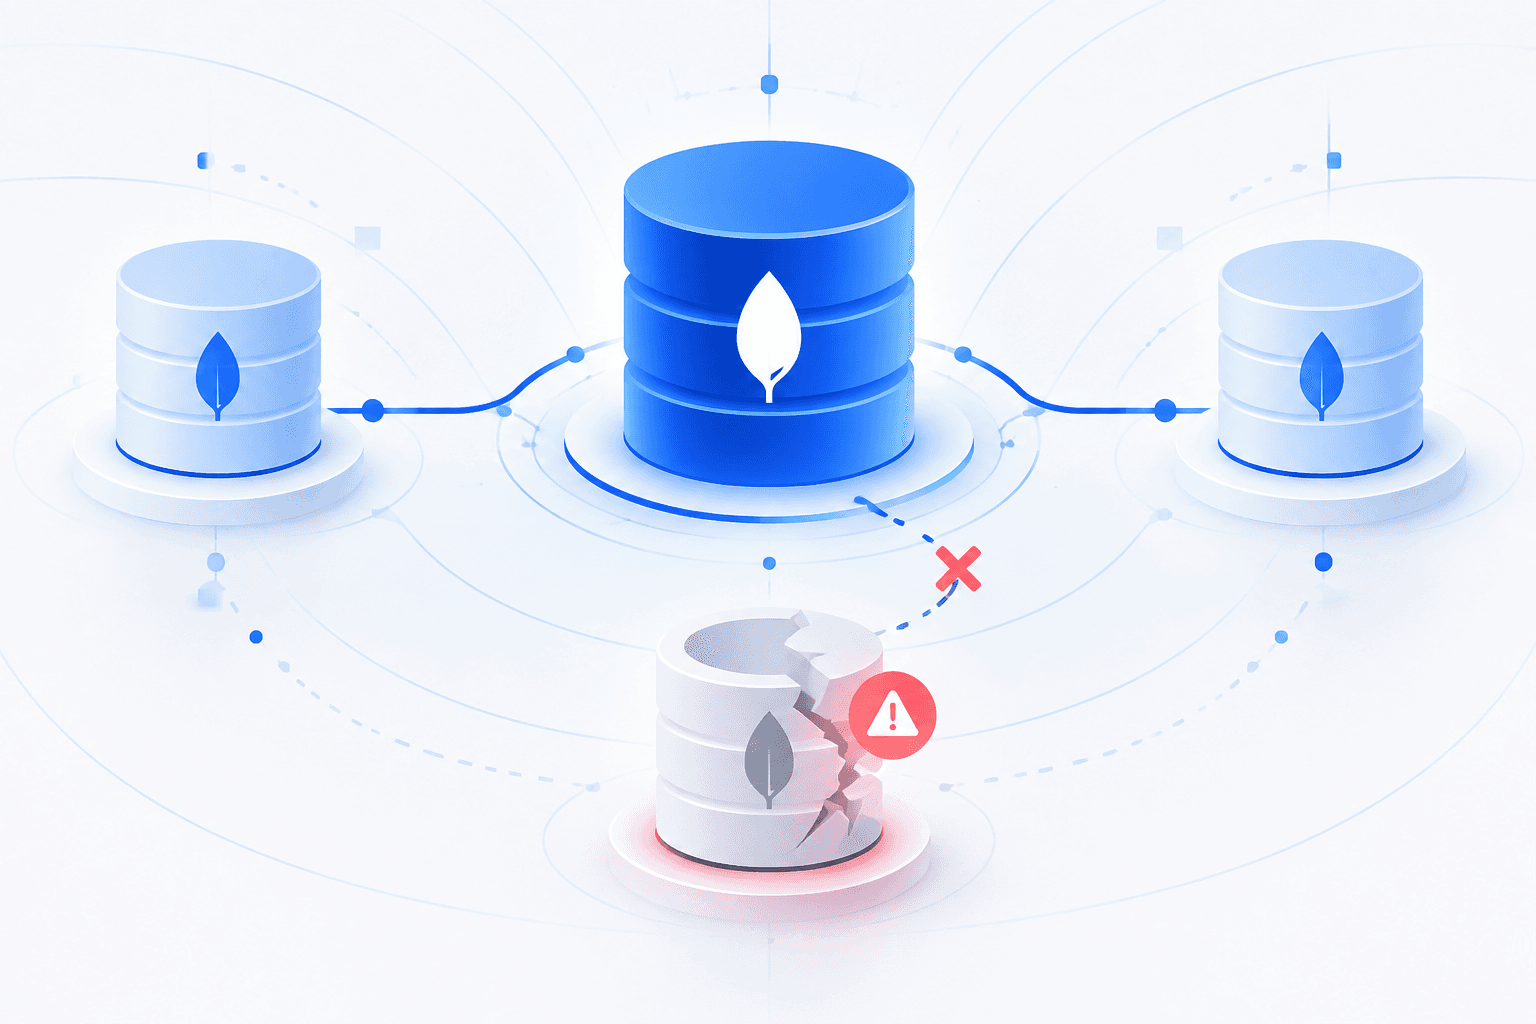
MongoDB released fixes for CVE-2026-118383, a critical use-after-free vulnerability in MongoDB Server’s primary catch-up process rated 9.5 under CVSS v4.0. The flaw affects replica set members, including shard and config server members, but not standalone instances. Datadog Security Labs reproduced a crash on MongoDB Server 8.0.34 after two unauthenticated ping requests planted abandoned waiters. Those requests alone do not cause a crash: the targeted member must subsequently become primary while behind another member in replication. MongoDB warns that arbitrary code execution may be possible, but researchers demonstrated only a crash, and the vendor reported no known exploitation attempts when announcing the update.
Organizations should upgrade every affected self-managed replica set member, rather than only the current primary; MongoDB Atlas distributes fixes through maintenance. Restrict database network access while patching to reduce exposure. Defenders should investigate suspicious requests containing readConcern.afterOpTime, particularly when followed by duplicate catch-up exits and server crashes, while treating these sequences as indicators requiring investigation rather than proof of exploitation.