Health Groups Warn HIPAA Changes Could Restrict Patient Authorization Checks
Regulatory & Policy · 5 sources · Updated 5d ago · First seen Nov 11, 2026
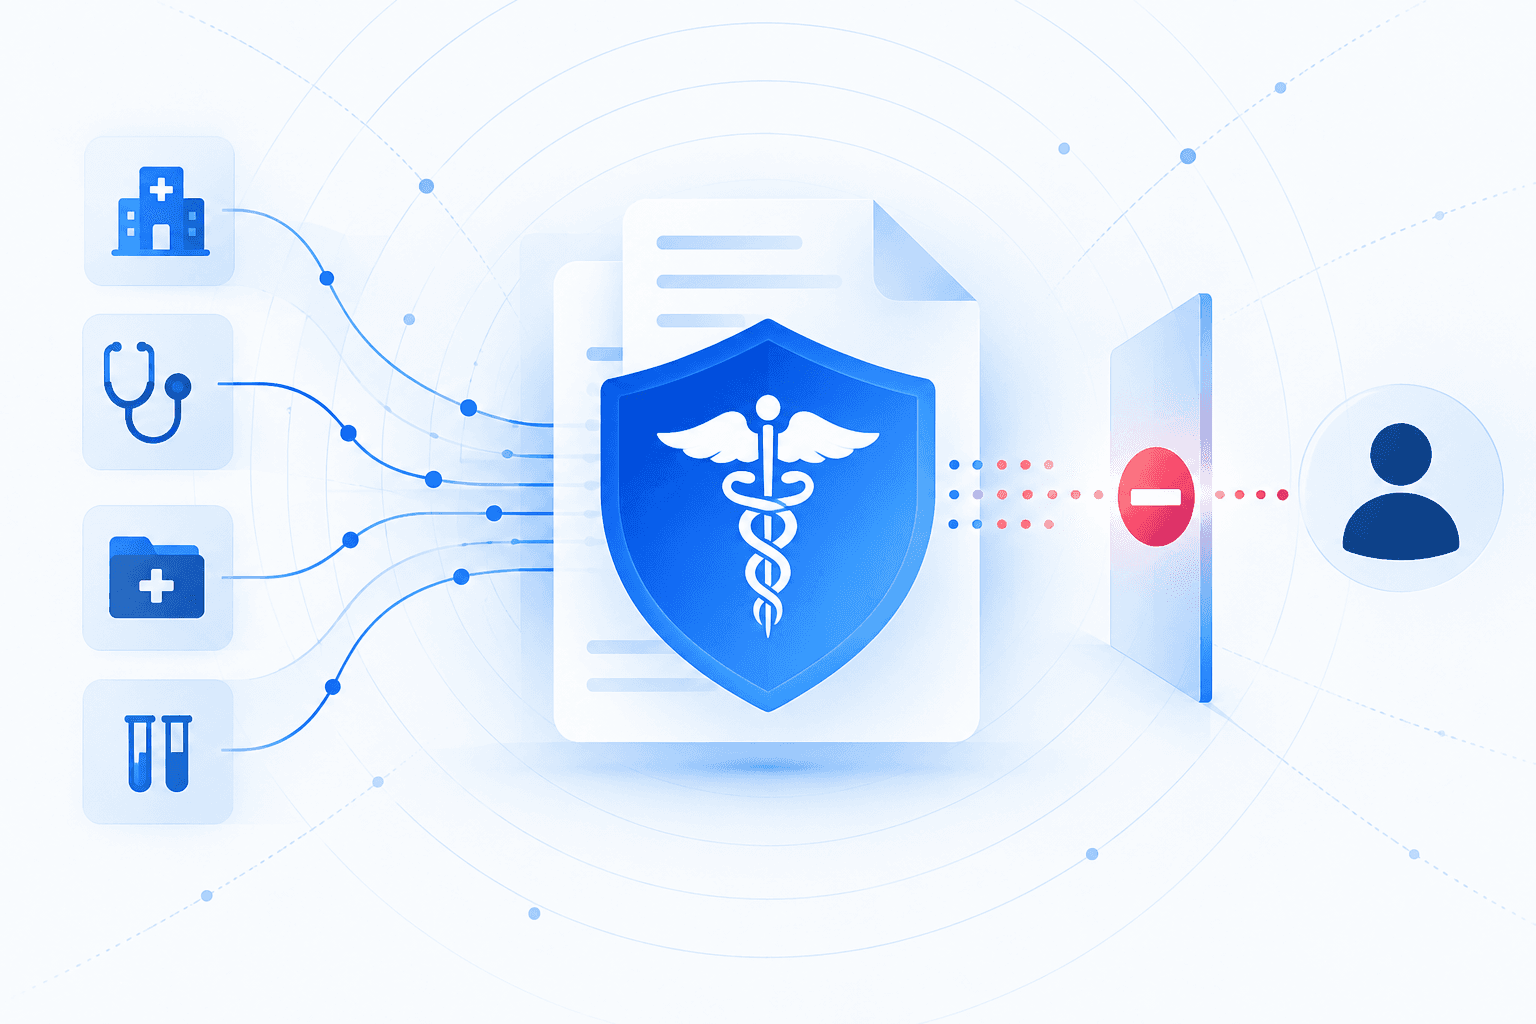
CHIME and 17 other healthcare organizations warned the U.S. Department of Health and Human Services that potential HIPAA Privacy Rule changes could prevent providers from independently verifying patient authorization before releasing protected health information to third-party applications. In a November 10 letter, the coalition argued that restricting these checks could increase unauthorized disclosures while leaving providers exposed to regulatory scrutiny and civil liability. The organizations emphasized that Identity Assurance Level 2 credentials establish identity assurance but do not necessarily confirm correct patient-record matching or valid authorization to disclose records.
The coalition also argued that prohibiting reasonable verification could exceed the scope of HHS’s 2021 proposed rule and require additional notice-and-comment rulemaking. Privacy attorneys highlighted potential conflicts with existing HIPAA safeguards and warned that disclosures to third-party applications may also implicate other federal and state privacy laws. The concerns address prospective policy risks, not a reported breach or a confirmed final rule change. For healthcare security and privacy leaders, the central issue is whether future access requirements will preserve providers’ ability to validate authorization and patient-record matching before releasing data.