ScreenConnect Campaign Compromises MSPs, Reaches 286 Endpoints Across 47 Organizations
Breach & Incident Intelligence · 28 sources · Updated 11m ago · First seen Nov 11, 2026
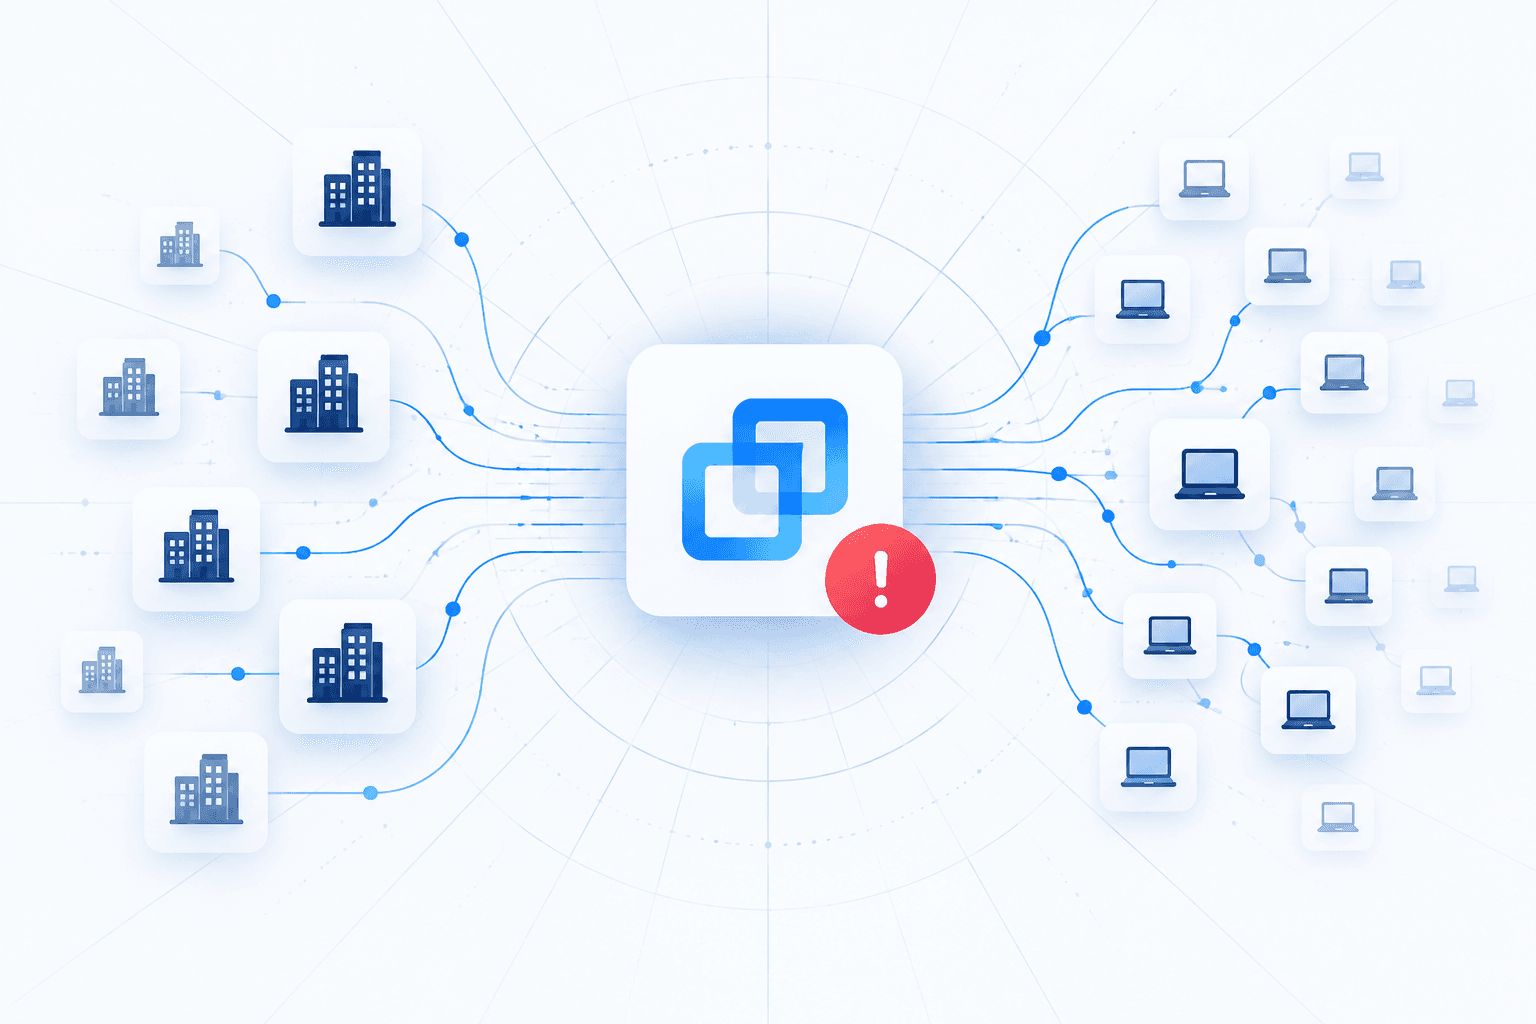
An active malware campaign is compromising managed service providers’ ScreenConnect environments and deploying unauthorized remote-access clients to customer devices. Huntress reported six compromised MSPs and at least 286 affected endpoints across 47 organizations, with victim counts increasing. ConnectWise confirmed the incident and is investigating. Initial telemetry points to compromised credentials and hijacked support sessions, but the initial access method remains unconfirmed and no specific software vulnerability has been established.
Sophos observed remote command execution using curl to download a ScreenConnect installer, Windows Installer to install it silently, and PowerShell with execution-policy bypass to retrieve a second-stage script. Its researchers identified three likely compromised ScreenConnect instances and two malicious deployment instance IDs. ConnectWise recommended disabling identified third-party extensions while investigating their possible involvement. Organizations should review remote-session command histories, investigate unexpected ScreenConnect installations and script downloads, and assess technicians’ workstations for a possible reverse pivot from infected customer devices during interactive support sessions. An earlier malicious batch script shared a rogue client identifier with this campaign, but the connection remains unclear.