Mallory
← Back to News
identity-authentication-vulnerabilityinternet-facing-service-vulnerabilityprivilege-escalation-methodpersistence-method

Critical Red Hat Quay Flaw Enables Signing-Key Takeover and Private Image Access

Vulnerability Disclosure · 18 sources · Updated 26m ago · First seen Nov 12, 2026
Critical Red Hat Quay Flaw Enables Signing-Key Takeover and Private Image Access

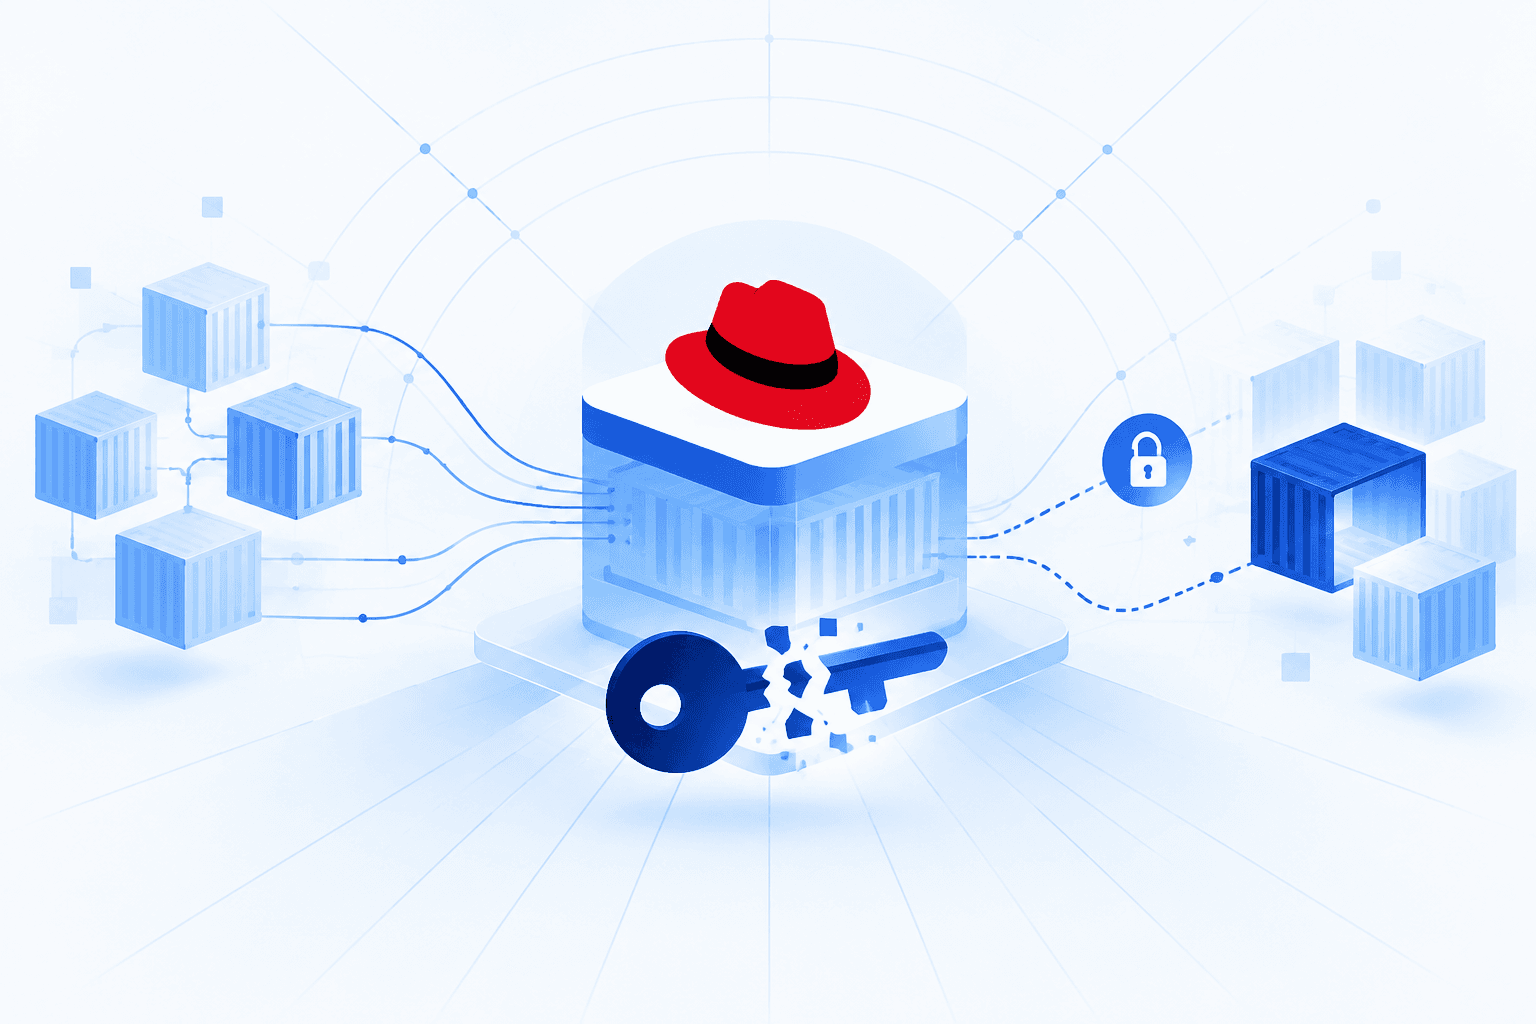
A critical authentication and authorization flaw in Red Hat Quay, CVE-2026-123710, could let unauthenticated attackers take over registry token signing and gain read/write access to every repository. Rated CVSS 9.8, the attack requires anonymous access to be enabled and the key-management endpoint, /keys, to be reachable by untrusted clients. An anonymously issued registry token can authorize service-key rotation because the key server checks its signature, audience and issuer without validating its intended purpose or permissions. An attacker can install a trusted, non-expiring signing key and forge tokens to retrieve private images, expose embedded secrets, or push and replace images and tags. Rotation also deletes the legitimate instance key, and the malicious key can be used to delete replacement keys.

Restrict access to /keys to trusted internal components, review service-key audit events and investigate unrecognized approved keys. Attacker-controlled keys can survive registry restarts; changing account credentials or disabling anonymous access does not revoke an already installed malicious key. Removing unauthorized keys alone is insufficient while attackers can reinstall them. Red Hat’s bug report confirms the flaw in the tested master commit and the 3.19-unstable image and says the vulnerable logic dates to the first public commit. Fixes were merged into the project’s GitHub repository on November 11, 2026, but the cited advisory and bug report did not identify a fixed release. No exploitation in the wild was reported in the supplied coverage.
Do you run this?See affected versions and whether adversaries are exploiting it.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events · Nov 11, 2026
  1. Reported Nov 12, 20265d ago

    Red Hat releases fixed builds for eight Quay 3 branches

    Red Hat released fixed builds for eight Quay 3 branches addressing CVE-2026-123710 and identifies the same releases as fixing CVE-2026-110697, which enables cross-tenant robot-account token theft. Red Hat also states that Quay.io is patched, although the article identifies inconsistencies between the CVE records and release advisories.

    Critical Red Hat Quay Flaw Lets Attackers Read and Overwrite All Private Container Images in a Registry
  2. Reported Nov 12, 20265d ago

    Red Hat researcher discovers Quay signing-key takeover vulnerability

    Red Hat's Dave O'Connor discovered CVE-2026-123710, which allows attackers to install a trusted signing key and forge tokens granting repository read and write access. The Bugzilla report confirmed the behavior against master commit 9226d3a5 and the 3.19-unstable image.

    Critical Red Hat Quay Vulnerability Could Expose Private Container Images - SecurityWeek
  3. Nov 11, 20266d ago

    Quay project merges fixes for signing-key takeover and another vulnerability

    Fixes for CVE-2026-123710 and CVE-2026-110697 were merged into Quay's GitHub repository. Neither Red Hat's advisory nor its Bugzilla report identified a fixed release at the time of reporting.

    Critical Red Hat Quay Vulnerability Could Expose Private Container Images - SecurityWeek
  4. Nov 11, 20266d ago

    Red Hat publishes critical Quay vulnerability advisory

    Red Hat disclosed CVE-2026-123710, rated CVSS 9.8, affecting Quay 3 and Quay 5 images when the signing-key management endpoint is reachable by untrusted clients. Red Hat recommended restricting endpoint access, reviewing key-rotation audit events, and removing unauthorized signing keys; the advisory named no fixed version.

    Critical Red Hat Quay Vulnerability Allows Unauthenticated Attackers to Hijack Container Registries
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

2 linked
QuayMirror Registry For Red Hat Openshift
Do you run this?See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
Check Your Exposure
Source coverage

Sources

18 references tracked. Mallory keeps watching after this page renders.

Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.