Mallory
← Back to News
telecommunications-sector-threatcommunication-services-sector-threatstate-sponsored-espionagecommand-and-control-method

SilentAir Abuses Compromised Asian Telcos to Intercept Taiwanese Calls and Texts

Sector Threat Intelligence · 21 sources · Updated 6h ago · First seen Nov 12, 2026
SilentAir Abuses Compromised Asian Telcos to Intercept Taiwanese Calls and Texts

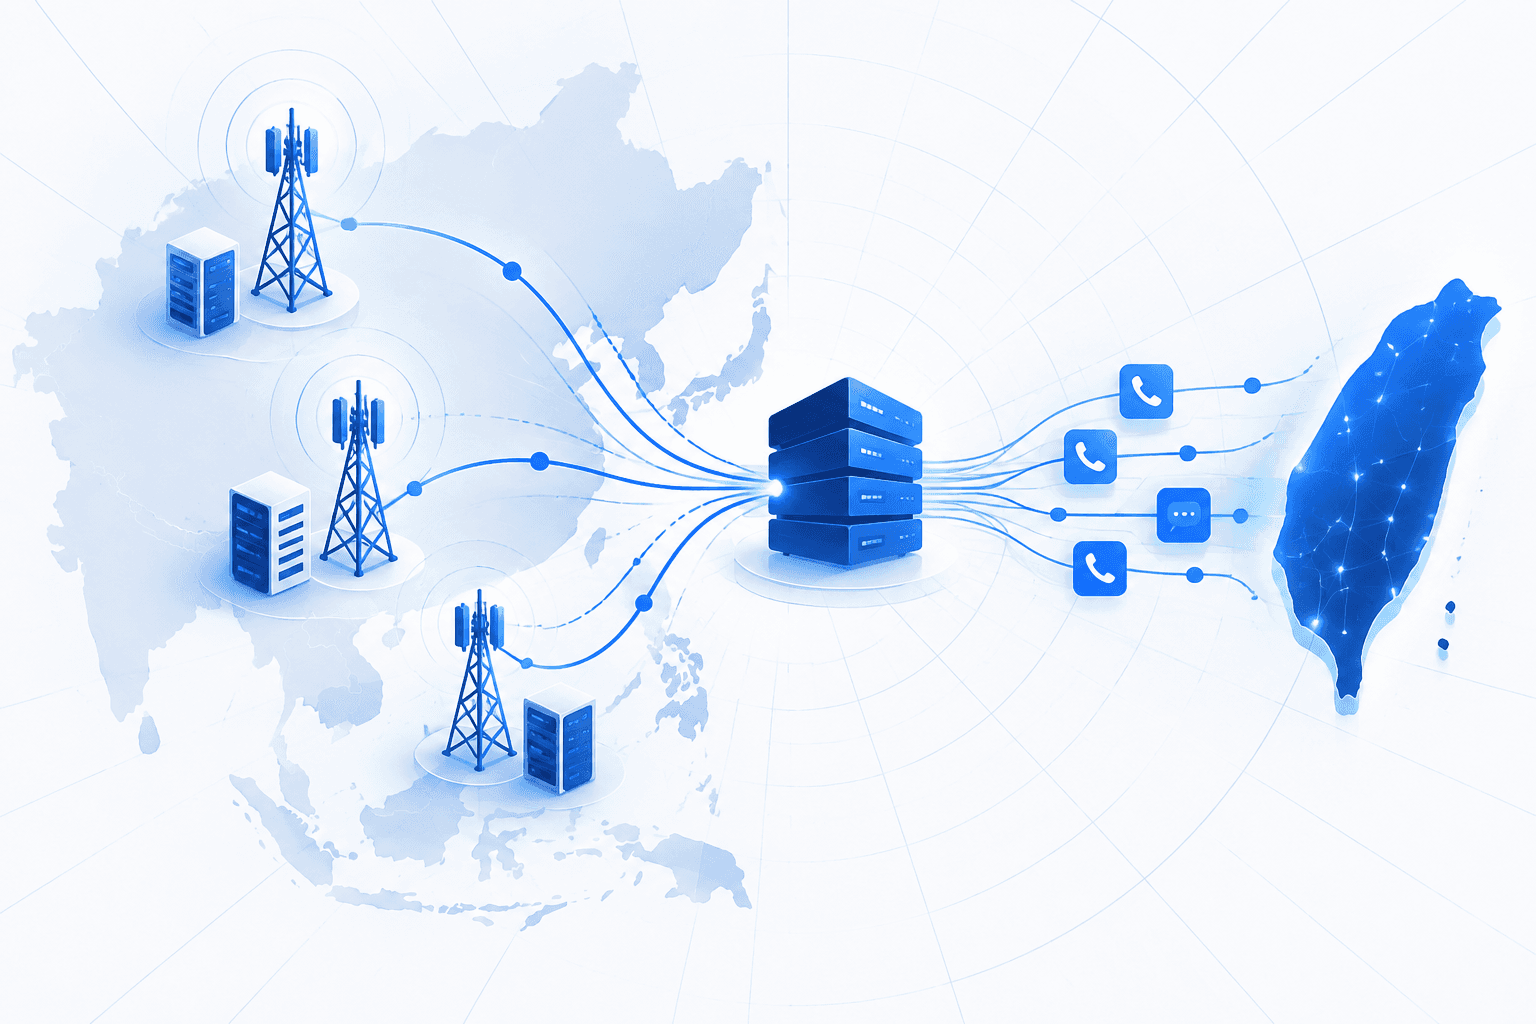
Enea identified SilentAir, an actor using compromised Asian mobile operators to intercept calls and text messages, primarily targeting Taiwanese subscribers. The activity exploited SS7 and Diameter signaling, with some interceptions associated with the arrival of two-factor authentication codes, suggesting attempts to compromise victims’ other accounts. Enea assessed with high confidence that SilentAir operates at state level, but linked it to China-nexus operations only with low confidence; a possible connection to Liminal Panda remains unproven.

Separately, Enea detected Liminal Panda at multiple operators and identified a new GTPDoor backdoor variant that hides command-and-control traffic within GTP-U user-data traffic. CrowdStrike previously documented Liminal Panda targeting telecommunications providers since at least 2020, using custom tools to collect subscriber information, call metadata and SMS messages, and leveraging compromised telecom servers to penetrate other providers. Enea reported helping customers remove Liminal Panda and notifying operators hosting SilentAir attack sources, but warned that conditions enabling renewed activity remained. Operators should prioritize signaling-abuse detection, scrutiny of GTP-U traffic and investigation of cross-provider access paths.
Who's targeting your sector?See the actors and campaigns active against you right now.
See sector threats
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

14 events · 2016 – Nov 11, 2026
  1. Reported Nov 16, 20262d ago

    Brandefence links some LIMINAL PANDA members to China's Ministry of State Security

    Brandefence assessed with moderate confidence that some LIMINAL PANDA members might work for a regional office of China's Ministry of State Security. This assessment followed CrowdStrike's low-confidence assessment of the group's China links.

    SilentAir and LIMINAL PANDA Target Telecom Networks to Spy on Subscribers
  2. Reported Nov 12, 20265d ago

    Enea helps remove Liminal Panda and alerts SilentAir source operators

    Enea helped customers remove Liminal Panda and notified operators whose equipment hosted SilentAir attack sources. It assessed that both groups had been temporarily disrupted but warned that conditions enabling renewed activity remained.

    Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts - Infosecurity Magazine
  3. Reported Nov 12, 20265d ago

    Enea discovers a GTPDoor variant using GTP-U traffic

    Enea discovered a new GTPDoor variant that conceals command-and-control communications within GTP-U user-data traffic, which receives less monitoring than GTP control traffic. Enea assessed that the variant primarily served as a fallback.

    Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts - Infosecurity Magazine
  4. Nov 11, 20267d ago

    Enea names SilentAir and discloses interception campaign

    Enea published research naming SilentAir, assessing with high confidence that it operated at state level and linking it to China-nexus operations with low confidence. The research described call and text interception, including activity coinciding with targets receiving two-factor authentication codes, and identified a possible but unproven connection to Liminal Panda.

    Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts - Infosecurity Magazine
  5. Jul 2026

    POST Luxembourg publicly reports detecting GTPDoor activity

    POST Luxembourg publicly reported detecting GTPDoor activity, adding another operator's observation of the covert command-and-control implant.

    The Enemy Within. Tracking LIMINAL PANDA and SilentAir through Mobile Networks | Enea
  6. 2026

    Enea detects and blocks Liminal Panda activity at mobile operators

    Beginning in early 2026, Enea's firewalls detected and blocked GTPDoor and other Liminal Panda activity at several customer mobile operators. Enea detected several hundred attempted command-and-control exchanges.

    Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts - Infosecurity Magazine
  7. 2025

    Enea begins monitoring SilentAir

    Enea began monitoring SilentAir in early 2025. The actor used compromised mobile operator equipment in at least six Asian countries to conduct SS7 and Diameter attacks, primarily targeting Taiwanese subscribers.

    Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts - Infosecurity Magazine
  8. Nov 2024

    CrowdStrike links Liminal Panda to China-nexus operations

    CrowdStrike linked Liminal Panda to China-nexus operations with low confidence, according to Enea's subsequent account.

    Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts - Infosecurity Magazine
  9. Feb 27, 20243y ago

    GTPDoor backdoor first documented

    GTPDoor was first documented on February 27, 2024. The backdoor conceals command-and-control communications in GTP-C signaling traffic used by telecommunications networks.

    SilentAir Hijacks Asian Telecom Networks to Intercept SMS 2FA Codes and Spy on Taiwanese Users
  10. Feb 2024

    CL-STA-0969 targets Southwest Asian telecommunications providers

    Between February and November 2024, CL-STA-0969 compromised Southwest Asian telecom providers, leveraging interconnected roaming networks and deploying implants including AuthDoor, GTPDoor and ChronosRAT. Unit 42 assessed a high-confidence nation-state nexus and heavy overlap with Liminal Panda, but found no clear evidence of data collection or exfiltration in the investigated cases.

    The Covert Operator's Playbook: Infiltration of Global Telecom Networks
  11. Reported Feb 9, 20225y ago

    Enea identifies HiddenArt as a Russian-linked SS7 threat actor

    Enea identified HiddenArt as a Russian-linked threat actor associated with SS7 activity.

    HiddenArt – A Russian-linked SS7 Threat Actor
  12. 2021

    CrowdStrike attributes telecom intrusions to LightBasin

    CrowdStrike attributed multiple telecommunications-sector intrusions to the LightBasin activity cluster.

    Unveiling LIMINAL PANDA: A Closer Look at China's Cyber Threats to the Telecom Sector
  13. 2020

    Liminal Panda targets telecom networks for intelligence collection

    Liminal Panda targeted telecommunications entities from at least 2020 using custom tools for covert access, command and control, and data exfiltration. Its operations included using compromised telecom servers to penetrate additional providers and retrieving subscriber information, call metadata, and text messages.

    Unveiling LIMINAL PANDA: A Closer Look at China's Cyber Threats to the Telecom Sector
  14. 2016

    LightBasin begins targeting telecommunications providers

    The LightBasin activity cluster targeted telecommunications entities using custom tools from at least 2016.

    Unveiling LIMINAL PANDA: A Closer Look at China's Cyber Threats to the Telecom Sector
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

2 linked

Malware

2 linked

Organizations

1 linked
Liminal Panda

Observables

25 linked

Indicator values are masked on this page. View all 25 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
See Your Sector's Threats
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.