Weak SQL Server Passwords Enable Monero Mining and Gh0st RAT Deployment
Malware Intelligence · 9 sources · Updated 13h ago · First seen Nov 12, 2026
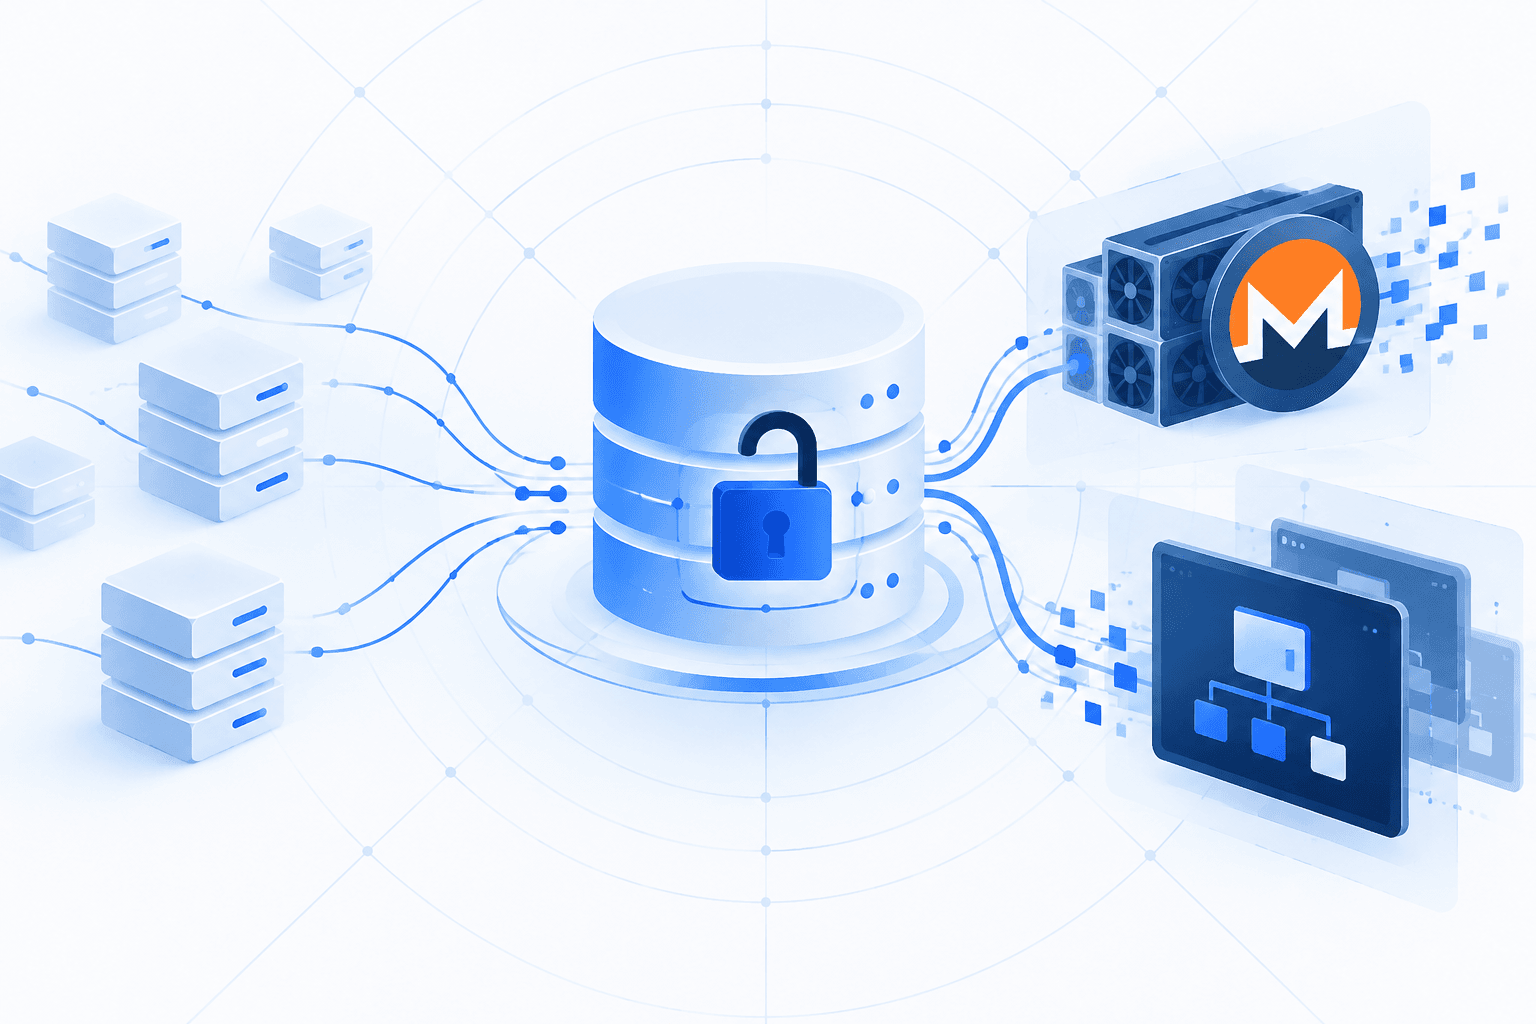
Attackers are compromising internet-facing Microsoft SQL Server instances with weak credentials to deploy a Monero cryptominer and a Gh0st remote access trojan variant. FortiGuard Labs discovered the active campaign in early October and reported that it abuses legitimate database administration features rather than a newly identified software vulnerability. A Go-based payload incorporating Naabu scans TCP port 1433, while a separate .NET executable attempts authentication using predefined usernames and more than 2,700 passwords. After obtaining sufficiently privileged access, attackers enable SQL Server’s xp_cmdshell feature to execute Windows commands and install loaders that retrieve the malware from attacker-controlled infrastructure.
The campaign establishes persistence through scheduled tasks, a Windows service, registry Run keys and the Startup folder. The miner consumes server processing resources, while Gh0st RAT provides capabilities for host profiling, file access, keylogging, data theft and remote control. Researchers could not verify the RAT’s live communications because its command-and-control server was offline; neither the responsible threat actor nor the number of compromised servers was identified. Defenders should restrict external SQL Server access, strengthen credentials, limit database privileges and monitor operating-system command execution and persistence mechanisms. Incident response should investigate the full compromise rather than treating removal of the miner as sufficient remediation.