China-Nexus Actor Uses Cairn AI Framework to Breach 10 Organizations
Emerging Technology Risk · 2 sources · Updated 4d ago · First seen Nov 12, 2026
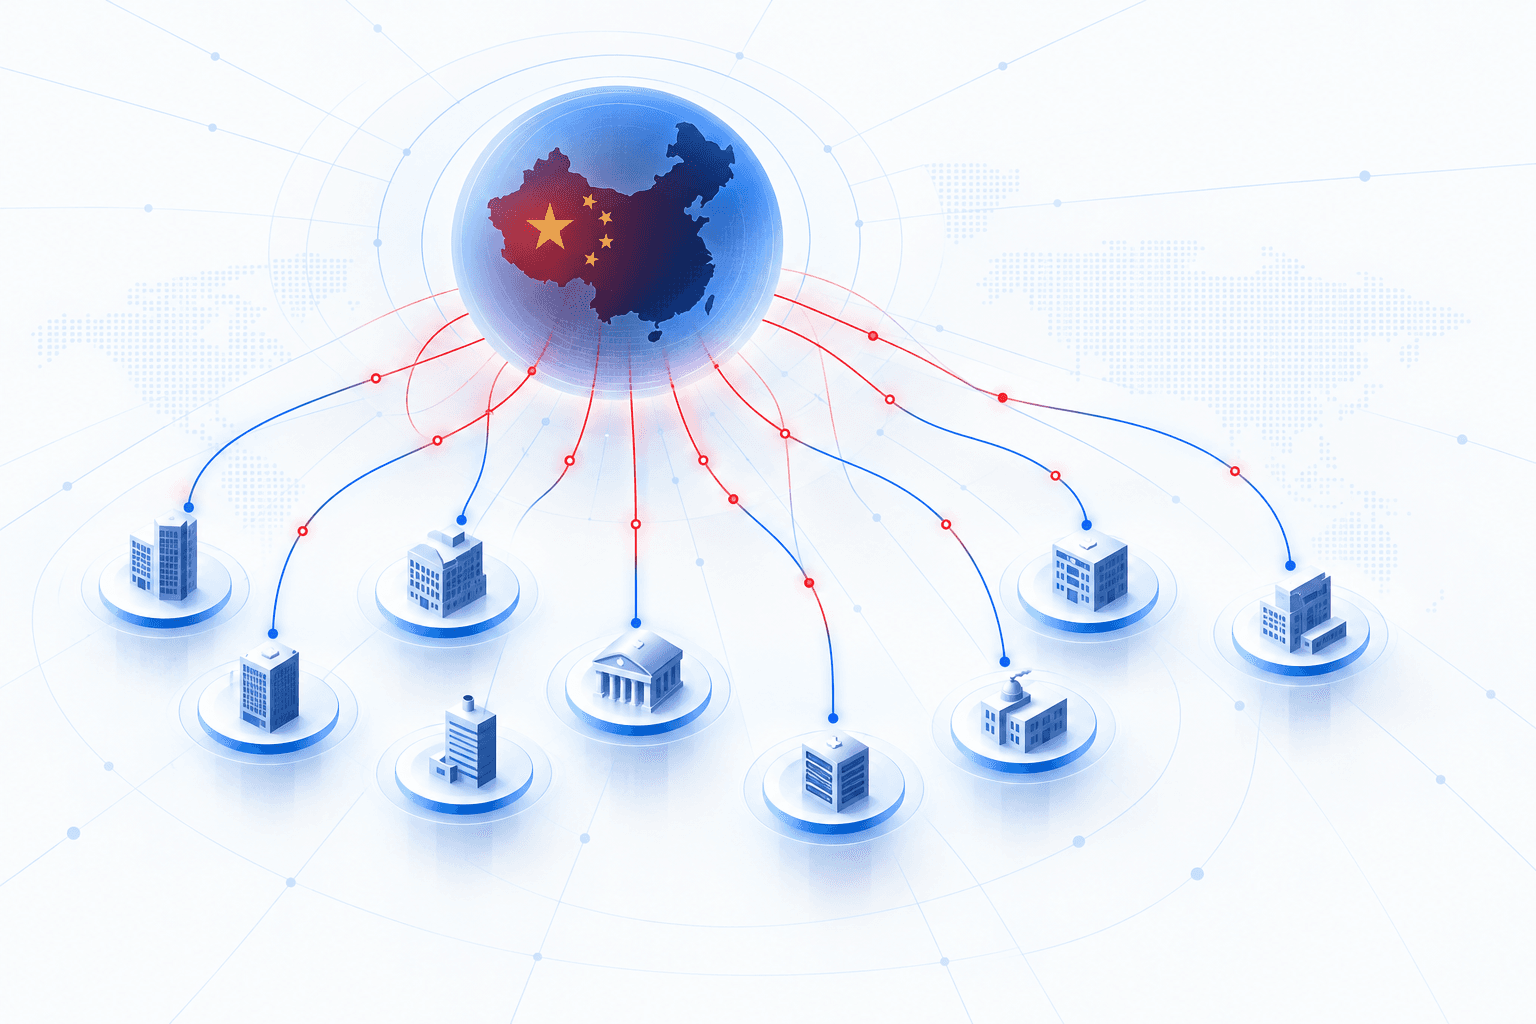
A Chinese-speaking threat actor used a customized version of the open-source Cairn AI penetration-testing framework to conduct 25 operations against at least 19 organizations in August and September 2026, gaining unauthorized access or extracting data at 10. Palo Alto Networks’ Unit 42 tracked the campaign as CL-STA-1238 and assessed with moderate confidence that it represented China-nexus intelligence collection. Targets included U.S. semiconductor, defense and human rights organizations. Likely operated by one person or a small team, the campaign combined Zhipu GLM and DeepSeek models with tailored scanning and exploitation capabilities and prompts falsely describing the intrusions as authorized testing.
Autonomous agents performed reconnaissance, exploitation, credential theft, privilege escalation and persistence, with individual runs lasting from 20 minutes to more than 50 hours. Reported outcomes included access to more than one million teachers’ union member records, theft of 500 defense-policy think tank user records and 150,000 industrial-automation documents, manipulation of an industry standards body’s systems, and persistent access at a semiconductor company. The attackers exploited familiar weaknesses—including authentication bypasses, weak credentials and exposed APIs—rather than relying on more sophisticated exploits, underscoring the importance of closing these gaps and detecting sustained automated intrusion activity.