Fake Teams Meeting Scheduler Tricks Employee Into Authorizing Attacker Sign-In
Social Engineering & Fraud · 3 sources · Updated 4d ago · First seen Nov 13, 2026
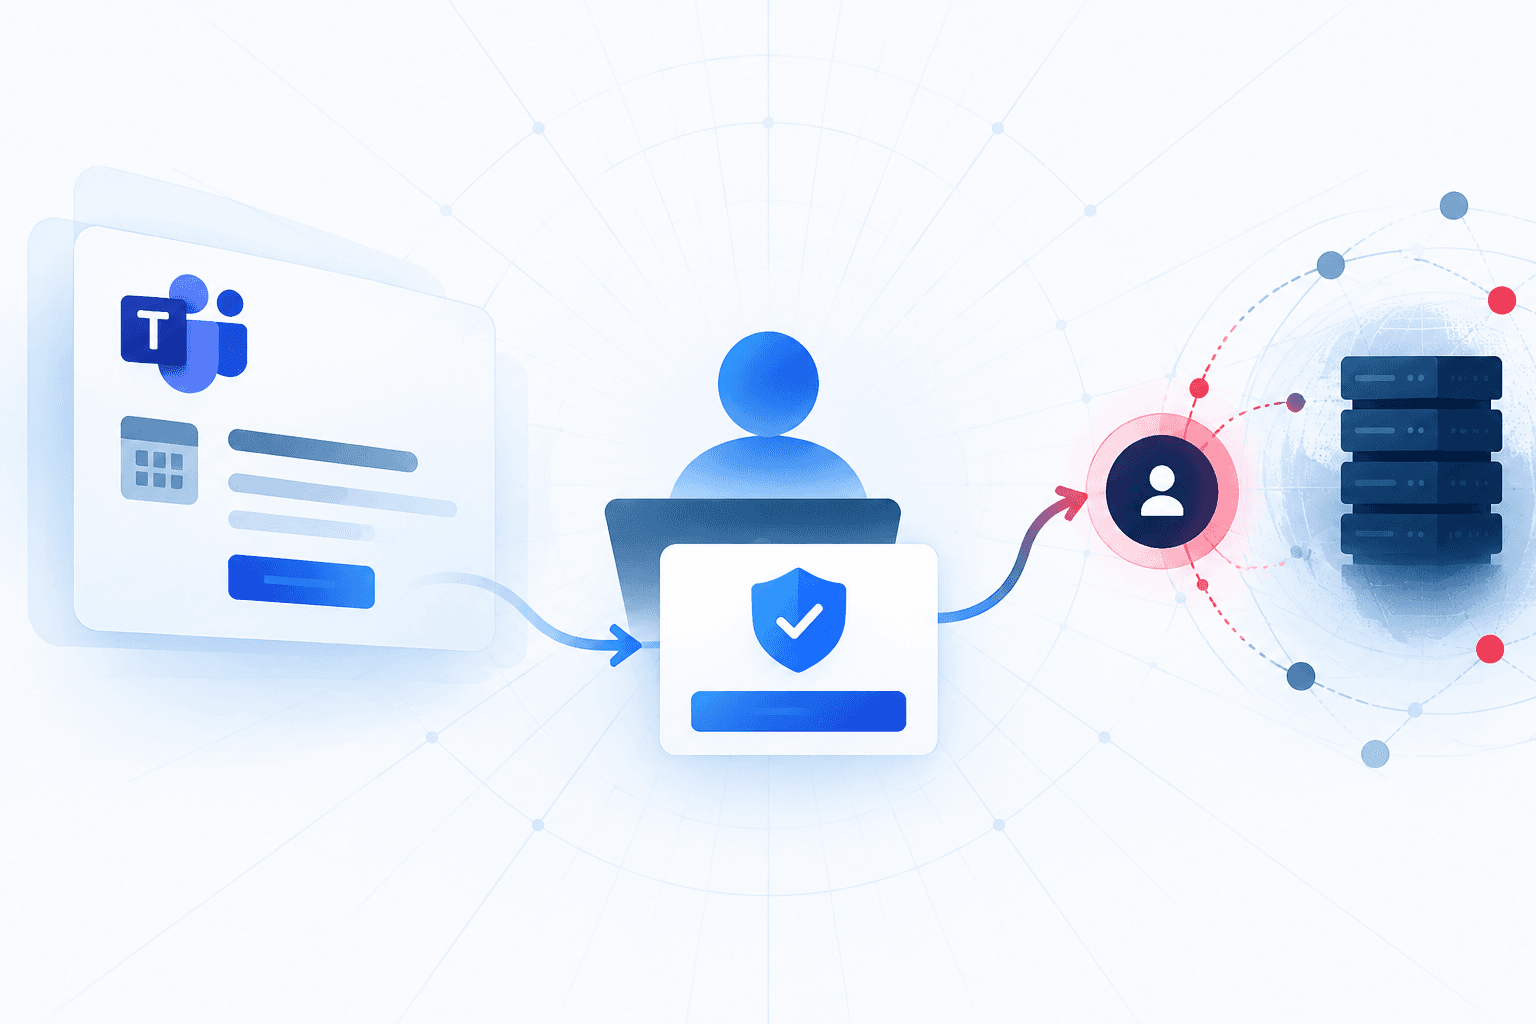
Attackers used a fake Microsoft Teams meeting scheduler to trick an employee at a construction company into authorizing an attacker-controlled sign-in through Microsoft’s device code authentication flow. The campaign impersonated a senior executive at another construction firm and routed the victim through a Google share link to conceal the phishing destination from email URL reputation checks. A code presented as a meeting booking reference was entered into Microsoft’s genuine sign-in page, granting the attacker a valid session token before Huntress’s security operations center identified the incident.
The phishing kit delivered encrypted content through JavaScript, automatically retried after authentication errors, and used a residential proxy to evade detection and sustain the deception. The attack illustrates how a legitimate authentication page can enable account compromise when users are persuaded to authorize a device they do not control. Huntress recommends restricting unnecessary device code authentication, deploying phishing-resistant MFA, monitoring unusual sign-ins, and investigating persistence mechanisms after compromise.