Mallory
← Back to News
ransomware-tooling-evolutionransomware-group-operationpersistence-methodcybercrime-service-ecosystem

Beast Ransomware Hides “666” Control Panel to Encrypt Windows and Network Shares

Malware Intelligence · 2 sources · Updated 5d ago · First seen Nov 13, 2026
Beast Ransomware Hides “666” Control Panel to Encrypt Windows and Network Shares

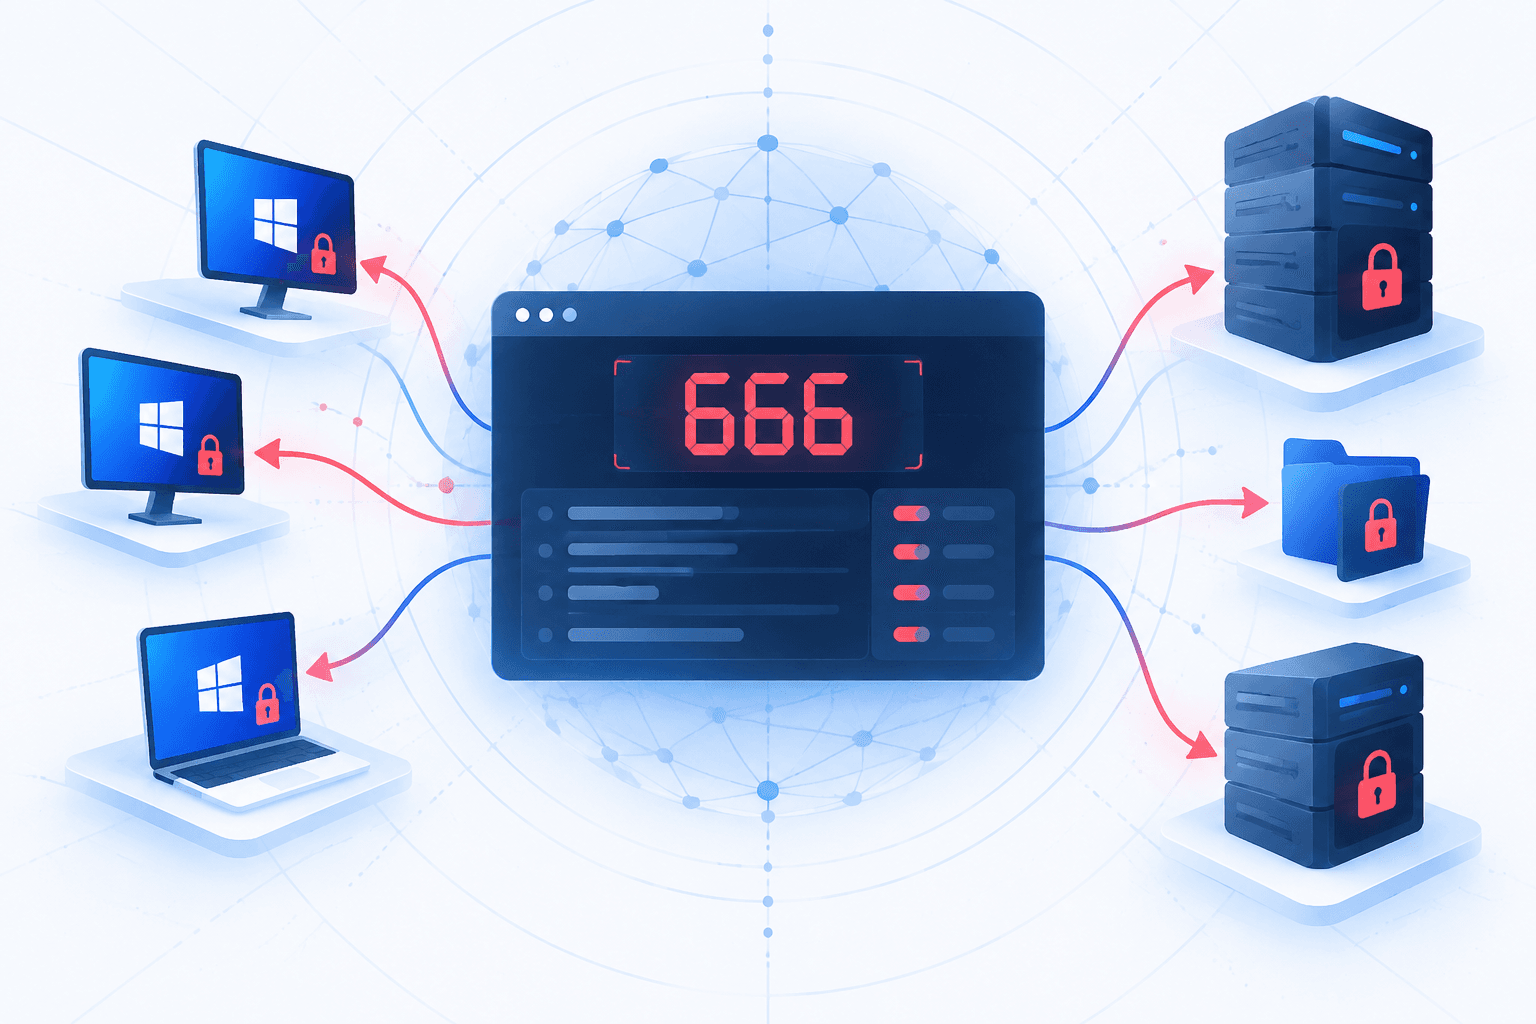
AttackIQ’s analysis of a 32-bit Windows Beast ransomware sample revealed a hidden graphical control panel that allows attackers to select encryption targets and control execution interactively. The panel opens by holding Alt+Ctrl and typing “666.” Beast discovers network shares, establishes user-level registry persistence, terminates security and backup-related processes and services, and can delete Volume Shadow Copies when administrative privileges are available. It combines ChaCha20 and Curve25519 with intermittent encryption and sends encryption-start and completion notifications through a public IP-logging service.

Beast emerged on the RAMP forum in June 2024 as a ransomware-as-a-service operation advertising an offline builder for Windows, NAS devices, and VMware ESXi servers; the analyzed sample specifically demonstrates its Windows capabilities. Symantec and Carbon Black have associated Beast with Hyadina, while Symantec reported a related, code-sharing operation named GodDamn Ransomware in July 2026. The findings highlight the importance of monitoring unusual network-share enumeration, registry persistence, backup-service disruption, and shadow-copy deletion, alongside protecting recovery copies from compromised endpoints.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

7 events · Mar 2022 – Oct 23, 2026
  1. Reported Nov 13, 20265d ago

    AttackIQ releases a Beast ransomware emulation

    AttackIQ released a Beast emulation to help security teams test whether their controls detect the ransomware's behavior.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
  2. Oct 23, 202626d ago

    AttackIQ publishes analysis revealing Beast's hidden encryption control panel

    AttackIQ published reverse engineering of a 32-bit Windows Beast sample, revealing a hidden graphical panel opened by pressing ALT+CTRL and typing 666 that allows interactive target selection and encryption control. The analysis also detailed SMB share discovery, user-level registry persistence, security and backup software termination, shadow-copy deletion, and intermittent encryption using ChaCha20 and Curve25519.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
  3. Aug 30, 20263mo ago

    Activity recorded on the original Beast leak site

    The original Beast leak site recorded activity on August 30, 2026, the latest activity identified in the references.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
  4. Jul 2026

    Symantec reports Beast-linked group's return as GodDamn Ransomware

    Symantec reported that the group associated with Beast had returned under the GodDamn Ransomware name, using ransomware that shares substantial code with Beast. Symantec and Carbon Black associate Beast with the actor Hyadina.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
  5. Aug 2024

    Beast operators begin promoting a multiplatform offline builder

    Beast operators began advertising an offline builder capable of generating ransomware payloads for Windows, NAS devices, and VMware ESXi servers.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
  6. Jun 2024

    Beast ransomware-as-a-service appears on RAMP

    Beast appeared on the RAMP underground forum as a ransomware-as-a-service operation.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
  7. Mar 2022

    Monster ransomware offered for sale on RAMP

    Monster ransomware was sold on the RAMP underground forum. Beast is reportedly its successor.

    Beast Ransomware Uses Hidden '666' Control Panel to Encrypt Windows Systems and Network Shares
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Malware

1 linked

Affected products

1 linked
Windows

Observables

4 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.