Mallory
← Back to News
internet-exposed-serviceendpoint-security-bypassloader-delivery-mechanismcommand-and-control-method

Attackers Abuse Exposed GeoVision Camera Software to Deploy XMRig at 13 Organizations

Active Exploitation · 6 sources · Updated 6h ago · First seen Nov 13, 2026
Attackers Abuse Exposed GeoVision Camera Software to Deploy XMRig at 13 Organizations

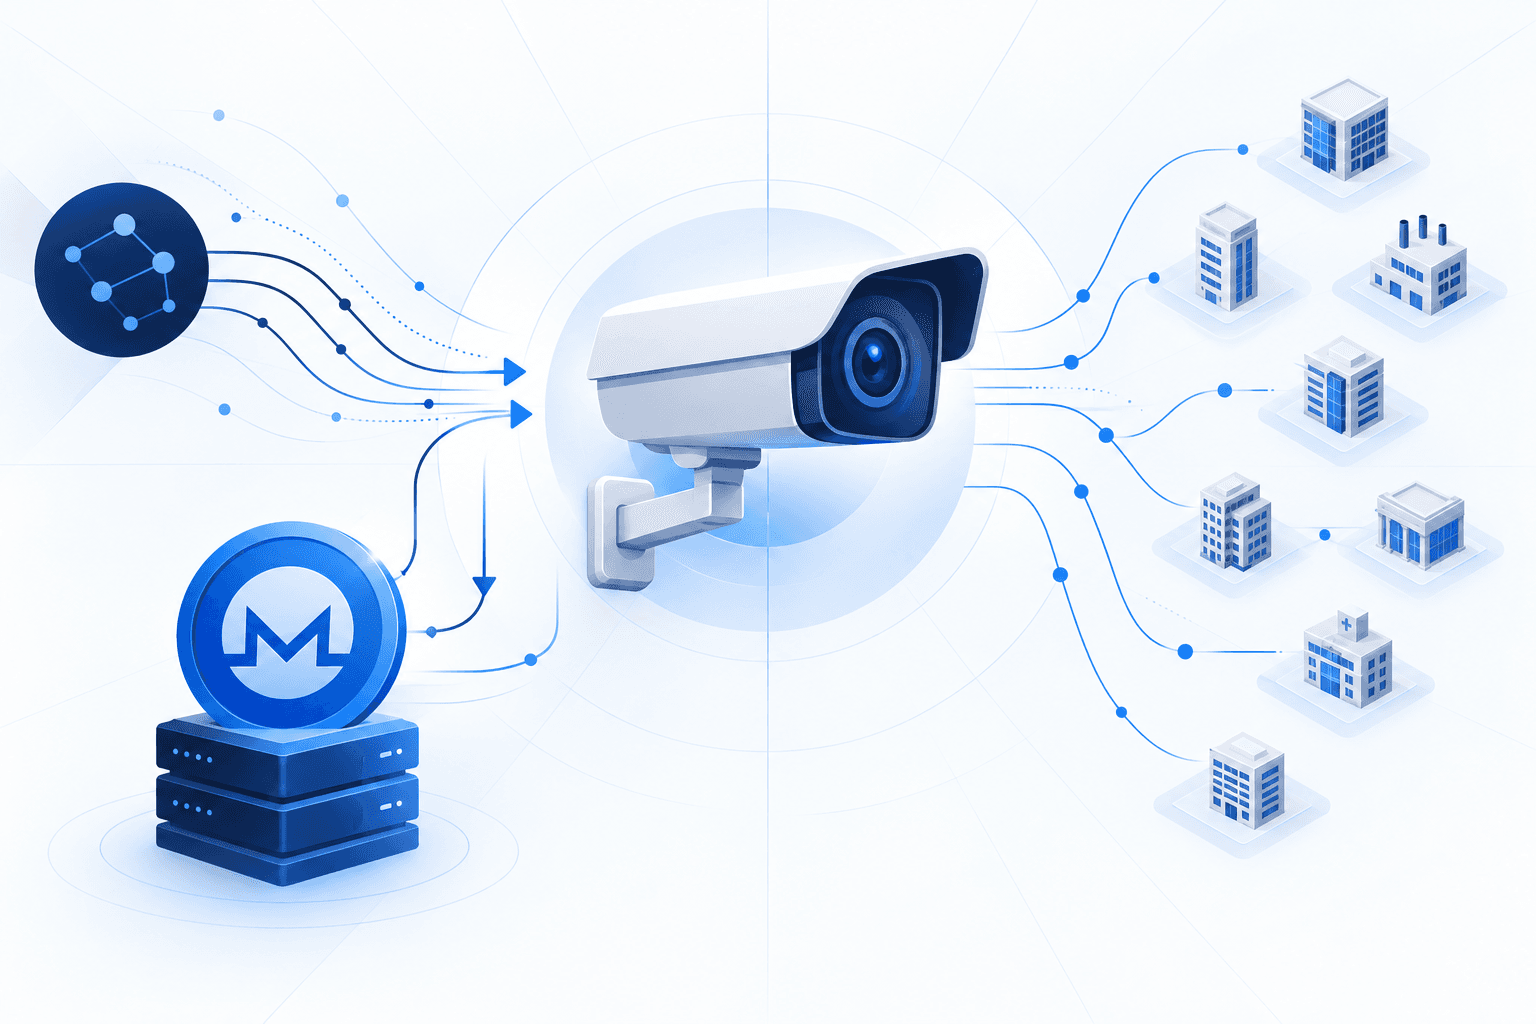
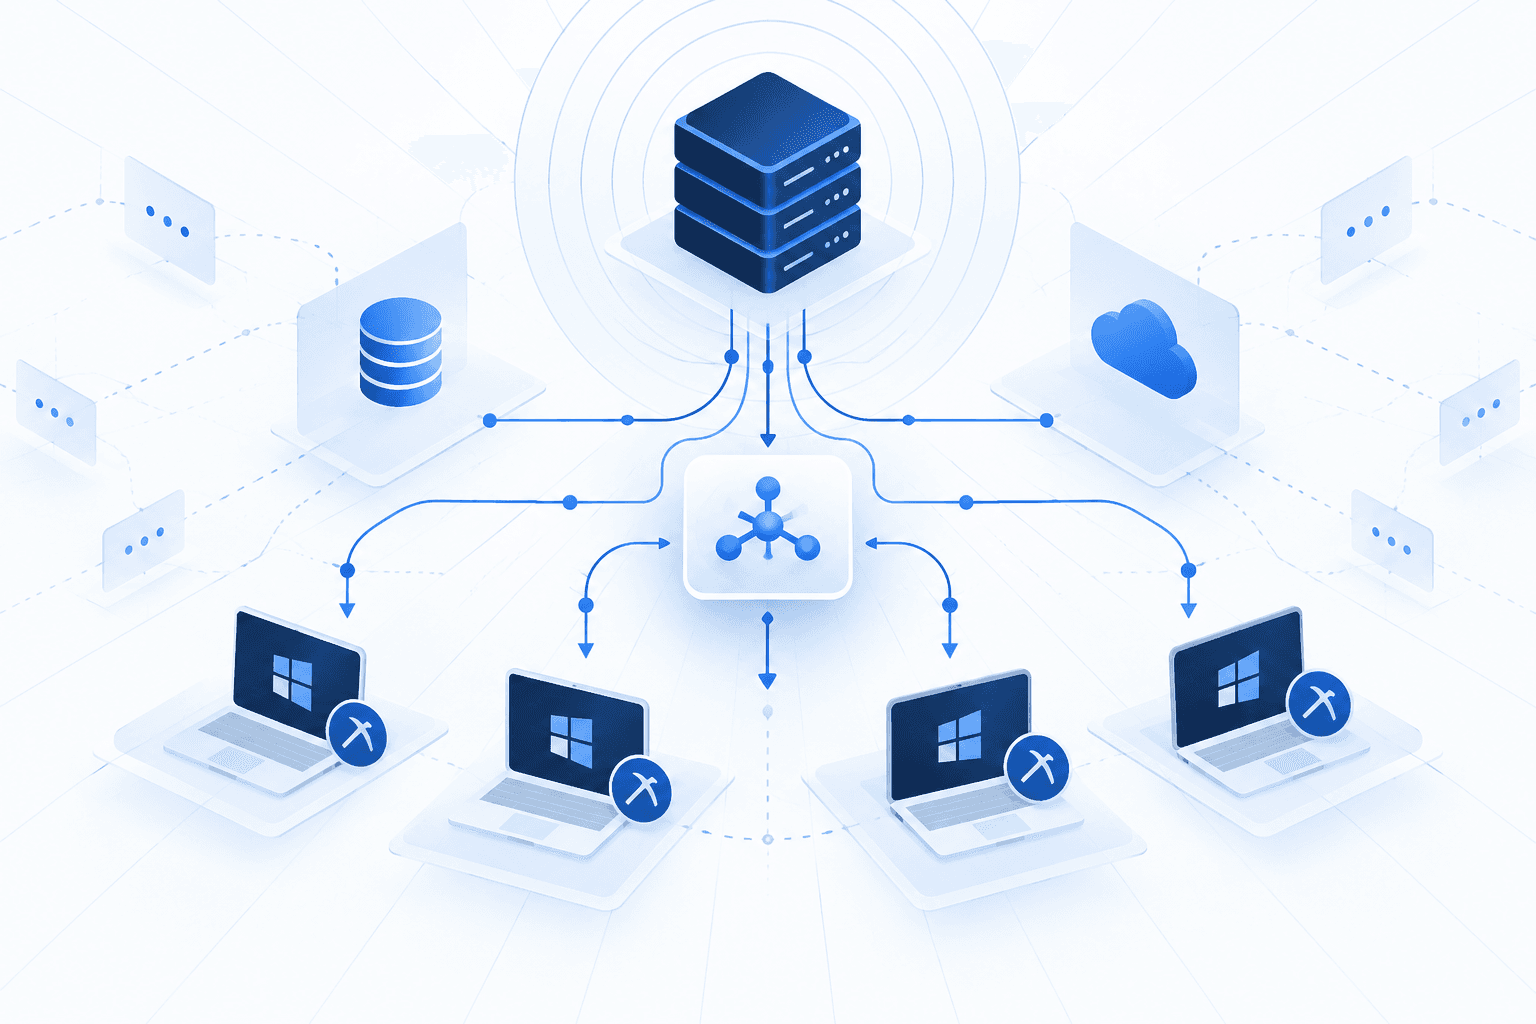
Attackers compromised Windows systems at 13 organizations across multiple industries through internet-exposed GeoVision surveillance software and deployed XMRig cryptocurrency miners, according to Huntress. Activity began November 8, with most intrusions occurring November 8–10. Investigators identified GV-VMS version 17.4.8.0 on a sample of affected hosts and assessed exploitation of a known unauthenticated remote-code-execution vulnerability as the most likely entry method, although the specific CVE remains unconfirmed.

The attackers used PowerShell scripts, a previously abused vulnerable kernel driver, and Windows Image File Execution Options debugger hijacks to interfere with Microsoft Defender and other security protections. A custom Go loader used BitTorrent Mainline DHT and PKARR to discover updated server addresses, complicating infrastructure disruption; some hosts also had scheduled tasks for persistence. The loader could deliver additional payloads, but only XMRig delivery was observed. Huntress recommends restricting internet access to GeoVision interfaces, investigating command shells launched by GeoVision services and suspicious network activity, and isolating compromised hosts while preserving evidence.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Apr 2026 – Nov 8, 2026
  1. Reported Nov 16, 20261d ago

    Huntress links sampled installations to known-vulnerable GV-VMS version

    Following an initial advisory that did not identify a vulnerability or product version, Huntress said sampled affected hosts ran GV-VMS 17.4.8.0 and assessed exploitation of a known flaw as the most likely entry method. Investigators had not determined which of the three remote-code-execution CVEs was exploited.

    Unpatched GeoVision camera software gave cryptojackers a side door into 13 organizations - Help Net Security
  2. Reported Nov 13, 20264d ago

    Huntress details security tampering and resilient Go loader

    Huntress documented PowerShell scripts, a vulnerable kernel driver and Image File Execution Options hijacks used to interfere with Windows security components. Its analysis also identified a Go loader using BitTorrent Mainline DHT and PKARR for server discovery, scheduled-task persistence on some hosts, and XMRig delivery.

    Hackers exploit exposed GeoVision CCTV software to disable Defender and deploy cryptominers - IT Security Guru
  3. Nov 8, 202610d ago

    Huntress first observes GeoVision cryptomining campaign

    Huntress first observed attackers compromising Windows machines through internet-exposed GeoVision software, attempting to disable security protections and installing XMRig. The campaign affected 13 organizations across multiple industries, with most intrusions occurring November 8–10 and activity continuing over the following week.

    Hackers exploit exposed GeoVision CCTV software to disable Defender and deploy cryptominers - IT Security Guru
  4. Nov 7, 202611d ago

    Attack-linked cctv-update[.]top domain registered

    The domain cctv-update[.]top was registered one day before the observed attacks began. The campaign’s custom Go loader subsequently contacted infrastructure linked to this domain.

    Hackers exploit exposed GeoVision CCTV software to disable Defender and deploy cryptominers - IT Security Guru
  5. Apr 2026

    GeoVision discloses three unauthenticated remote-code-execution flaws

    GeoVision’s April 2026 advisory identified three unauthenticated remote-code-execution vulnerabilities in WebCam Server functionality affecting GV-VMS 17.4.8.0. The advisory identified V17.4.8.58 as the fixed release.

    Unpatched GeoVision camera software gave cryptojackers a side door into 13 organizations - Help Net Security
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Affected products

2 linked
WindowsGv-Vms

Organizations

1 linked
Geovision

Observables

4 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.