Leaked Fireworks AI Key Enabled Backdoored Claude Code Extensions in Cursor
Supply Chain Risk · 6 sources · Updated 3h ago · First seen Nov 14, 2026
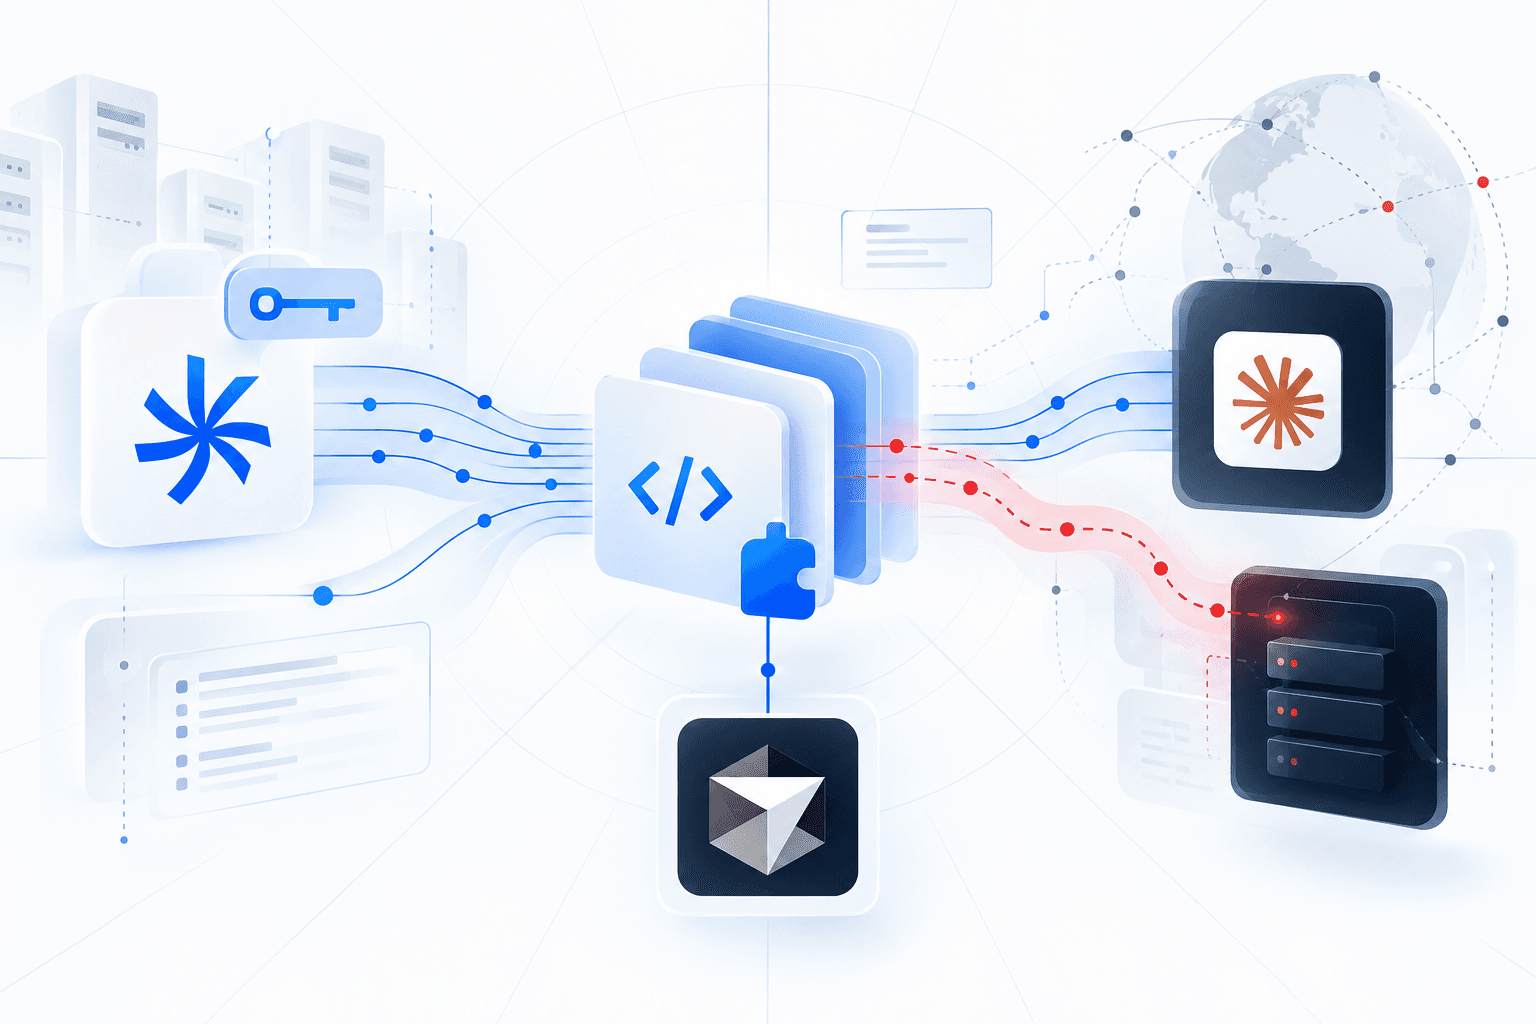
Cursor traced its October breach to an access key exposed by Fireworks AI, which allowed an attacker to steal historical coding-agent records and harvest additional credentials. On October 29, the attacker used a stolen credential to insert backdoored Claude Code extensions directly into Cursor’s marketplace cache. Up to 5,000 users potentially received malicious builds during roughly 11 hours; that figure does not establish how many backdoors successfully connected. Anthropic and Open VSX were not the source of the malicious packages.
The malware collected host information, added an SSH key, and attempted persistent reverse SSH connections. Cursor said coding errors and insufficient privileges prevented remote login on most hosts. The company revoked vendor access, rotated credentials, rebuilt its extension marketplace, and redeployed production infrastructure as a precaution, and believes the incident is contained. Privacy Mode prompts, customer code repositories, and official Cursor updates were unaffected. Affected developers should investigate endpoints for unauthorized SSH keys and persistence, because uninstalling the extension alone may not remove the attacker’s foothold.