Hijacked Bitly Links Redirect Visitors From Old Brand and Trump Posts
Vulnerability Disclosure · 6 sources · Updated 1d ago · First seen Nov 15, 2026
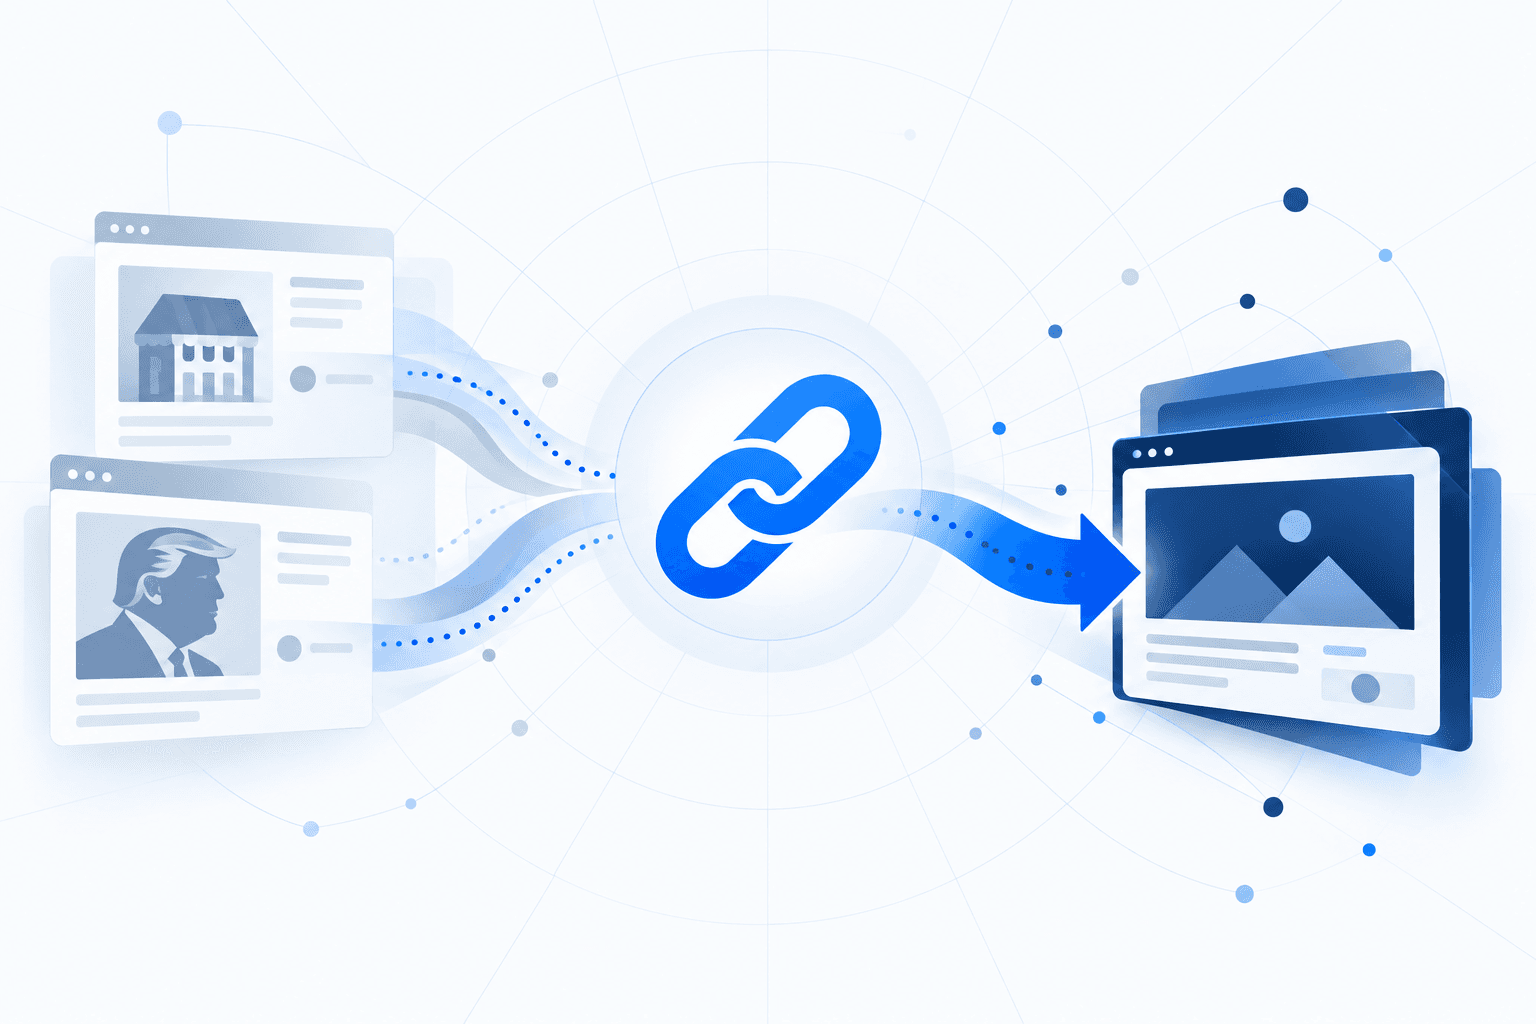
Attackers hijacked expired Bitly links in genuine social media posts, redirecting visitors without editing the posts or compromising the accounts that published them. Links in McDonald’s and Burger King tweets from 2011 were redirected to unrelated Wikipedia articles, according to Ransomnews and Malwarebytes. Ransomnews also examined 97 Bitly links in Donald Trump’s archived tweets: 56 had creation dates later than the posts containing them, and seven of those re-created links led to unrelated destinations, including two domains resembling cryptocurrency services. One of the 97 links was blocked as malicious or spam.
Bitly attributed the incident to a flaw involving expired links, suspended the accounts involved, and said it was disabling affected links. The reported reuse conflicts with Bitly’s stated policy that link endings cannot be reused and follows a vulnerability reportedly fixed in 2025; the references do not establish whether the flaws are related. Although the reported brand redirects led to Wikipedia, the technique could exploit trusted accounts’ credibility to distribute phishing pages, fake promotions, or malicious downloads. Organizations should audit shortened links in historical posts and remove or replace links whose destinations they no longer control.