Amazon Uncovers AI Agents Targeting Exposed AI Apps to Steal Provider API Keys
Emerging Technology Risk · 8 sources · Updated 2h ago · First seen Oct 8, 2026
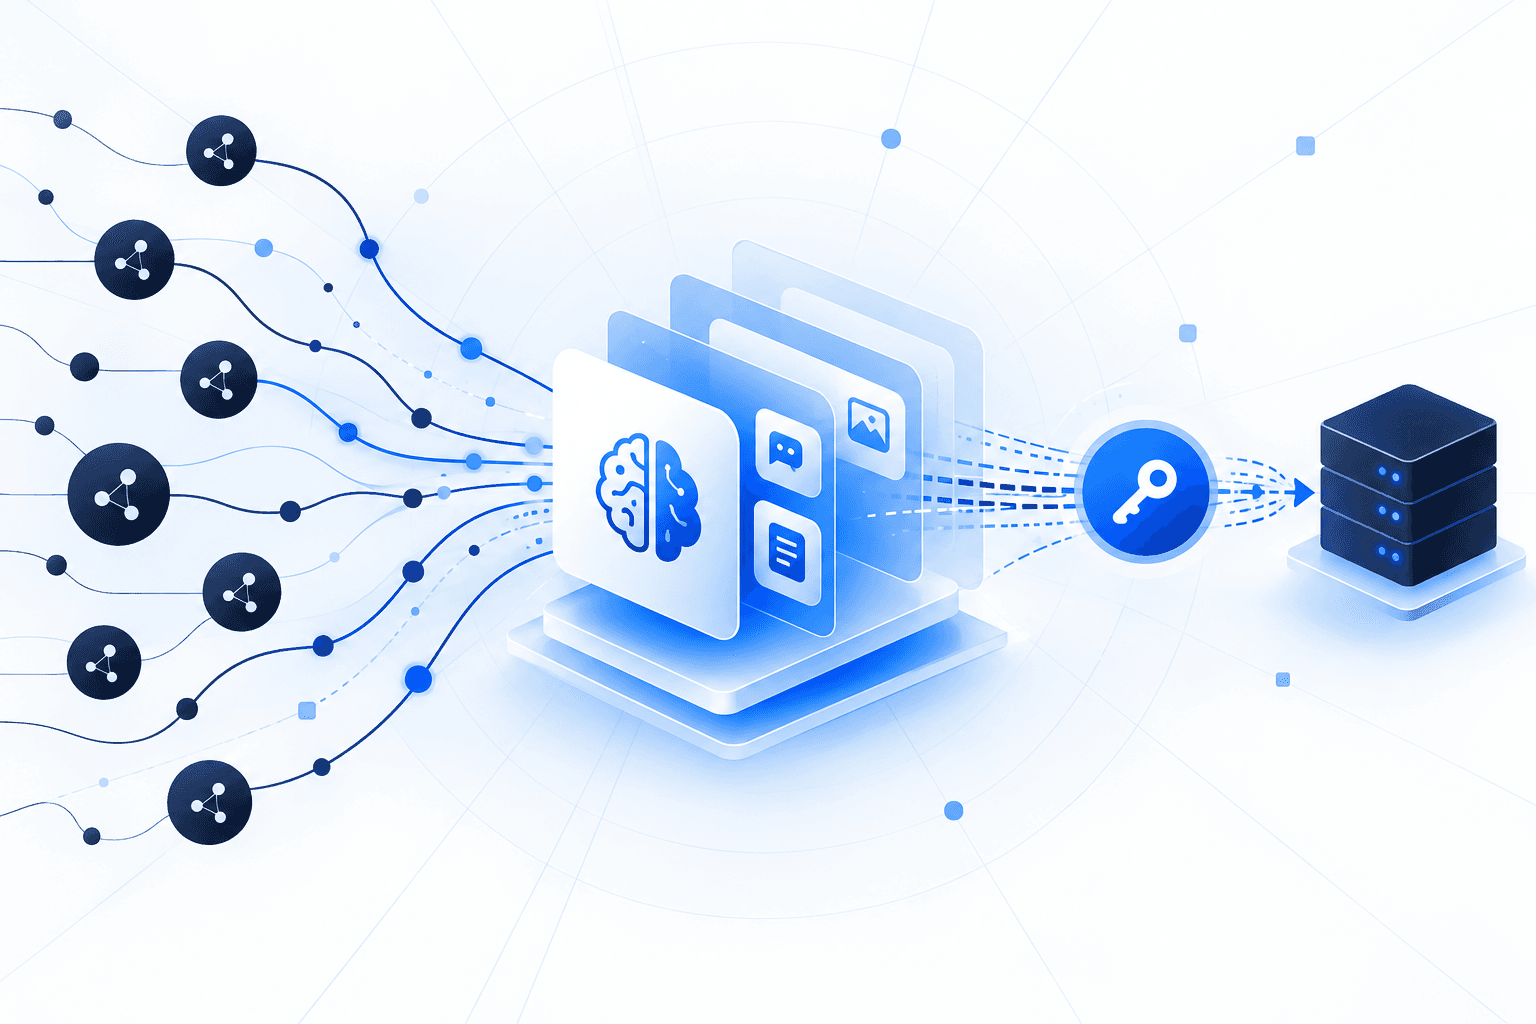
Amazon captured attacker-agent records describing campaigns to steal AI provider API keys from internet-exposed applications and reuse that access to power further credential hunting. Targets included LiteLLM, Dify, One API, Langflow, and RAGFlow, with playbooks covering default credentials, exposed secrets, authentication bypasses, server-side request forgery, and known vulnerabilities. Amazon assessed with moderate confidence that the agents used ARTEX and that the operators represented separate China-linked groups, but it could not independently verify the reported compromises. The records also described attempted cryptocurrency-exchange identity-verification bypasses using deepfakes.
Separate research illustrates related abuse of exposed AI infrastructure. Zenity's honeypots captured three operators using exposed Ollama and LiteLLM endpoints as backends for offensive tooling, including Strix, HexStrike AI, and an OpenAI Codex agent, without needing a software exploit. Separately, Cloudflare investigated ARTEX activity involving a compromised, broadly privileged CI/CD API token and 400 database dump requests in one hour, although it did not confirm whether data was returned. Defenders should patch exposed AI applications, authenticate and restrict administrative and inference endpoints, rotate exposed provider keys, limit API-token privileges, and monitor unusual inference consumption and database access.