Mallory
← Back to News
endpoint-software-vulnerabilityinitial-access-methodidentity-impersonation-fraud

Fake Crypto-Exchange Sessions Bait ScreenConnect Technicians in Suspected Exploit Trap

Vulnerability Disclosure · 5 sources · Updated 49m ago · First seen Nov 16, 2026
Fake Crypto-Exchange Sessions Bait ScreenConnect Technicians in Suspected Exploit Trap

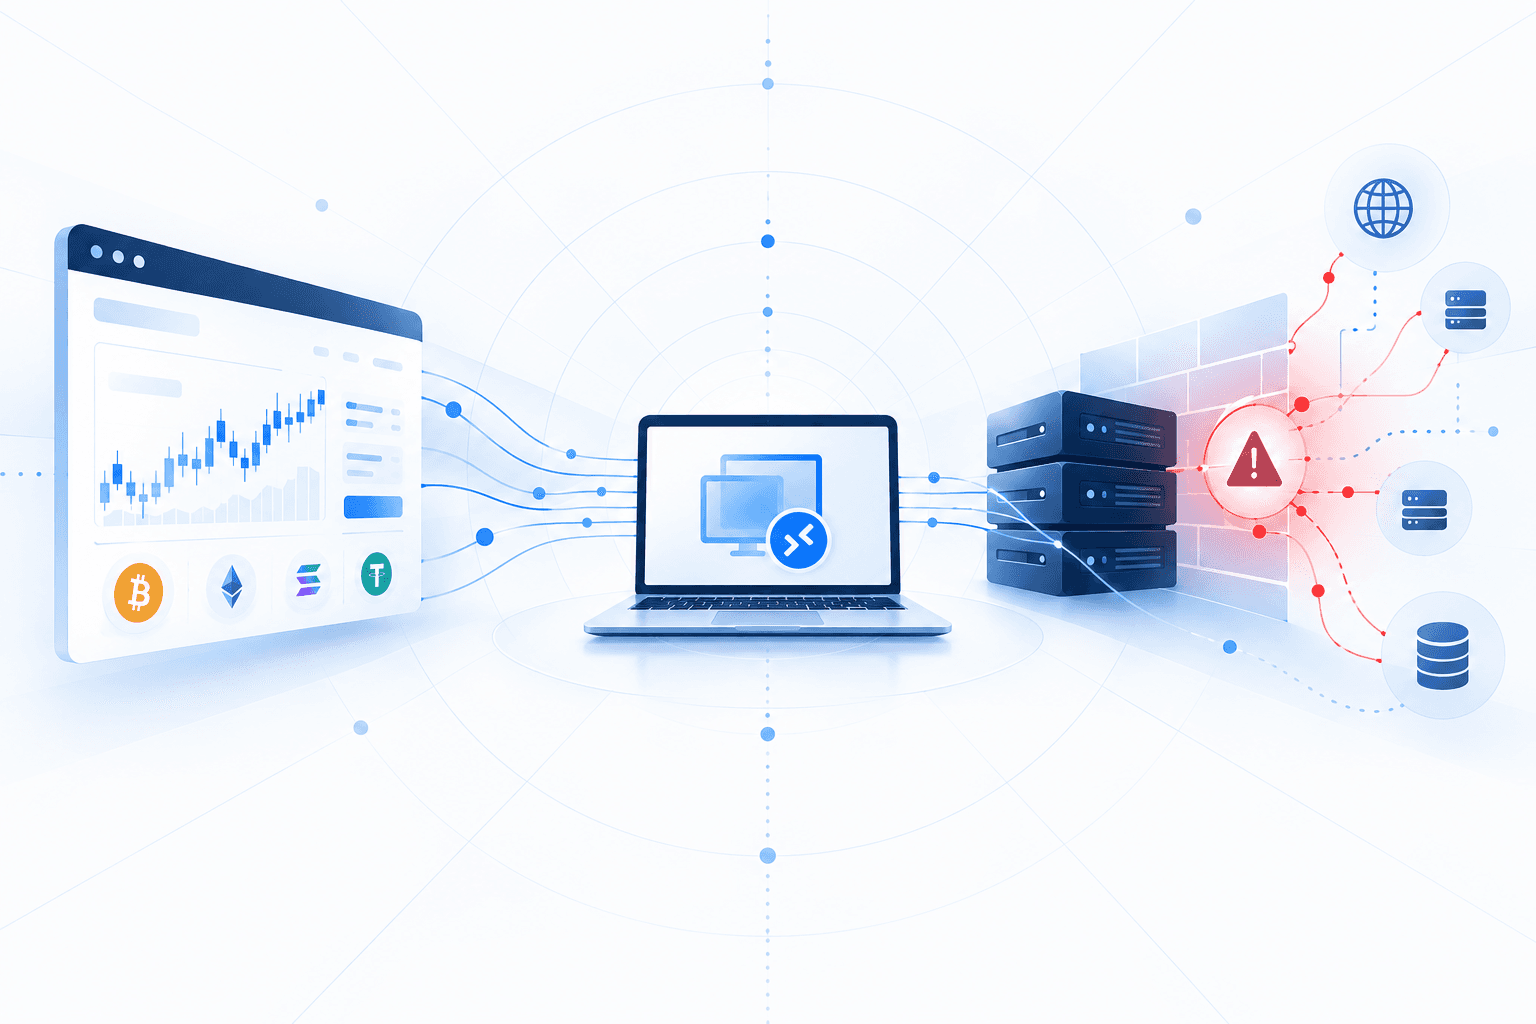
An unknown operator planted more than 2,000 fake guest sessions on self-hosted ScreenConnect servers, impersonating computers associated with cryptocurrency exchanges including Binance and KuCoin. Huntress observed the activity on at least 118 servers across 109 organizations beginning November 3. A scripted emulator maintains the sessions, apparently to lure IT technicians into connecting to the counterfeit machines.

Huntress’s leading hypothesis is that the sessions could target unpatched technician clients through CVE-2026-84869, a critical vulnerability that allows a malicious guest to run a file on the technician’s client. Some technicians opened the sessions, and one interaction raised concerns about possible credential exposure, but Huntress observed no exploitation, confirmed compromises, or losses. Organizations should update technician clients to version 26.6.5 or later, preserve session evidence before removing fake sessions, investigate technician interactions, and restrict access to ScreenConnect installers.
Do you run this?See affected versions and whether adversaries are exploiting it.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Oct 20, 2026 – Nov 12, 2026
  1. Reported Nov 16, 20261d ago

    Huntress identifies session emulator and warns of potential client-exploitation trap

    Huntress determined that a scripted emulator impersonated Windows ScreenConnect clients, with approximately 97.8% of cryptocurrency-named connections originating from one IONOS-hosted IP address. Researchers assessed that the sessions could lure technicians into exposure to CVE-2026-84869, but observed no exploitation, file transfers, command execution, or data sent from the fake sessions.

    Fake "Binance" and "KuCoin" machines planted on ScreenConnect servers in apparent trap for IT technicians - IT Security Guru
  2. Reported Nov 16, 20261d ago

    Technicians connect to fake sessions, raising possible credential-exposure concerns

    Several technicians opened the fake sessions, with most observed connections lasting less than 30 seconds. One technician entered text twice, prompting Huntress to treat the interaction as possible credential exposure; no confirmed compromises or losses were reported.

    Fake "Binance" and "KuCoin" machines planted on ScreenConnect servers in apparent trap for IT technicians - IT Security Guru
  3. Nov 12, 20266d ago

    ScreenConnect exploit reportedly compromises MSP technician workstation in nine seconds

    Huntress reportedly observed attackers exploit CVE-2026-84869 to compromise an MSP technician’s workstation in nine seconds. The execution chain ran update_224ac089.bat and deployed a rebranded ScreenConnect client that connected to the attacker-controlled relay masterdarky[.]com:8041.

    CVE-2026-84869 : exploitation active de ScreenConnect pour compromettre les techniciens MSP | CyberVeille
  4. Nov 3, 202615d ago

    Fake cryptocurrency-exchange sessions appear on ScreenConnect servers

    Beginning November 3, an unknown operator planted more than 2,000 fake guest sessions across at least 118 self-hosted ScreenConnect servers belonging to 109 organisations monitored by Huntress. The sessions impersonated cryptocurrency-exchange computers using names such as “LAPTOP-BINANCE” and “KUCOIN-SRV,” trading-desktop thumbnails, and persistent online status.

    Fake "Binance" and "KuCoin" machines planted on ScreenConnect servers in apparent trap for IT technicians - IT Security Guru
  5. Oct 20, 202629d ago

    Mass ScreenConnect run-file campaign targets 42 MSP servers

    Beginning October 20, Huntress observed at least 688,000 guest run-file requests for update*.bat files targeting 42 MSP ScreenConnect servers from 29 IP addresses. Attackers staged requests in support sessions to exploit CVE-2026-84869 when technicians connected, causing vulnerable technician clients to execute guest-pushed batch files without confirmation.

    Critical MSP ScreenConnect bug exploits the technician’s computer | news | SC Media
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

1 linked
Screenconnect

Observables

36 linked

Indicator values are masked on this page. View all 36 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
Check Your Exposure
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.