Mallory
← Back to News
vendor-distribution-compromiseloader-delivery-mechanismcommunication-services-sector-threatthird-party-vendor-breach

Poisoned Third-Party JavaScript Exposes Major Websites to Skimmers and iPhone Exploit Loaders

Supply Chain Risk · 14 sources · Updated 25m ago · First seen Nov 16, 2026
Poisoned Third-Party JavaScript Exposes Major Websites to Skimmers and iPhone Exploit Loaders

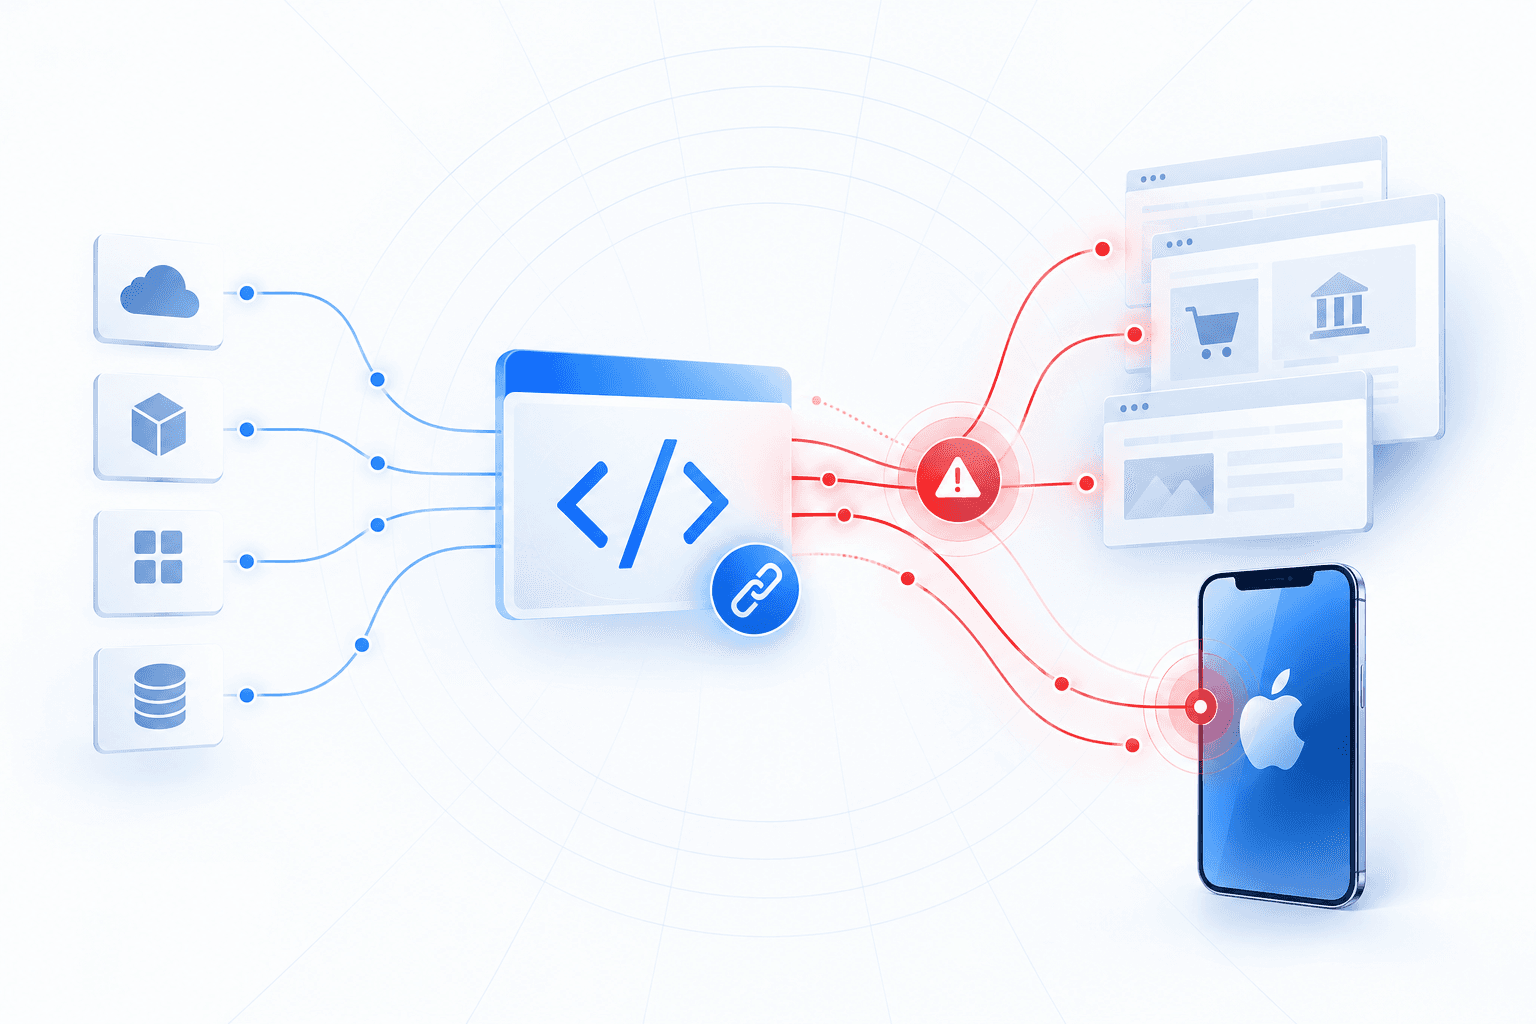
Researchers identified malicious third-party JavaScript reaching major websites through Optimizely, Kissmetrics, StorifyMe and minute-ly endpoints. Hudson Rock and researcher Kirk from Ohey linked 21 named web properties to affected resources, including BBC and Zoom. Payloads supported cryptocurrency-address substitution, payment-card skimming and conditional browser-data collection, alongside delivery infrastructure associated with the Coruna and DarkSword iPhone exploit kits. BBC and HSBC UAE scripts contained complete embedded malicious payloads, meaning blocking external attacker domains alone would not eliminate the threat. Archived scans showed mobile-routing and exploit-entry responses, but did not establish successful exploitation of an actual iPhone. The operators, initial access methods, full exposure window and confirmed theft or device-compromise totals remain unknown. Hudson Rock

Separately, Dutch publishers including Bright.nl and VI.nl disclosed malicious advertising code following unauthorized access on November 1–3 and November 11. They said the code collected visitor information and attempted to exploit outdated iPhones; affected publishers reported removing it and fixing the advertising-system vulnerability. These disclosures do not establish that every affected service shared the same intrusion. Tweakers Beazley Security advised organizations exposed through Optimizely to inspect project JavaScript, remove affected snippets from sensitive pages, block attacker infrastructure, review account access and investigate potential payment-data exposure. Its advisory said Optimizely had not issued a statement or remediation guidance at publication. Beazley Security
Does this reach your builds?Trace attribution and downstream blast radius.
Trace the chain
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

14 events · Nov 2026 – Nov 16, 2026
  1. Reported Nov 16, 20263h ago

    Scott Helme reports 186 websites confirmed infected

    Security researcher Scott Helme reported that 186 websites had been confirmed infected, indicating a broader reported impact than the previously documented 21 named web properties.

    AndreGironda: RT @Scott_Helme: 186 sites confirmed infected so far. These are sites that every person here will know and use. It seem...
  2. Reported Nov 16, 20265h ago

    Mobile dispatchers are linked to Coruna and DarkSword-labelled infrastructure

    Kirk associated the A8 and JIUJIU888 dispatchers with Coruna and identified D11 as a DarkSword-labelled delivery entry whose later stages were not fully inspected. Shared routing infrastructure connected the financial-theft and mobile-delivery paths, but did not establish a common operator, successful device compromise or a confirmed connection to the Dutch advertising attacks.

    Poisoned Scripts on BBC, Zoom and Other Major Websites Linked to iPhone Exploit Loaders | Hudson Rock
  3. Reported Nov 16, 20265h ago

    BBC and HSBC UAE scripts reveal embedded malicious fallback

    Recovered BBC and HSBC UAE Optimizely scripts contained the same 24,392-byte Base64-encoded malicious fallback, invoked after a remote-script failure or timeout. This meant blocking external attacker domains alone could leave local cryptocurrency-address substitution available, subject to browser execution policies.

    Poisoned Scripts on BBC, Zoom and Other Major Websites Linked to iPhone Exploit Loaders | Hudson Rock
  4. Reported Nov 16, 20265h ago

    Investigation verifies poisoned responses across four script providers

    Hudson Rock and Kirk from Ohey documented malicious response bodies from Optimizely, Kissmetrics, StorifyMe and minute-ly endpoints associated with 21 named web properties, including BBC, Zoom and Fox Sports. Hudson Rock corroborated all 16 poisoned response hashes supplied by Kirk and directly recovered eight poisoned Optimizely assets and one minute-ly loader.

    Poisoned Scripts on BBC, Zoom and Other Major Websites Linked to iPhone Exploit Loaders | Hudson Rock
  5. Nov 16, 20261d ago

    Optimizely cleanup leaves one infected snippet; cryptocurrency theft confirmed

    At 21:52 UTC on November 16, Report URI found malicious code remaining in only 1 of 188 infected Optimizely snippets. It also reported verified cryptocurrency transactions to the attackers, establishing actual financial loss.

    World's Largest Brands Infected With Malware Via Optimizely
  6. Nov 16, 20261d ago

    Cleanup leaves 41 of 188 compromised scripts still infected

    At approximately 21:32 UTC on November 16, Scott Helme reported that 41 of 188 infected script files remained infected during cleanup. Public scans recorded malicious payload requests beginning at 08:28 UTC, establishing an exposure window of at least 13 hours.

    OPTIMJACK: Optimizely-Hosted Scripts Loaded a Crypto Clipper and Card Skimmer on 186 Confirmed Sites - StepSecurity
  7. Nov 16, 20261d ago

    User-agent tests retrieve iPhone-targeting delivery stages

    Tests at 21:08:43 and 21:12:49 UTC using iOS 18.6 and iOS 17.5 Safari user-agent strings retrieved mobile boot scripts, a D11 entry and an A8 entry with packed JavaScript. Because URLScan used headless Chrome rather than Safari WebKit, the results demonstrated routing and stage delivery, not successful iPhone exploitation.

    Poisoned Scripts on BBC, Zoom and Other Major Websites Linked to iPhone Exploit Loaders | Hudson Rock
  8. Nov 16, 20261d ago

    Researchers disclose malicious Optimizely scripts across major websites

    PrivacyAffairs and an independent researcher disclosed injected Optimizely project files, with PrivacyAffairs verifying affected files for Optimizely, NOW TV, CNN, Virgin Media and TalkTalk between 20:33 and 20:36 UTC. The payload included cryptocurrency-address substitution, payment-card skimming, conditional browser-data collection and Apple mobile-device loaders; the independent researcher named the activity OPTIMJACK.

    Emerging Threat: Optimizely Web Experimentation Compromised to Serve Malicious iOS Malware, Card Skimmers and Crypto Clippers
  9. Nov 16, 20261d ago

    Attackers add payment-card skimmer to compromised Optimizely scripts

    At 13:43 UTC on November 16, attackers added a payment-card skimmer that captured card numbers, expiration dates and CVVs from form submissions and sent them to 1688360.cc/card.php. It could capture details in websites' own form fields, but not within hosted payment frames such as Stripe or Adyen.

    Hackers Infect 178 Major Websites via Optimizely to Steal Credit Cards and Target iPhones | Cryptika Cybersecurity
  10. Nov 16, 20261d ago

    Attack infrastructure domain 1688360.cc is registered

    The domain 1688360[.]cc was registered at 05:23 UTC and subsequently served the malicious track.js payload and collection endpoints. PrivacyAffairs also reported that an associated .icu delivery domain was registered at 16:38 UTC that day.

    Emerging Threat: Optimizely Web Experimentation Compromised to Serve Malicious iOS Malware, Card Skimmers and Crypto Clippers
  11. Reported Nov 15, 20262d ago

    Dutch websites announce malicious code removal and advertising-system fix

    Bright.nl and VI.nl warned visitors about the advertising compromise and stated that the malicious code had been removed and the discovered advertising-management vulnerability fixed. Autoblog, GeenStijl and other websites were also affected, but the total number was unknown.

    Bright.nl, VI.nl en andere websites verspreidden iPhone-malware via advertenties - Tweakers
  12. Nov 13, 20264d ago

    Security Bank capture records a poisoned vendor script

    An archived Security Bank capture at 05:42 UTC recorded a poisoned vendor response, the earliest verified observation in the evidence subset examined by Hudson Rock. Additional malicious vendor responses were observed through November 16.

    Poisoned Scripts on BBC, Zoom and Other Major Websites Linked to iPhone Exploit Loaders | Hudson Rock
  13. Nov 11, 20266d ago

    Unauthorized access to the Dutch advertising system recurs

    The affected Dutch websites reported another instance of unauthorized access on November 11. The advertising system belonged to an external software supplier and was managed by a separate advertising service provider, identified by GeenStijl as Next Day Media.

    Bright.nl, VI.nl en andere websites verspreidden iPhone-malware via advertenties - Tweakers
  14. Nov 2026

    Attackers inject malicious advertising code into Dutch websites

    Between November 1 and 3, attackers gained unauthorized access to an advertising system used by Bright.nl, VI.nl and other Dutch websites. Injected advertising code collected visitor information and attempted to exploit outdated iPhones; GeenStijl identified the payload as Coruna.

    Bright.nl, VI.nl en andere websites verspreidden iPhone-malware via advertenties - Tweakers
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

2 linked
IpadosIos

Organizations

42 linked
Virgin MediaOptimizelySalesforceBitlyTricentisGitLabHSBC HoldingsAir FranceZoom CommunicationsBritish Broadcasting Corporation+32 more

Observables

66 linked

Indicator values are masked on this page. View all 66 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See attribution and downstream blast radius, and whether this package or vendor reaches your builds.
Trace the Supply Chain
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.