Mallory
← Back to News
remote-access-implantidentity-impersonation-fraudinitial-access-methodloader-delivery-mechanism

Crypto Wallet Lures Install ScreenConnect for Remote Access

Malware Intelligence · 3 sources · Updated 11h ago · First seen Nov 17, 2026
Crypto Wallet Lures Install ScreenConnect for Remote Access

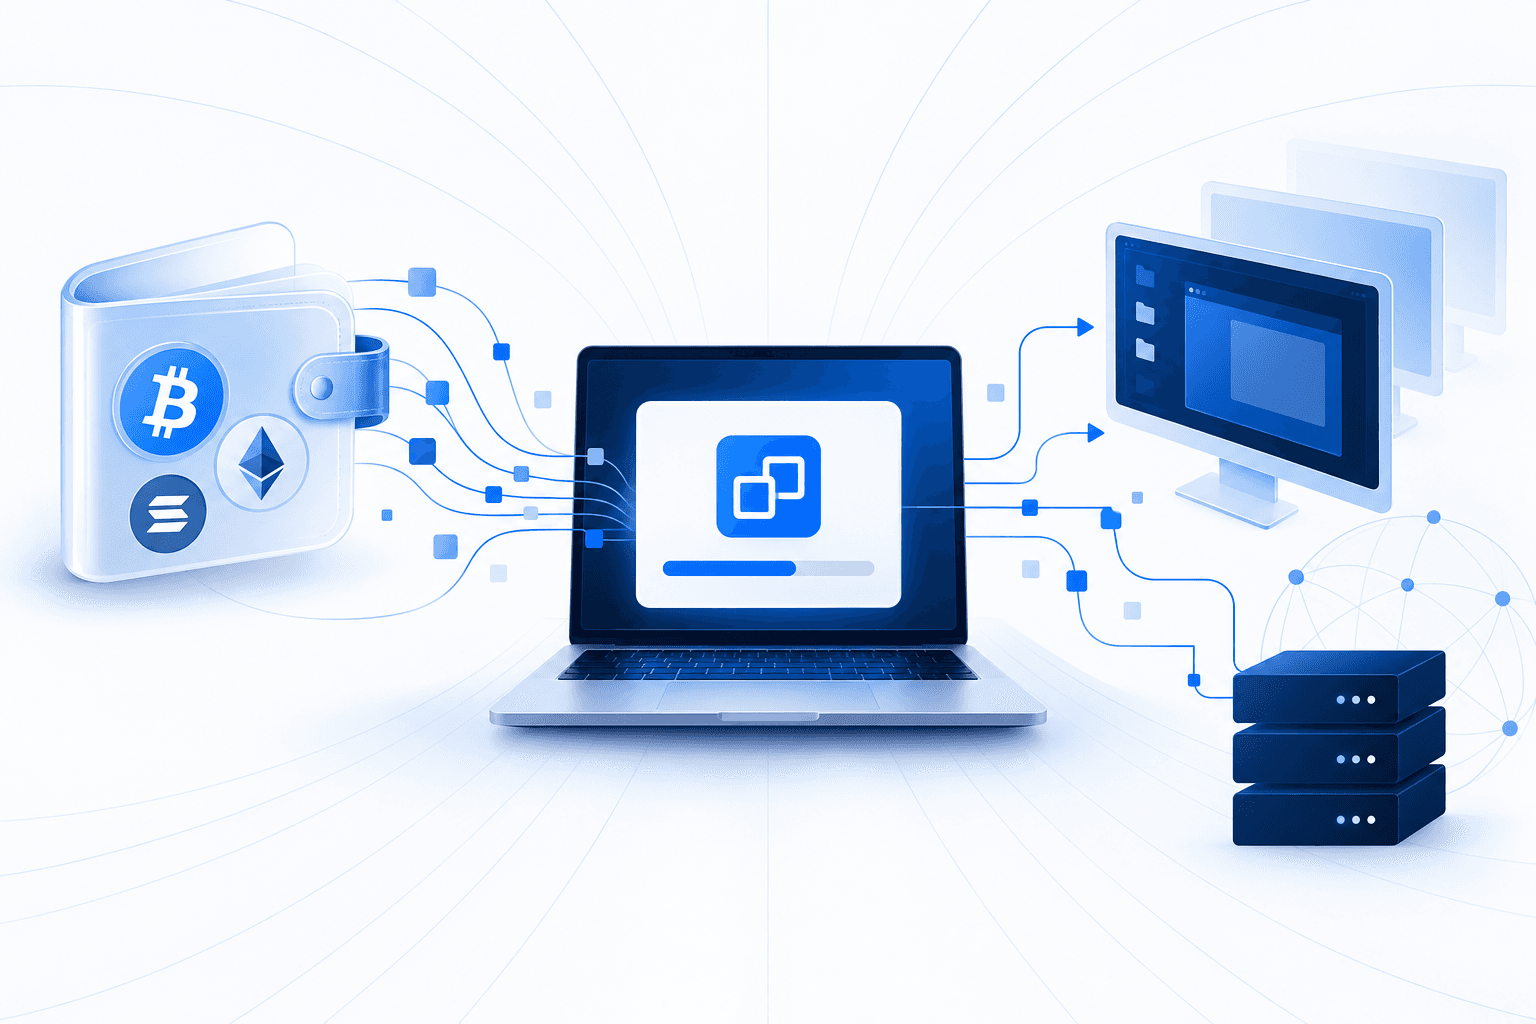
An unattributed campaign is targeting cryptocurrency users, particularly hardware-wallet owners, with branded ZIP archives containing malicious batch files, according to Blaze’s Security Blog. The lures reference Coldcard, Ledger, Pera Algorand Wallet, Revolut, and Xaman. Executing the files installs ConnectWise ScreenConnect, a legitimate remote-support application, as a Windows service that connects to fjksdjfdtitive[.]net over TCP port 8041. Attackers can abuse that access to control affected computers, execute commands, and potentially obtain sensitive information. The report does not establish confirmed cryptocurrency theft or exploitation of a software vulnerability.

Defenders should investigate unauthorized ScreenConnect installations, isolate affected devices, and block the identified attacker infrastructure. Exposed credentials should be reset from a clean device. Any wallet recovery phrases or private keys potentially exposed on an affected computer should be treated as compromised, with remaining assets transferred to a newly generated wallet; hardware-wallet ownership alone does not protect secrets disclosed on a compromised host.

Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event
  1. Reported Nov 17, 202623h ago

    Crypto-wallet lure campaign installs ScreenConnect for unauthorized remote access

    Attackers targeted cryptocurrency users, including hardware-wallet owners, with ZIP archives containing malicious batch files impersonating Coldcard, Ledger, Pera Algorand Wallet, Revolut, and Xaman. Executing the files installs ConnectWise ScreenConnect, which connects to fjksdjfdtitive[.]net over TCP port 8041 and enables remote control and potential information theft; no provider breach or cryptocurrency theft was confirmed.

    Crypto hardware wallet users under attack - Malware Analysis - Malware Analysis, News and Indicators
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

1 linked
Screenconnect

Observables

17 linked

Indicator values are masked on this page. View all 17 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.