Phishing Compromises Luxury Hotel Reservation Inboxes to Enable Refund Fraud
Social Engineering & Fraud · 2 sources · Updated 20h ago · First seen Nov 17, 2026
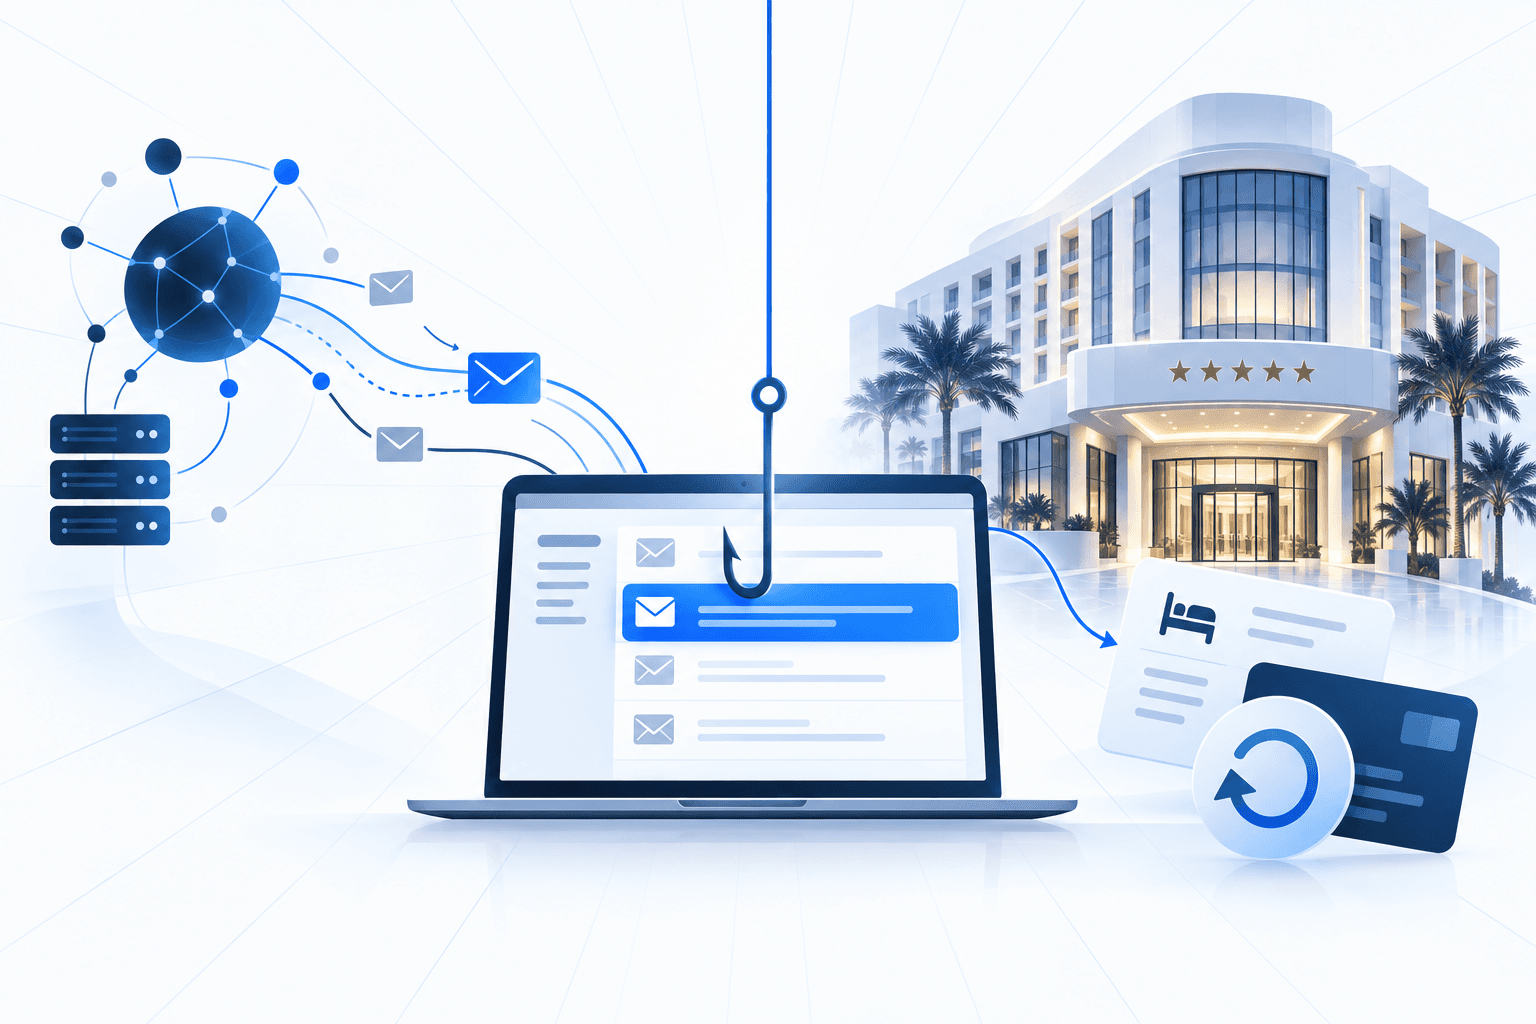
Attackers used fake booking requests to compromise luxury hotel reservation inboxes, then intercepted legitimate refund requests and substituted fraudulent versions that led to unauthorized financial approvals. SC Media reported the scheme, citing an account attributed to Schneier on Security. The attack exploited a routine business workflow: reservation staff must respond to inquiries from unfamiliar senders, making blanket advice to avoid suspicious messages difficult to apply.
The account also identified fragmented security responsibility among hotel property owners, management operators, and global brands as a structural weakness that can leave infrastructure protection without clear accountability. A guest-first service culture compounds the challenge by encouraging employees to accommodate requests. For hotel operators, the incident underscores the importance of independently verifying refund changes and clearly assigning responsibility for reservation-system security, rather than relying solely on employees to recognize phishing.