The Gentlemen Ransomware Targets Enterprises With Cross-Platform Double Extortion
Active Exploitation · 2 sources · Updated 4h ago · First seen Nov 17, 2026
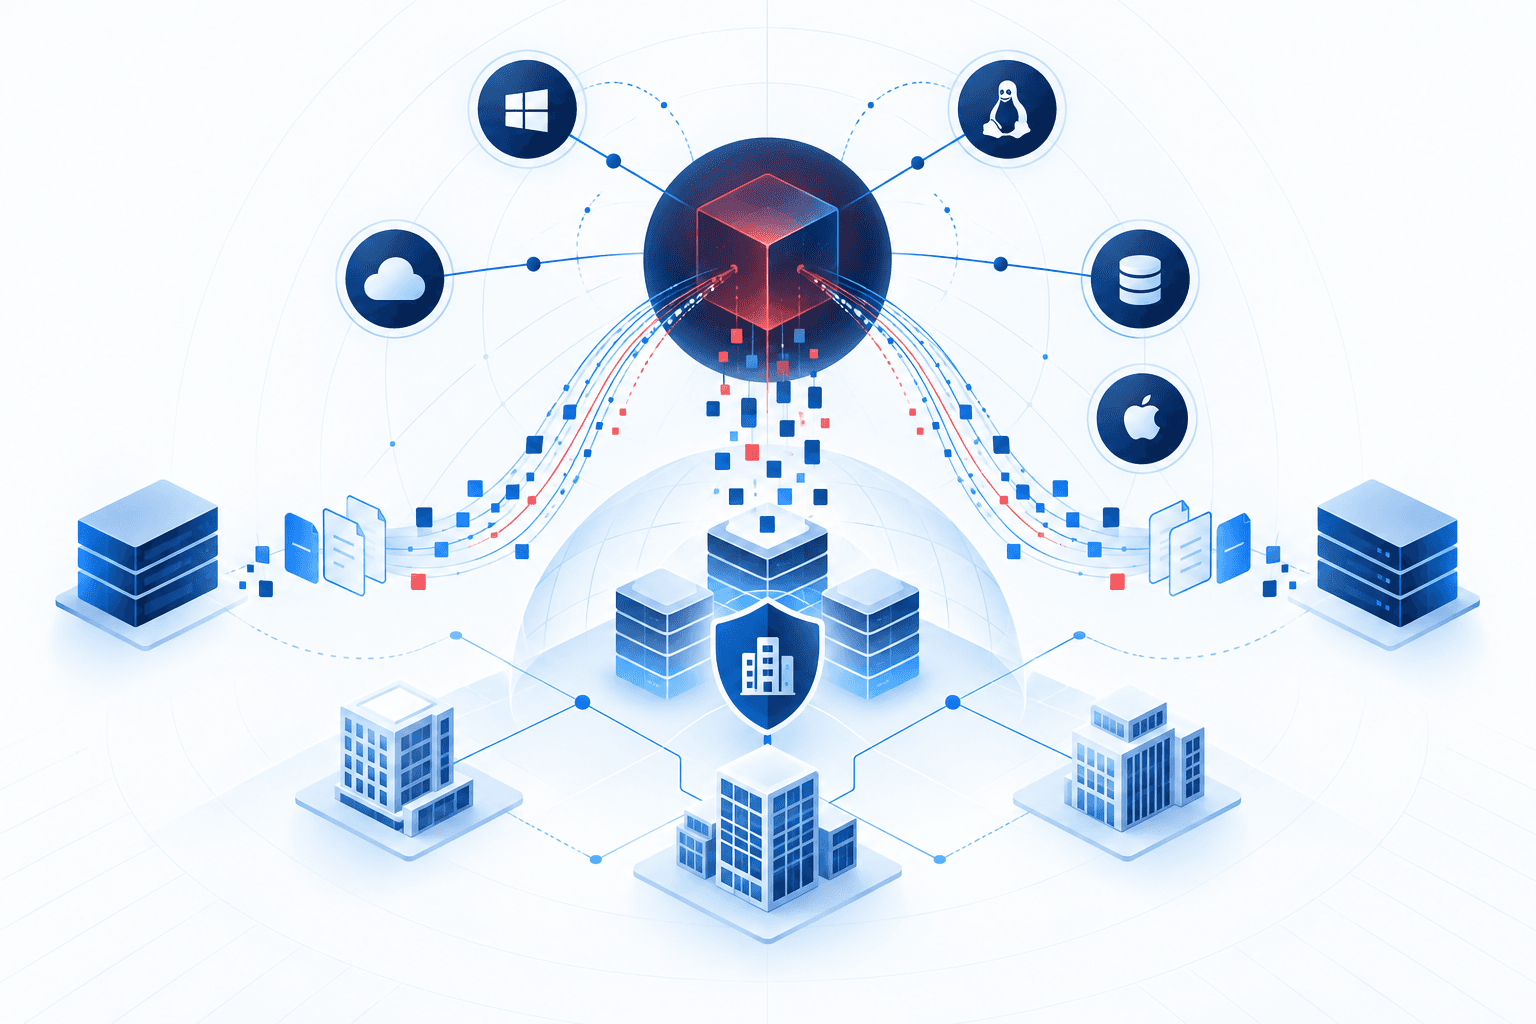
The Gentlemen ransomware-as-a-service operation is targeting organizations worldwide with data theft and file encryption, affecting sectors including healthcare, financial services, manufacturing, logistics, and construction. Reported to have emerged around mid-2025, the group was classified as a critical threat in Gurucul’s November 16 bulletin. Its Go-based ransomware reportedly uses code obfuscation and self-propagation across Windows, Linux, BSD, NAS devices, and VMware ESXi environments. Earlier research from 0xDelta identified the United States, Brazil, Thailand, and India as primary target countries and described affiliate recruitment requiring a $1,500 deposit.
Reported intrusion methods include exploiting vulnerable internet-facing systems, VPNs, and RDP services, as well as using compromised credentials. 0xDelta specifically identified exploitation of FortiGate/FortiOS vulnerability CVE-2024-55591 and vulnerable drivers used to disable security software. Attackers conduct reconnaissance, move laterally, disable security tools, and delete backups before deploying ransomware. Defenders should prioritize patching exposed infrastructure, restricting administrative access, enforcing multifactor authentication, rotating privileged credentials, and monitoring anomalous logins and security-tool tampering. Gurucul’s bulletin provides domain, IP address, and file-hash indicators with corresponding detection queries to support threat hunting.