Fake Shipment ZIP Uses Kingsoft DLL Side-Loading in PureLogs-Linked Malware Chain
Malware Intelligence · 2 sources · Updated 4h ago · First seen Nov 17, 2026
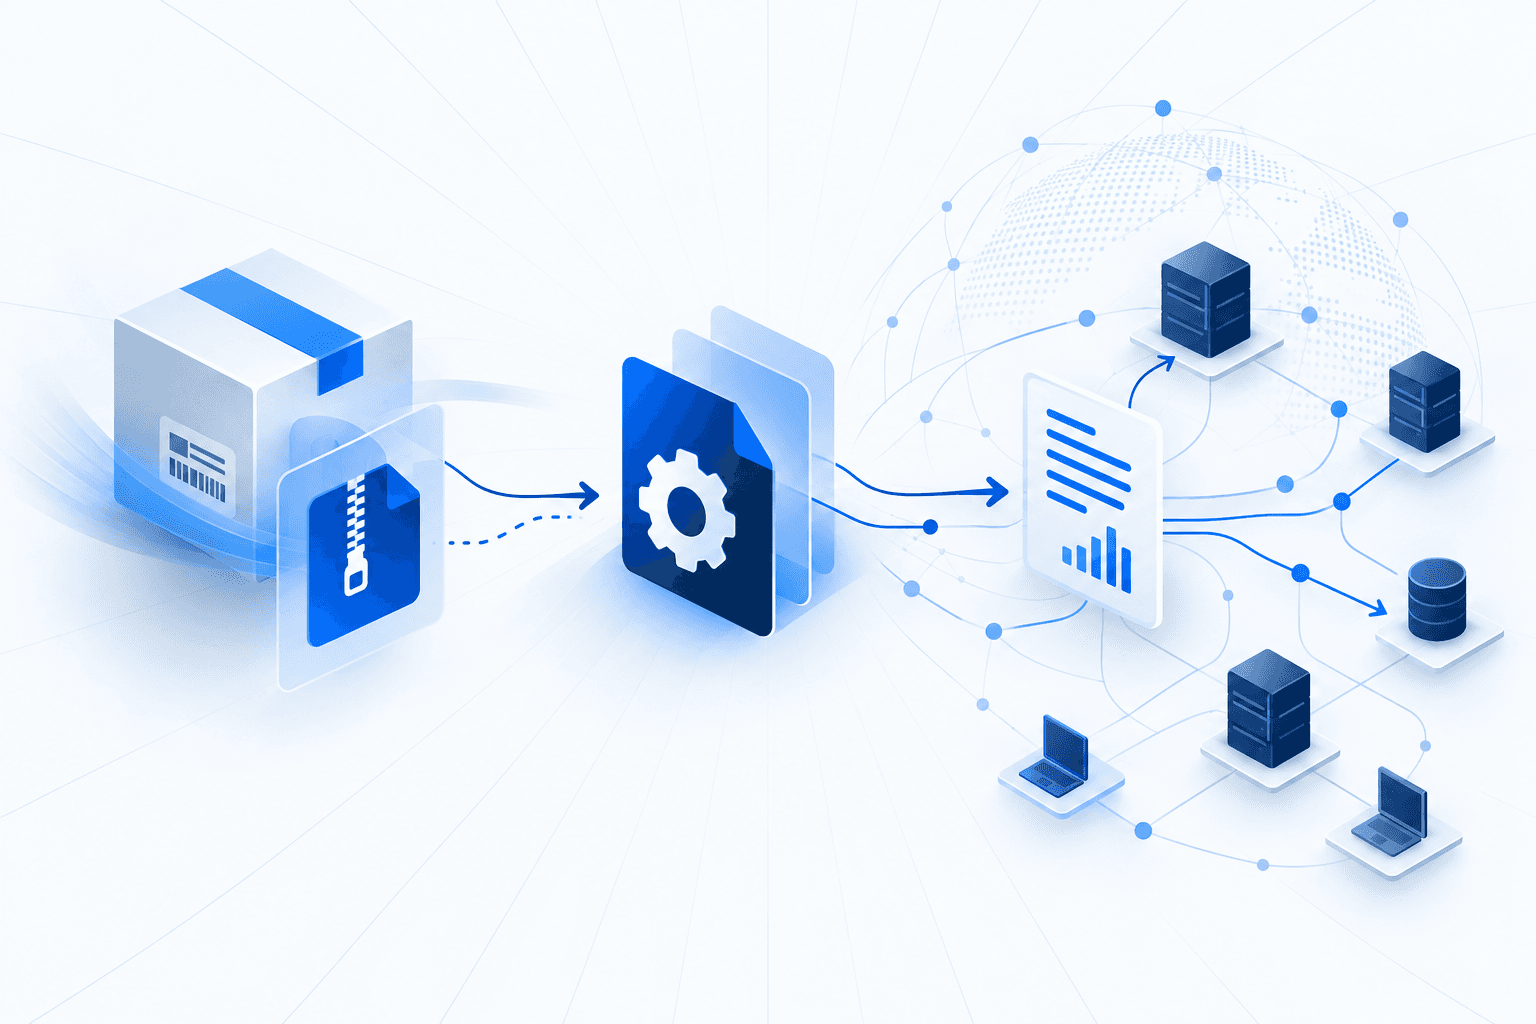
Attackers used a shipment-themed ZIP archive to launch a Windows infection chain combining a legitimate signed Kingsoft PDF application, DLL side-loading, and an obfuscated Python loader. A malicious DLL opened a decoy PDF while a disguised WinRAR utility extracted a password-protected package containing a Python runtime masquerading as Microsoft Edge Update. Successive XOR and Base64 decoding stages recovered a Windows executable that communicated with infrastructure associated with PureLogs and PureRAT campaigns; the findings do not establish that both malware families executed.
Unit 42 observed the infection chain on October 21 and documented it in research dated November 16, 2026, without identifying the threat actor or establishing how the download link reached the user. Defenders should prioritize behavioral detections for signed applications loading adjacent DLLs from Downloads, disguised archive extraction, and Python executing encoded document contents from a public directory. The legitimate application's signature or hash alone should not be treated as evidence of compromise; investigations should examine neighboring libraries and subsequent execution.