Malicious GitHub Repositories Hijack AI Coding Agents to Steal Developer Credentials
Emerging Technology Risk · 5 sources · Updated 2d ago · First seen Nov 17, 2026
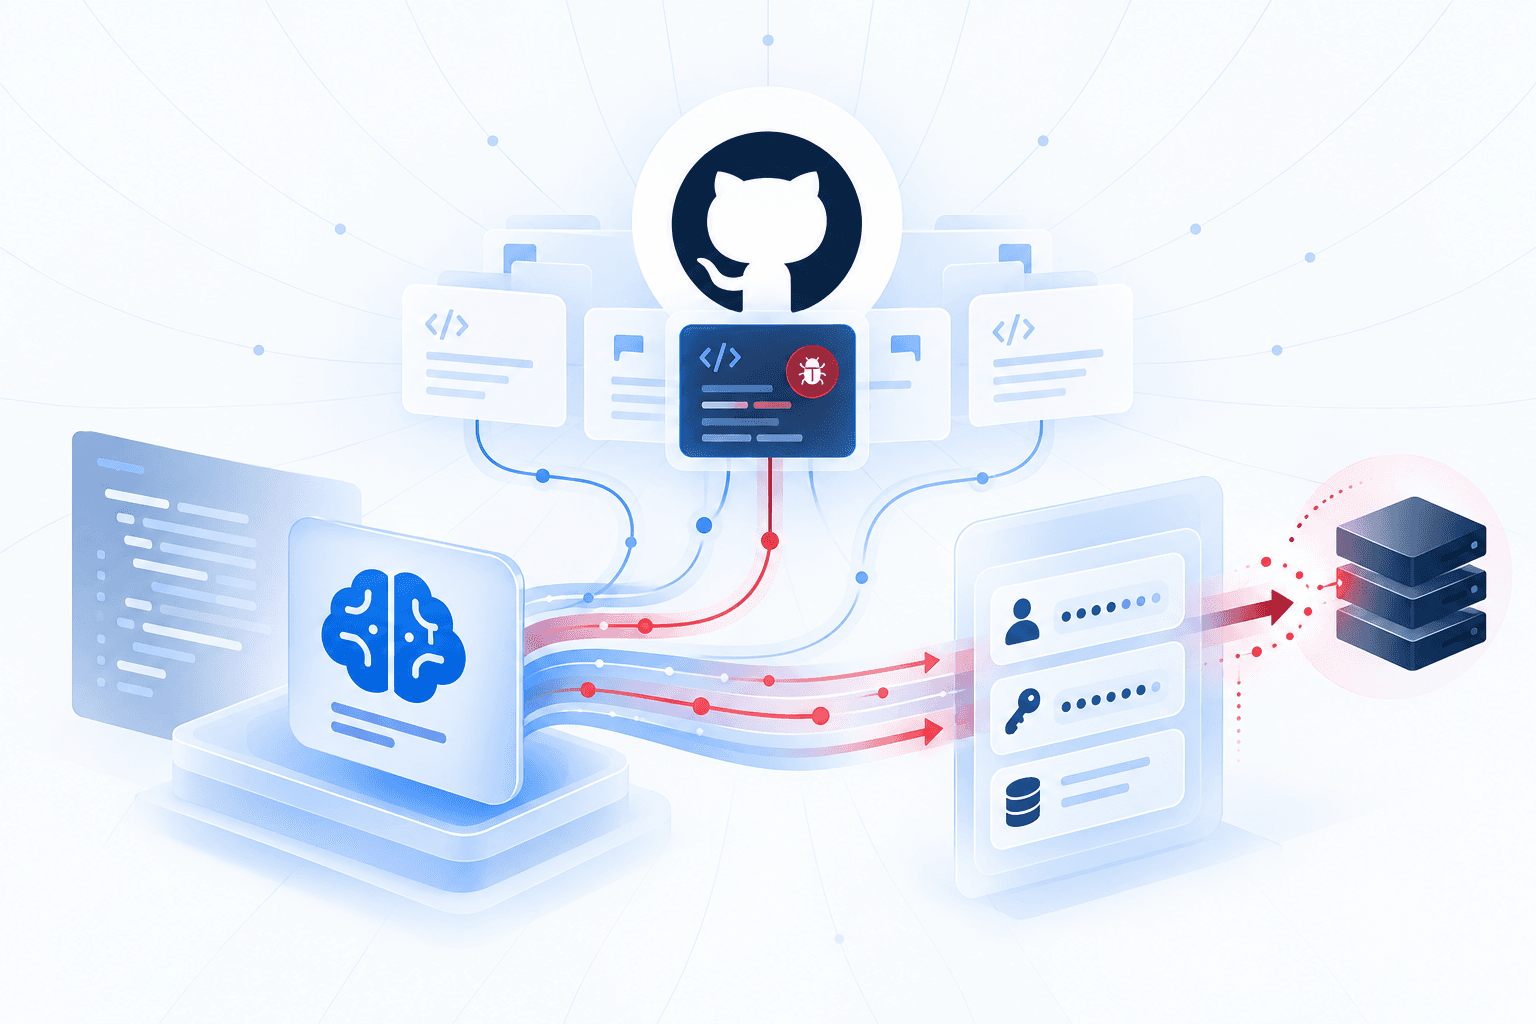
Bitdefender Labs identified 22 malicious GitHub links in a campaign targeting developers who use AI coding assistants. Attackers embed malicious project instructions, session-start hooks, Model Context Protocol (MCP) configurations, and editor tasks in repositories to launch a concealed JavaScript payload through a loader named setup.js. The campaign combines indirect prompt injection with execution hooks that do not require an AI assistant to follow malicious instructions. The payload runs with the developer’s permissions and can steal credentials and tokens, validate account access, and prepare collected data for exfiltration.
The malware also attempts to propagate by modifying local AI-agent configurations and using stolen GitHub and GitLab credentials to implant malicious files in additional repositories. Accessible package-publishing credentials can enable it to republish infected packages, extending the risk beyond the initially compromised workstation. Developers should inspect repository instructions, hooks, MCP settings, editor tasks, and referenced setup scripts before trusting unfamiliar projects. If malicious files have executed, responders should rotate all secrets accessible to the affected environment and investigate agent configurations, repositories, and package-publishing activity for further compromise.