Microsoft agent-framework PyPI Releases Hijacked to Steal Cloud and CI Credentials
Malware Intelligence · 33 sources · Updated 30m ago · First seen Nov 17, 2026
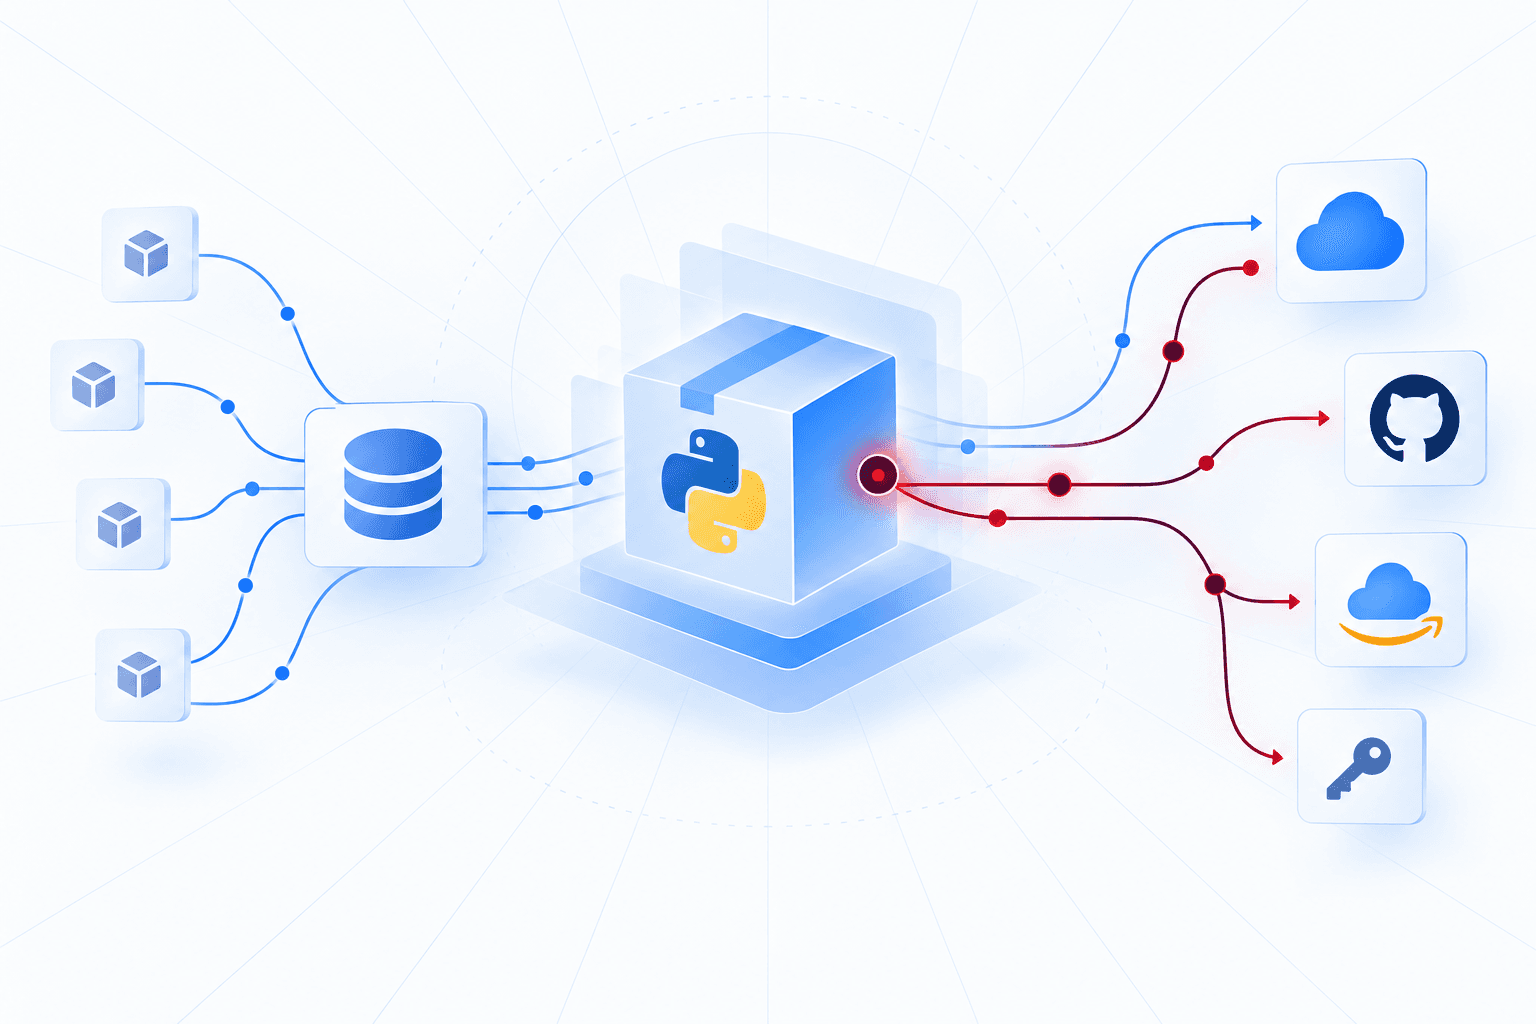
Two malicious releases of Microsoft’s official agent-framework Python package, versions 1.26.1 and 1.26.2, were published to PyPI and subsequently removed or quarantined. OX Security, Aikido and Wiz reported that both releases installed credential stealers through .pth startup hooks, causing the payload to execute whenever Python started in an affected environment without requiring an application to import the package. The malware collected environment secrets, credential files, other processes’ environment variables, Azure DevOps pipeline tokens and Azure managed identity tokens; version 1.26.2 additionally targeted GitHub Actions OIDC tokens and runner files. Stolen data was sent to a shared attacker-controlled webhook.site endpoint, while legitimate framework functionality was preserved to reduce visible disruption.
The attacker and initial compromise mechanism remain unidentified. Release anomalies suggested publishing outside the normal build process, and researchers observed the second malicious release after the first had been reverted. Reports placed removal of both versions at approximately 21:20–21:30 UTC on November 17. Organizations that installed either release should rebuild affected environments using a verified release, with researchers recommending 1.26.0 and package hash verification. Responders should rotate all secrets accessible to those environments and audit Azure, Azure DevOps and GitHub identity activity, federated access and outbound connections; removing the package alone does not invalidate stolen credentials.