UAT-12643 Uses Solana-Based C2 to Support RAT and Cryptocurrency Theft Campaign
Attack Tradecraft · 8 sources · Updated 2d ago · First seen Nov 18, 2026
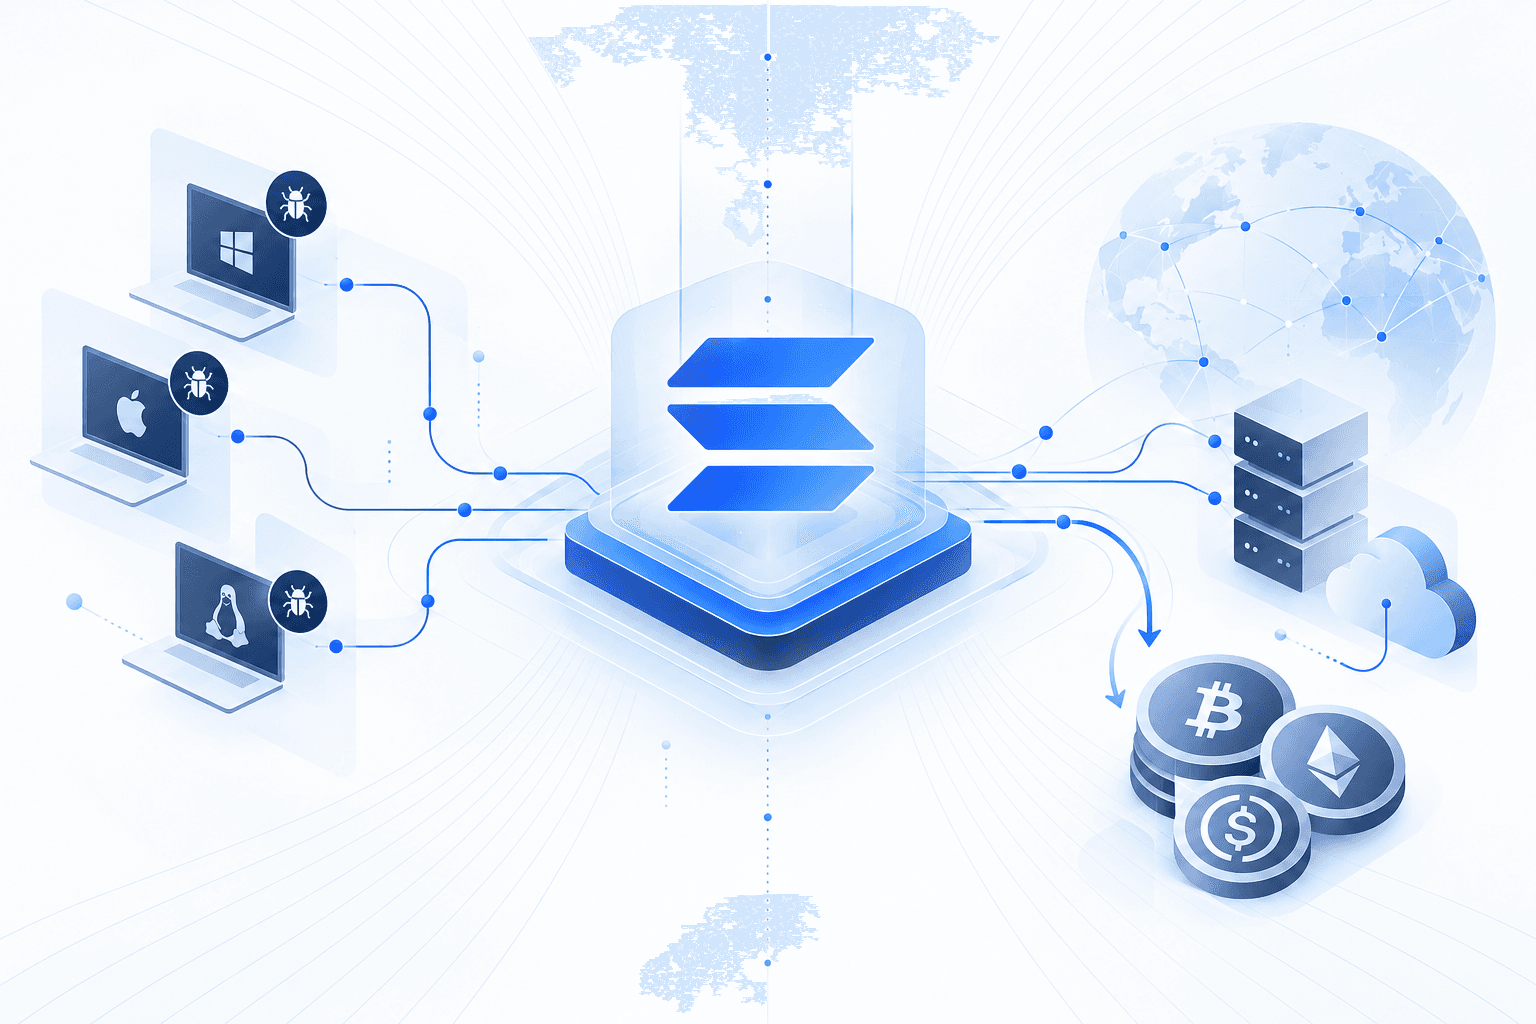
Cisco Talos identified malicious infrastructure linked to UAT-12643, a financially motivated threat actor deploying Overlord RAT, the Good Game infostealer, and a cryptocurrency clipboard hijacker. Lure themes and collection capabilities suggest targeting of cryptocurrency holders, gamers, finance and accounting personnel, messaging users, and VoIP operators, potentially including victims in Europe. Talos assessed a possible North Korea alignment with low confidence, cautioning that other actors also use the overlapping tools and techniques.
The campaign uses weaponized Windows shortcuts, HTA files, and MSBuild XML projects. Overlord retrieves encrypted command-and-control addresses from Solana transaction data and reportedly supports persistence through Windows recovery resets. Good Game steals credentials, sessions, sensitive files, and surveillance data, uploads archives to GoFile, and alerts operators through Discord webhooks; the clipboard hijacker replaces cryptocurrency addresses with attacker-controlled alternatives. Defenders should prioritize detecting suspicious shortcut-to-script execution and MSBuild activity, investigate unexpected GoFile uploads and Discord webhook traffic, and account for the reported reset-surviving persistence when planning remediation.