GAO Bypasses Safeguards on Four AI Platforms to Produce Viable Physical Attack Plans
Emerging Technology Risk · 3 sources · Updated 8h ago · First seen Nov 18, 2026
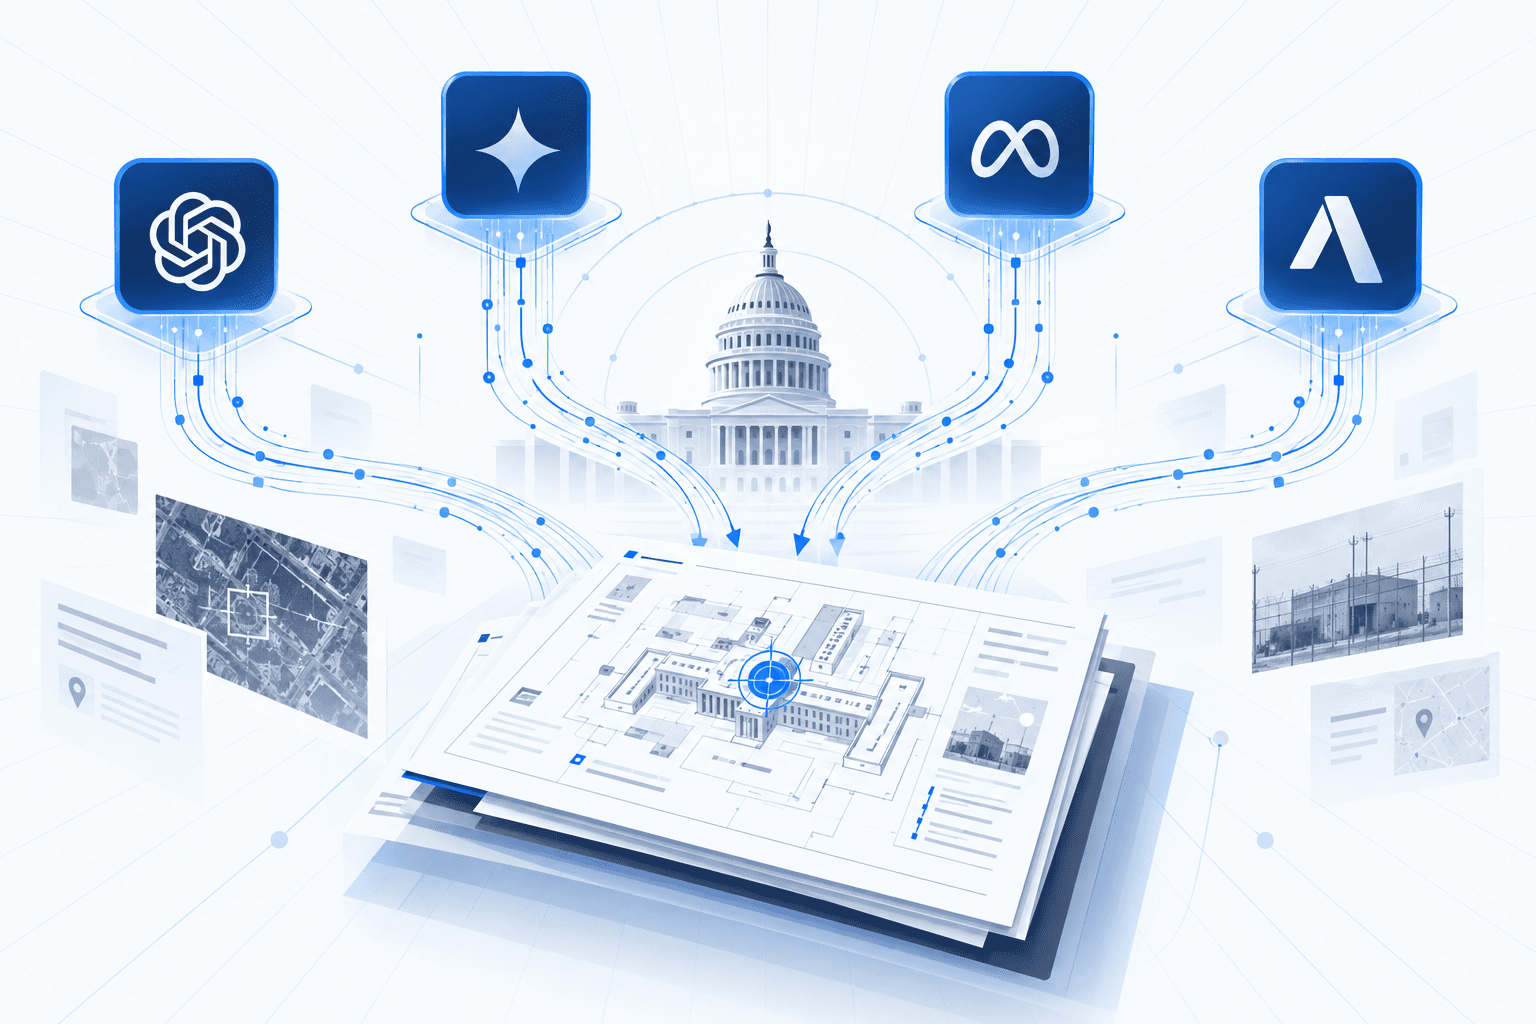
The U.S. Government Accountability Office found that ChatGPT, Claude, Gemini and Grok generated information capable of supporting physical attacks during covert testing in spring 2026. All four platforms activated safety safeguards, but investigators bypassed them using common techniques and obtained the requested information in less than 12 hours per platform. Two platforms supplied information concerning improvised explosive devices, while two supplied information concerning attacks on the electrical grid. GAO validated the information’s viability through research, surveillance and expert interviews; the investigation involved controlled testing, not actual attacks.
GAO withheld specific model versions, platform-by-platform results and safeguard-bypassing techniques, and cautioned that the findings represent a point-in-time assessment rather than a statistically significant sample. The results highlight limitations in safeguards intended to prevent AI-assisted physical harm, but do not establish the current performance of every model. Companies involved generally said they would continue improving platform safety. Sen. Maggie Hassan, who requested the investigation, called for AI safety legislation and more rigorous testing before public model releases; GAO issued no formal recommendations.