Mallory
← Back to News
enforcement-actionransomware-group-operationvoice-social-engineeringenergy-sector-threat

Ukraine and FBI Arrest Four Suspects in $40.5 Million Ransomware Investigation

Regulatory & Policy · 8 sources · Updated 27m ago · First seen Nov 19, 2026
Ukraine and FBI Arrest Four Suspects in $40.5 Million Ransomware Investigation

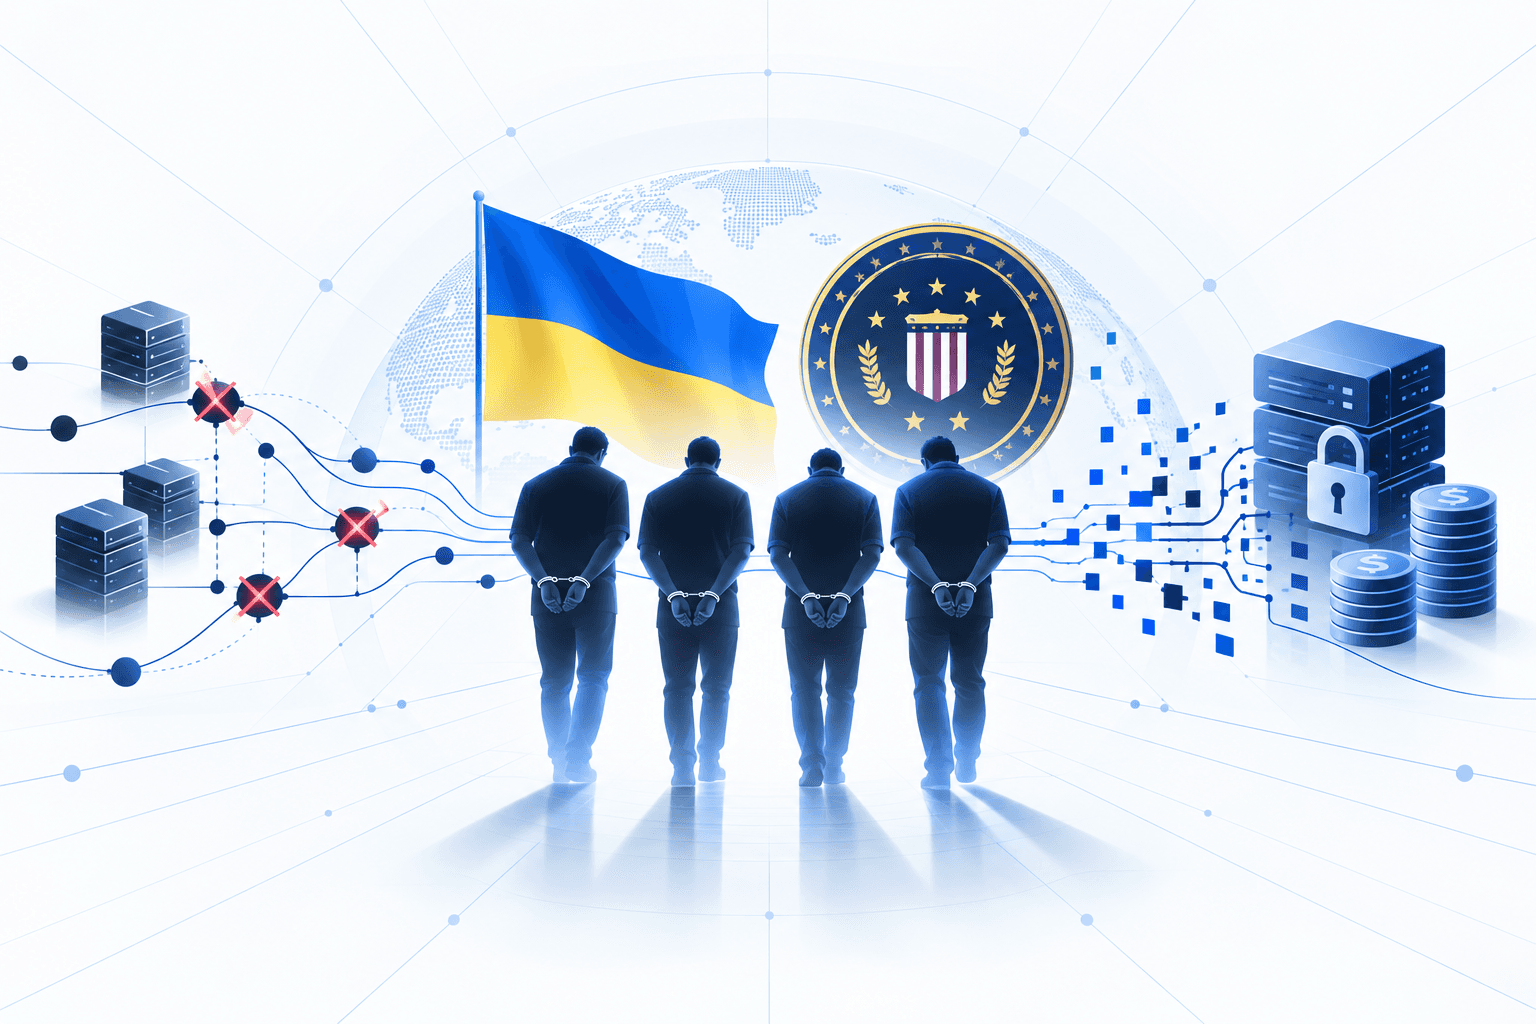
Ukrainian authorities, working with the FBI, arrested four alleged key members of an international ransomware organization linked to more than $40.5 million in ransom payments from at least 28 companies worldwide. The investigation lasted more than two years and identified a group of at least 27 people connected to a broader network exceeding 60 members, including former Conti participants. Police conducted 66 searches across Kyiv and 11 Ukrainian regions, seizing electronic devices, bank cards and cash. The suspects face up to 15 years in prison if convicted; their individual affiliations with Conti, BlackSuit or Chaos remain unconfirmed.

Investigators said the attackers impersonated IT support through phone calls and AI-generated voice messages, using corporate VPN phishing pages and remote-access software to gain access. They then stole data, encrypted systems and threatened disclosure to demand cryptocurrency payments. In one documented incident, an attacker kept an employee on the phone while an accomplice accessed the corporate network. Targets spanned energy, pharmaceuticals, industry, logistics, finance and infrastructure. Ukrainian court records identify victims including Warren Oil Company, Maxxis International-USA, Newpark Resources and Quantum Health, and name Chaos ransomware as a tool used by the organization. The reported intrusion methods underscore the need to independently verify support requests and restrict remote-access software installation.

What this changes for youSee the reporting duties and controls this puts on the clock.
Get the context
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

12 events · Aug 2024 – Nov 18, 2026
  1. Reported Nov 19, 20265h ago

    Four detained suspects formally notified of criminal suspicion

    The four suspects were formally notified of suspicion concerning participation in a criminal organization and unauthorized interference with information systems and remained in custody. They face up to 15 years in prison if convicted; authorities have not confirmed their individual affiliations with Conti, BlackSuit or Chaos.

    Ukraine arrests key members of ransomware gang that extorted $40.5 million posing as IT support - Help Net Security
  2. Reported Nov 19, 20268h ago

    Investigation reveals AI-assisted support impersonation and Chaos ransomware use

    Authorities described a custom platform using AI-generated voice messages to impersonate IT support and obtain credentials or persuade employees to install remote-access software. Court records identify corporate VPN phishing pages, spoofed telephone numbers, TeamViewer, AnyDesk and Chaos ransomware among the organization's tools and techniques.

    vxunderground: @darkzOGx Tbh idek, I saw the photos and died inside https://t.co/nckN1TJQMZ
  3. Reported Nov 18, 202616h ago

    Ukrainian police release footage of alleged $15 million extortion call

    Ukraine's National Police released investigation footage containing an alleged extortion call demanding $15 million. During the call, the speaker claimed that more than 1.5 terabytes of corporate data had been stolen.

    Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms
  4. Reported Nov 18, 202616h ago

    Attackers expand Warren Oil intrusion to related companies

    After the negotiated $5 million ransom payment, the attackers expanded their attack to other companies in the same corporate group.

    Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms
  5. Nov 18, 20262d ago

    Ukraine and FBI operation arrests four suspected ransomware members

    Ukrainian authorities working with the FBI arrested four alleged key members of an organization linked to more than $40.5 million in ransom payments from at least 28 companies, following a two-year investigation. The operation included 66 searches across Kyiv and 11 regions, with investigators seizing electronics, bank cards, nearly $370,000 and €20,000.

    Dinosn: Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms https://t.co/U6gtVnDi3O
  6. Reported Oct 26, 202625d ago

    Ukrainian police identify wider international network linked to ransomware organization

    Ukrainian police said investigators identified at least 27 members of the organization across countries including Ukraine, Kazakhstan and Russia. A broader criminal structure linked to it reportedly includes more than 60 participants across eight jurisdictions.

    Дзвінок від "ІТ-підтримки" - і компанія в заручниках: керівник Нацполіції розповів про викриття хакерів, які отримали понад $40 млн | Національна поліція України
  7. Jun 2026

    Quantum Health allegedly pays $5 million after $15 million demand

    Ukrainian court records allege that Quantum Health paid a $5 million ransom after the attackers initially demanded $15 million.

    Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms
  8. May 29, 20266mo ago

    Quantum Health intrusion begins after employee responds to vishing call

    Quantum Health disclosed that an employee responded to a vishing call on May 29, 2026, and an unauthorized party accessed and took files between May 29 and June 1. The files contained health insurance and medical information and potentially some Social Security numbers; Washington’s attorney general listed 15,321 state residents as affected.

    Ukraine, FBI Arrest 4 Ransomware Suspects Tied to $40.5M
  9. Dec 2024

    Newpark Resources allegedly pays $1.5 million ransom

    Ukrainian court records allege that Newpark Resources paid a $1.5 million ransom to the criminal organization.

    Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms
  10. Nov 2024

    BlackSuit claims Maxxis International as a victim

    BlackSuit claimed Maxxis International as a victim, according to reporting cited by BleepingComputer. Ukrainian court records also identify Maxxis International-USA among the victims of the organization under investigation.

    Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms
  11. Oct 2024

    Attackers allegedly breach Newpark Resources using stolen employee credentials

    Ukrainian court records allege that attackers targeted Newpark Resources in October 2024, tricking employees into revealing credentials that enabled access to the company's network.

    Ukraine exposes ransomware network extorting US oil, healthcare firms | The Record from Recorded Future News
  12. Aug 2024

    Warren Oil Company breached in attack involving 1.4 terabytes of stolen data

    Ukrainian court records identify Warren Oil Company as the victim of an August 2024 attack in which hackers copied 1.4 terabytes of data. The attackers subsequently received 84.5 BTC, worth approximately $5 million, after initially demanding $10 million.

    Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Organizations

6 linked
Federal Bureau of InvestigationNational Police of UkraineQuantum HealthNewpark ResourcesMaxxis International-USAWarren Oil Company

Breaches

2 linked
MAXXISINTERNATIONAL-USA-2024-11WARRENOILCOMPANY-2024-08
Do you run this?See what this changes for your reporting obligations and which controls it puts on the clock.
Get the Regulatory Context
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.