Mallory
← Back to News
open-source-dependency-vulnerabilityinternet-facing-service-vulnerabilityend-of-life-softwarewidely-deployed-product-advisory

Ruby2Shell Heap Overflow Exposes Rails and Sinatra Apps to Unauthenticated RCE

Vulnerability Disclosure · 9 sources · Updated 24m ago · First seen Nov 19, 2026
Ruby2Shell Heap Overflow Exposes Rails and Sinatra Apps to Unauthenticated RCE

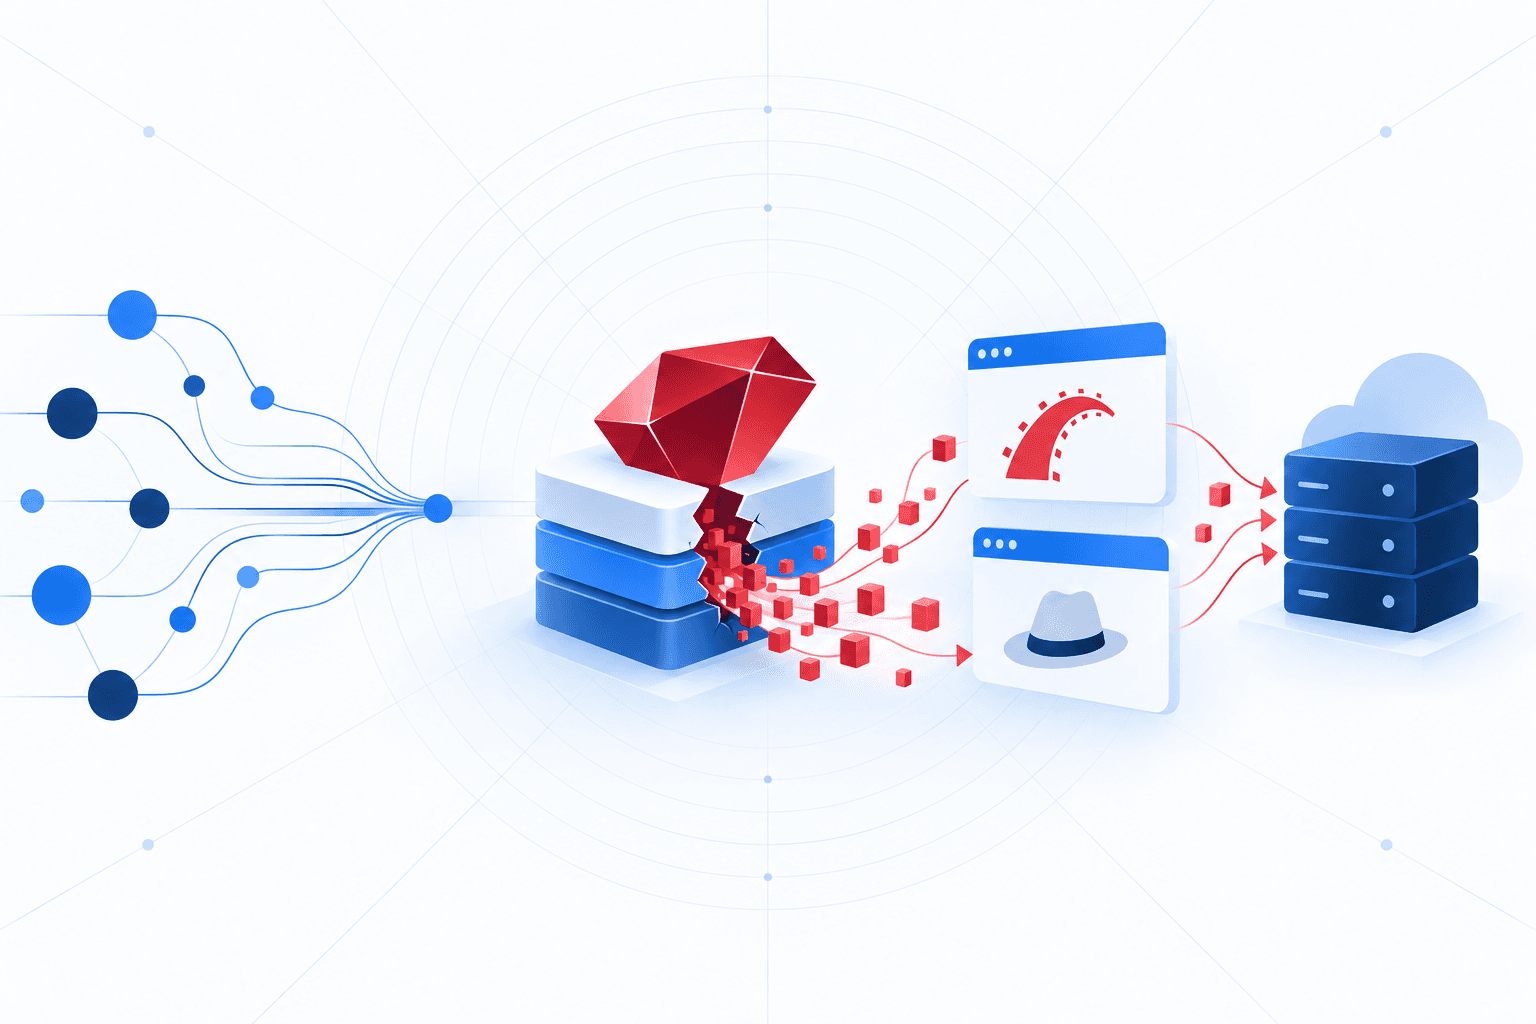
Ruby has patched Ruby2Shell (GHSA-34m4-m9fh-gqp5), a critical one-byte heap buffer overflow in string case conversion that can enable unauthenticated remote code execution. The flaw affects processing of certain legacy encodings; UTF-8 strings follow an unaffected code path. Veria Labs reports that default Ruby on Rails and classic-style Sinatra applications can expose the vulnerable functionality without authentication. Ruby maintainers are aware of proof-of-concept exploits achieving code execution in some scenarios, but sources report no known exploitation in the wild as of November 19, 2026. Researchers plan to publish their exploit in approximately one week.

Fixed Ruby versions are 3.3.14, 3.4.13 and 4.0.10, released November 18; affected Ruby 3.2 and earlier branches are unsupported and will not receive fixes. Identified releases of GitLab, GitHub Enterprise Server, Mastodon, OpenProject, Discourse and Chatwoot bundled vulnerable runtimes, although Discourse updated its Docker base image on November 19. Administrators should inventory and upgrade the Ruby runtime actually loaded by each application—including separately bundled copies—then rebuild affected containers and restart application servers. Where vendor fixes remain unavailable, restrict access to affected self-hosted services to reduce exposure.
Do you run this?See affected versions and whether adversaries are exploiting it.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

7 events · Nov 18, 2026 – Nov 19, 2026
  1. Reported Nov 19, 20267h ago

    Researcher reports independently finding Ruby bugs enabling Rails RCE

    Researcher @stdoutput said they had independently discovered Ruby bugs approximately a month earlier and claimed the bugs enabled universal pre-authentication remote code execution against Ruby on Rails.

    Dinosn: RT @stdoutput: About a month ago, I looked into Ruby and independently found bugs that make a universal pre-auth RCE on ...
  2. Reported Nov 19, 202616h ago

    Mastodon and OpenProject provide releases bundling patched Ruby

    Mastodon 4.7.6 and OpenProject 17.9.8 bundle Ruby 4.0.10 and are listed as fixed for ruby2shell, superseding the previously identified vulnerable versions.

    Ruby2Shell (GHSA-34m4-m9fh-gqp5) | Veria Labs
  3. Nov 19, 202616h ago

    Discourse updates its Docker base image to patched Ruby

    Discourse adopted Ruby 4.0.10 as the default base image in discourse_docker, replacing vulnerable Ruby 4.0.9. Docker installations could obtain the fix by rebuilding with the updated discourse_docker.

    ruby2shell: heap overflow in Ruby string case conversion can lead to remote code execution | Zero Wire | Cloudflare Radar
  4. Nov 19, 202616h ago

    Veria Labs identifies six products bundling vulnerable Ruby runtimes

    Veria Labs listed GitLab 19.6.0, GitHub Enterprise Server 3.22.5, Mastodon 4.7.5, OpenProject 17.9.7, Discourse 2026.10.1 and Chatwoot 4.20.0 as bundling affected Ruby versions. Updating a host's system Ruby would not fix separately bundled application runtimes.

    ruby2ßhell: Critical One-Byte Heap Overflow in Ruby Could Allow Remote Code Execution Attacks
  5. Nov 19, 202616h ago

    Ruby publishes critical ruby2shell security advisory

    Ruby published GHSA-34m4-m9fh-gqp5 for a one-byte heap overflow in string case conversion involving certain legacy encodings, crediting Stephan Lipp of Ada Logics and Anthropic with reporting it. Ruby acknowledged proofs of concept achieving code execution in some scenarios; Veria Labs reported unauthenticated reachability in default Rails and classic-style Sinatra applications.

    ruby2shell: heap overflow in Ruby string case conversion can lead to remote code execution | Zero Wire | Cloudflare Radar
  6. Nov 18, 20262d ago

    Ruby releases fixes for ruby2shell and six other vulnerabilities

    Ruby released versions 3.3.14, 3.4.13 and 4.0.10, fixing the ruby2shell heap overflow and six additional vulnerabilities. Affected Ruby 3.2 and older branches remained unsupported and unpatched.

    ruby2ßhell: Critical One-Byte Heap Overflow in Ruby Could Allow Remote Code Execution Attacks
  7. Reported Oct 28, 202623d ago

    Ruby commits sharp-s case-mapping bounds-check fix

    Ruby commit d582f8f fixed a one-byte heap overflow across 14 single-byte encoding implementations by requiring two available output bytes before processing characters that could include sharp s. The commit also added regression tests covering sharp-s expansion in multiple case-mapping operations.

    Fix a heap buffer overflow in case mapping of the sharp s · ruby/ruby@d582f8f · GitHub
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Vulnerabilities

1 linked

Affected products

6 linked
ChatwootOpenprojectGitlabDiscourseRubyGithub Enterprise Server

Organizations

6 linked
ChatwootOpenprojectGitLabGitHubDiscourseMastodon
Do you run this?See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
Check Your Exposure
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.