Mallory
← Back to News
government-diplomatic-threatoperational-disruptionai-enabled-threat-activity

European Commission Cyberattack Disrupts HR, Reimbursement and Translation Services

Sector Threat Intelligence · 11 sources · Updated 24m ago · First seen Nov 19, 2026
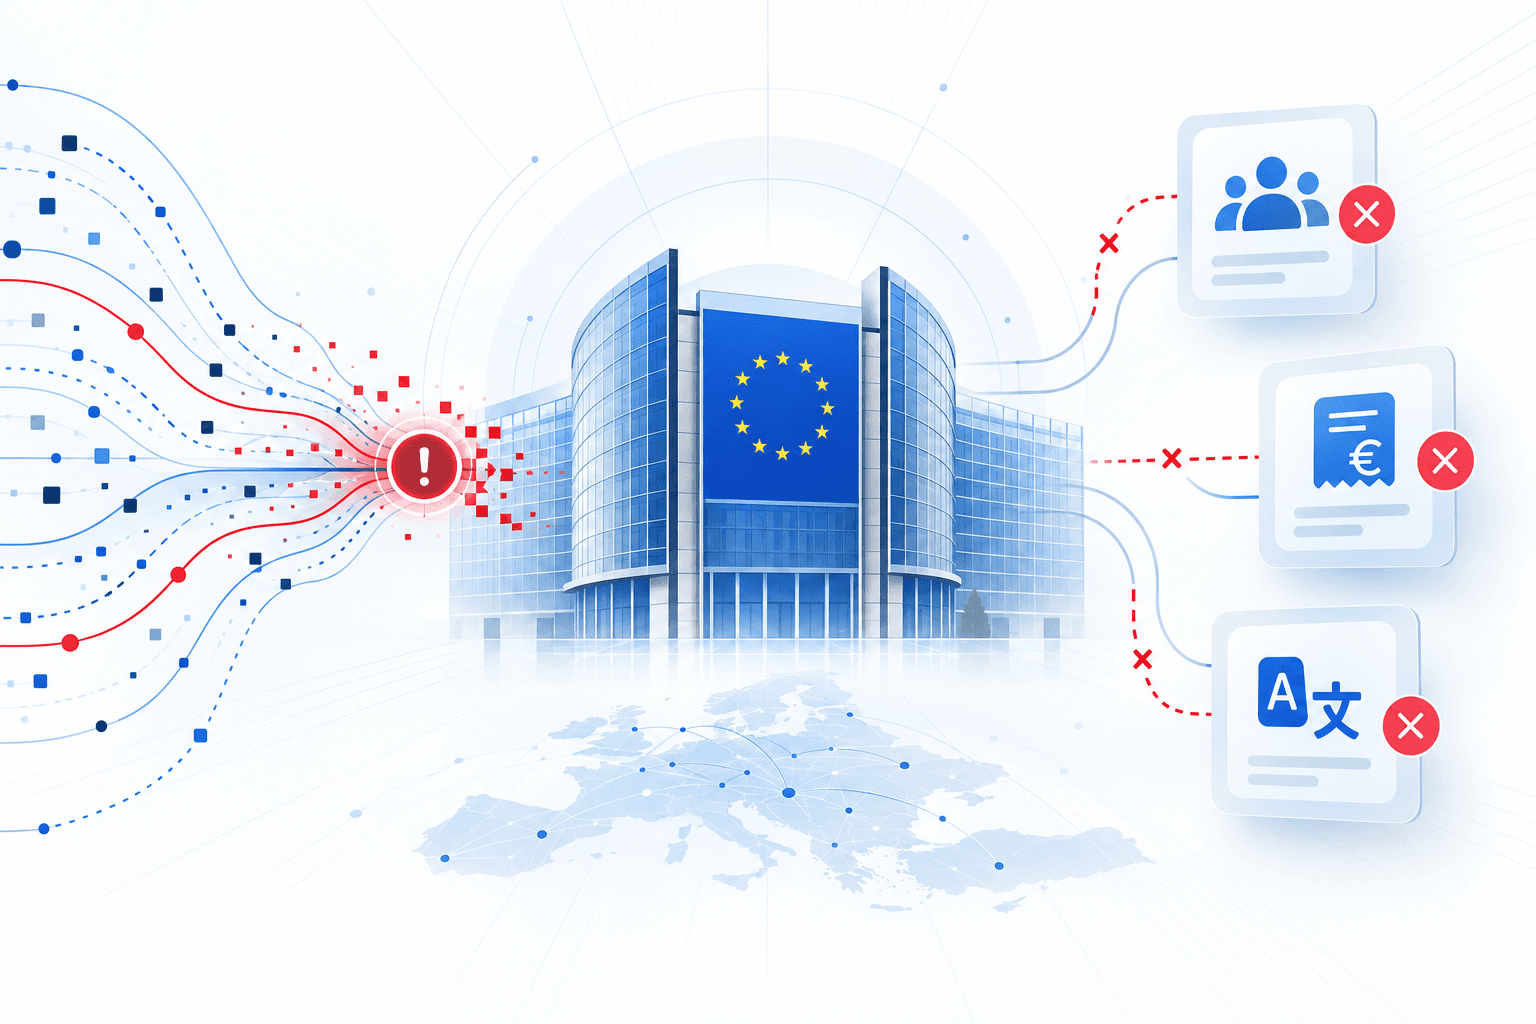
European Commission Cyberattack Disrupts HR, Reimbursement and Translation Services

A cyberattack disrupted European Commission internal services for more than 10 days, affecting personnel platform Sysper, reimbursement system MyPMO and translation applications, according to reporting attributed to POLITICO. Some employees were unable to complete routine personnel and reimbursement tasks. Commission spokesperson Thomas Regnier confirmed a campaign targeting multiple systems. Most affected applications had returned online, and an EU official said the Commission believed it had contained most of the attack, but the attackers, initial access method and full impact remained unknown. Investigators had not established whether personal or medical information was accessed or stolen.

Reports also highlighted CERT-EU findings or warnings concerning malicious use of ARTEX, a publicly available AI-driven penetration-testing tool, against European institutions. Its role in the Commission incident remained unconfirmed: investigators had not established whether it enabled initial access or was used only to identify vulnerabilities. The incident underscores the need to validate recovery across interconnected staff services and investigate potential exposure of sensitive records rather than equating restored availability with complete containment. No public evidence connected this attack to the separate March 2026 Commission breach involving a Trivy supply-chain compromise.
Who's targeting your sector?See the actors and campaigns active against you right now.
See sector threats
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

13 events · Mar 24, 2026 – Nov 18, 2026
  1. Reported Nov 19, 20266h ago

    Commission confirms campaign targeting multiple systems

    Spokesperson Thomas Regnier confirmed that multiple systems had been targeted and said affected individuals had been informed. An EU official said the Commission believed it had contained most of the attack, but investigators had not established whether personal or medical information had been accessed or stolen.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  2. Reported Nov 19, 20266h ago

    Commission takes applications offline and strengthens security checks

    The Commission temporarily disabled several applications as a precautionary security measure. Its digital services department also ordered additional security checks.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  3. Nov 18, 20262d ago

    Henna Virkkunen briefs European commissioners

    Executive Vice-President Henna Virkkunen briefed fellow commissioners on the cyber incident and response measures.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  4. Nov 18, 20262d ago

    Sysper suffers another interruption after restoration

    The Sysper personnel platform briefly went down again after having returned to service earlier in the week.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  5. Nov 17, 20263d ago

    Commission translation services disrupted

    European Commission translation services experienced disruption during the cyber incident.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  6. Nov 13, 20267d ago

    FBI issues alert concerning ARTEX

    The FBI published an alert concerning ARTEX, an AI-enabled penetration-testing tool that had been abused by cybercriminals.

    Une immense cyberattaque frappe la Commission européenne : l’arme des hackers est un outil IA qui a échappé à son propre créateur - Numerama
  7. Nov 5, 202615d ago

    CERT-EU warns of likely malicious use of ARTEX

    CERT-EU issued an alert about malicious activity against entities in its constituency that very likely relied on the AI-driven penetration-testing platform ARTEX. Its direct role in compromising the affected Commission applications remained unconfirmed.

    Cyberattaque à la Commission européenne : dix jours de perturbations et des données sensibles potentiellement exposées
  8. Nov 2026

    Sysper and MyPMO restored early in the reporting week

    The Commission restored its Sysper personnel platform and MyPMO medical reimbursement application early in the week of the November 19 reporting.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  9. Nov 2026

    Commission management holds emergency meeting on cyber incidents

    The Commission's Corporate Management Board held an emergency meeting in early November to examine ongoing cyber incidents.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  10. Nov 2026

    Cyberattack disrupts European Commission internal applications

    A cyberattack disrupted Commission staff services for more than ten days, affecting personnel administration, medical reimbursements and translation services. Some employees could not submit timesheets, request leave or enter salary information.

    Hackers Target European Commission with ARTEX AI Tool in Major Cyberattack
  11. Oct 22, 202629d ago

    Commission detects intrusion ahead of November service disruptions

    The European Commission detected the intrusion on October 22, 2026. It confirmed the incident as a cyberattack on October 26, triggering mitigation measures and an investigation.

    European Commission Confirms AI-Driven Cyber-Attack Took Systems Offli - Infosecurity Magazine
  12. Mar 28, 20268mo ago

    ShinyHunters publishes data stolen in the March breach

    ShinyHunters published the stolen March data on its leak site, amounting to approximately 340 GB when decompressed. No public evidence connected this breach to the subsequent November campaign.

    Cyberattaque à la Commission européenne : dix jours de perturbations et des données sensibles potentiellement exposées
  13. Mar 24, 20268mo ago

    Separate breach discovered in Commission cloud-hosting infrastructure

    A breach discovered in the European Commission's AWS infrastructure hosting Europa.eu websites involved a compromised Trivy security tool attributed to TeamPCP. Investigators determined that attackers exfiltrated 91.7 GB of compressed data; the Commission said its internal IT systems were unaffected.

    Cyberattaque à la Commission européenne : dix jours de perturbations et des données sensibles potentiellement exposées
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Organizations

1 linked
European Commission

Breaches

1 linked
EUROPEANCOMMISSION-2026-11
Do you run this?See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
See Your Sector's Threats
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.