Mallory
← Back to News
operational-disruptioninformation-technology-sector-threatbreach-disclosure-notification

N-able Server Breach Disrupts Mail Assure and SpamExperts Management Across Three Regions

Breach & Incident Intelligence · 7 sources · Updated 31m ago · First seen Nov 19, 2026
N-able Server Breach Disrupts Mail Assure and SpamExperts Management Across Three Regions

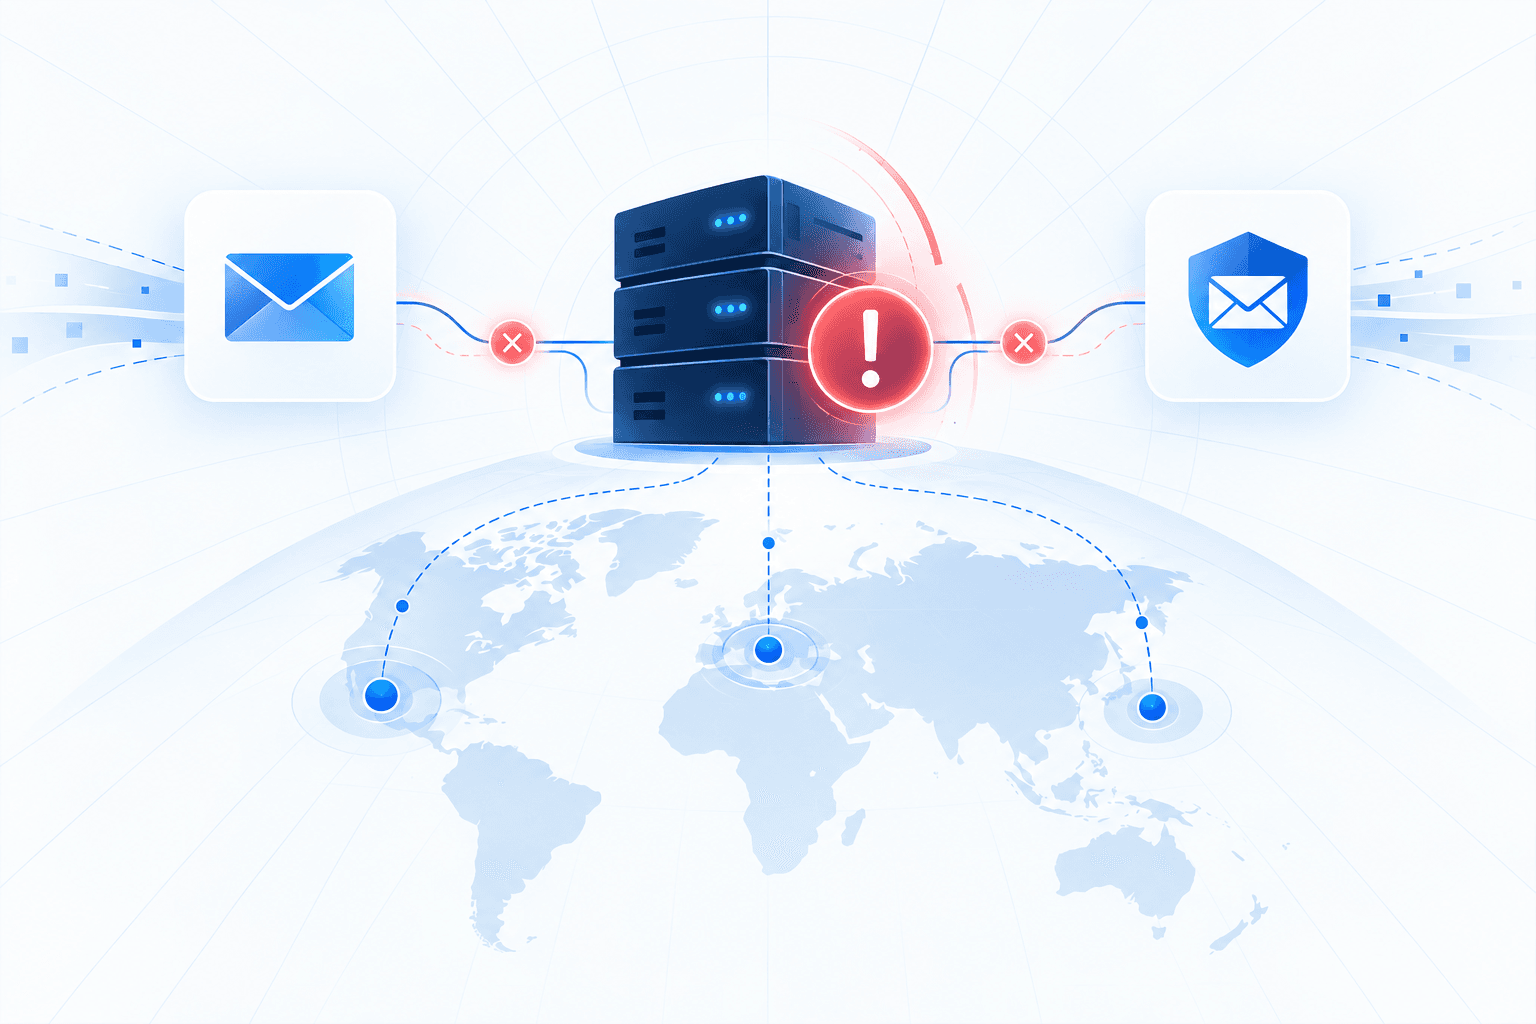
N-able confirmed that unidentified attackers gained unauthorized access to one server supporting its Mail Assure and SpamExperts Hosted Cloud services, disrupting email-security management across the Americas, Europe, and Asia-Pacific. The disruption began on November 16, 2026, and was initially attributed to platform configuration and service dependencies before being identified as a security incident. Management dashboards, APIs, quarantine access, and logging became unavailable, while core mail flow and inbound and outbound filtering remained operational.

N-able said it had found no evidence of customer data compromise or access to customer mailboxes, but its investigation remained ongoing; the attacker, entry method, and access duration were not disclosed. As of 08:00 UTC on November 19, restoration, fix validation, and security hardening were still underway, with no restoration time provided. The company had directly contacted affected service partners and said the breach was unrelated to the separate N-central security incident earlier in November.
Is this vendor in your chain?See attribution, scope, and your downstream exposure.
Check the blast radius
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events · Nov 16, 2026 – Nov 19, 2026
  1. Reported Nov 19, 20265h ago

    N-able contacts affected service partners with tailored guidance

    N-able directly contacted Mail Assure and SpamExperts Hosted Cloud partners with environment-specific information and guidance on whether they needed to take action.

    Хакери пробија N-able Cloud Server, нарушувајќи го управувањето со безбедноста на е-поштата во 3 региони | MKD-CIRT
  2. Nov 19, 202616h ago

    N-able begins controlled testing of fixes and adds security changes

    At 00:01 UTC on November 19, N-able reported that it had begun testing fixes in a controlled environment; by 04:01 UTC, engineers were continuing tests and implementing additional security changes. Its 08:00 UTC update reported ongoing validation and hardening, with management access still disabled and no restoration time provided.

    N-able Confirms Server Breach, Disables Mail Assure and SpamExperts Management Access | Cryptika Cybersecurity
  3. Nov 18, 20262d ago

    N-able discloses server breach behind three-region management outage

    On Wednesday, N-able disclosed unauthorized access to one server supporting Mail Assure and SpamExperts Hosted Cloud and said it had disabled management interfaces and APIs across the Americas, APAC, and Europe while containing the incident. Core email filtering remained operational, and the ongoing investigation had found no evidence of customer data compromise or mailbox access.

    Хакери пробија N-able Cloud Server, нарушувајќи го управувањето со безбедноста на е-поштата во 3 региони | MKD-CIRT
  4. Nov 16, 20264d ago

    N-able begins investigating hosted email-security disruption

    On November 16, N-able began investigating and notified customers of a disruption affecting Mail Assure and SpamExperts Hosted Cloud. It initially attributed the problem to platform configuration and dependencies between services.

    Хакери пробија N-able Cloud Server, нарушувајќи го управувањето со безбедноста на е-поштата во 3 региони | MKD-CIRT
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

1 linked
Mail Assure

Organizations

1 linked
N-Able

Breaches

1 linked
N-ABLE-2026-11
Do you run this?See attribution, scope, and whether this vendor sits anywhere in your supply chain.
Get the Full Incident Picture
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.