BADBOX 3.0 Disrupted After Generating 40 Billion Fraudulent Ad Bid Requests Daily
Malware Intelligence · 3 sources · Updated 15m ago · First seen Nov 19, 2026
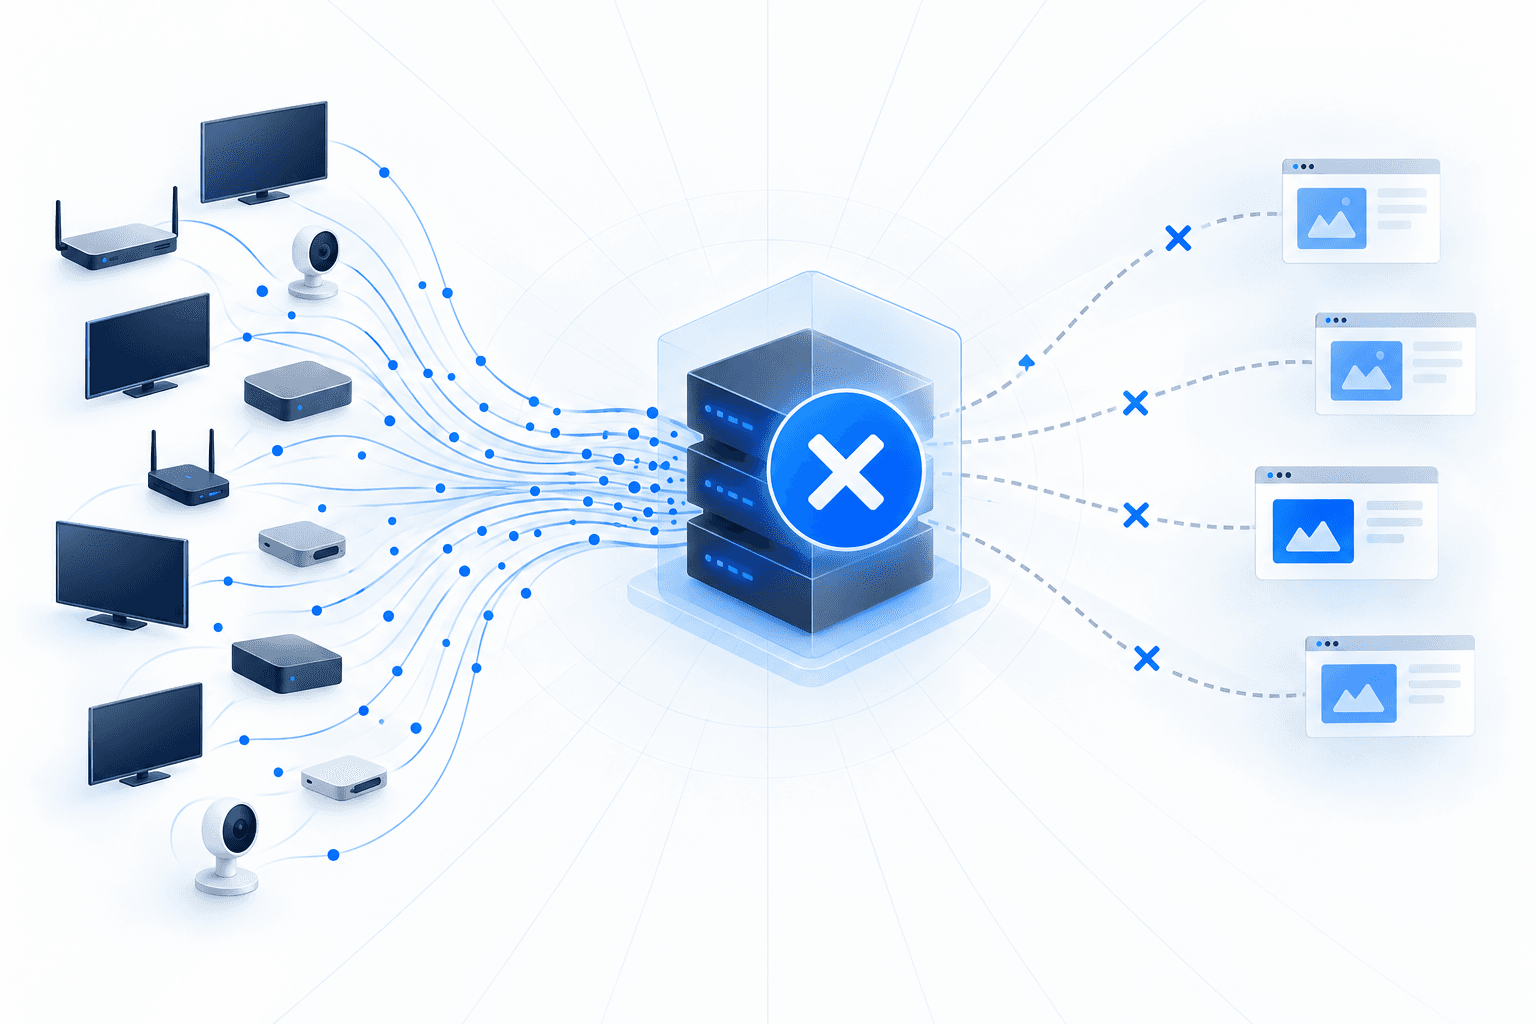
HUMAN Security’s Satori team identified and disrupted BADBOX 3.0, an operation that used compromised low-cost Android streaming boxes and fabricated traffic to generate roughly 40 billion advertising bid requests daily at its peak. The campaign ran hidden video ads, impersonated legitimate connected-TV apps, and enrolled devices in residential proxy networks without owners’ consent. Its traffic exceeded 4% of connected-TV traffic observed by the Human Defense Platform. Findings published November 18 linked the operation’s software catalog to Chinese electronics manufacturer TXCZ through infrastructure and device-specific evidence. Researchers also found Vo1d botnet code and assessed that the PXYEDGE proxy network succeeded IpMoYu. The findings did not establish a unique infected-device count; bid requests do not equate to ads watched or payments made.
The affected hardware primarily ran uncertified Android Open Source Project software, rather than Google’s Android TV OS. The operation follows earlier BADBOX campaigns, including BADBOX 2.0, which the FBI warned had compromised millions of home-connected devices through malware installed before purchase or malicious applications downloaded during setup. Those devices enabled criminals to route activity through victims’ residential internet connections. Organizations should evaluate streaming and other connected devices on their networks, monitor unexpected traffic, and disconnect suspicious hardware; the FBI also recommends avoiding unofficial app marketplaces and keeping operating systems, software, and firmware updated.