Mallory
← Back to News
credential-stealer-activityinitial-access-methodloader-delivery-mechanismdefense-evasion-method

Fake GTA VI Streaming Client Delivers Rust-Based Infostealer Through ClickFix

Malware Intelligence · 2 sources · Updated 12h ago · First seen Nov 20, 2026
Fake GTA VI Streaming Client Delivers Rust-Based Infostealer Through ClickFix

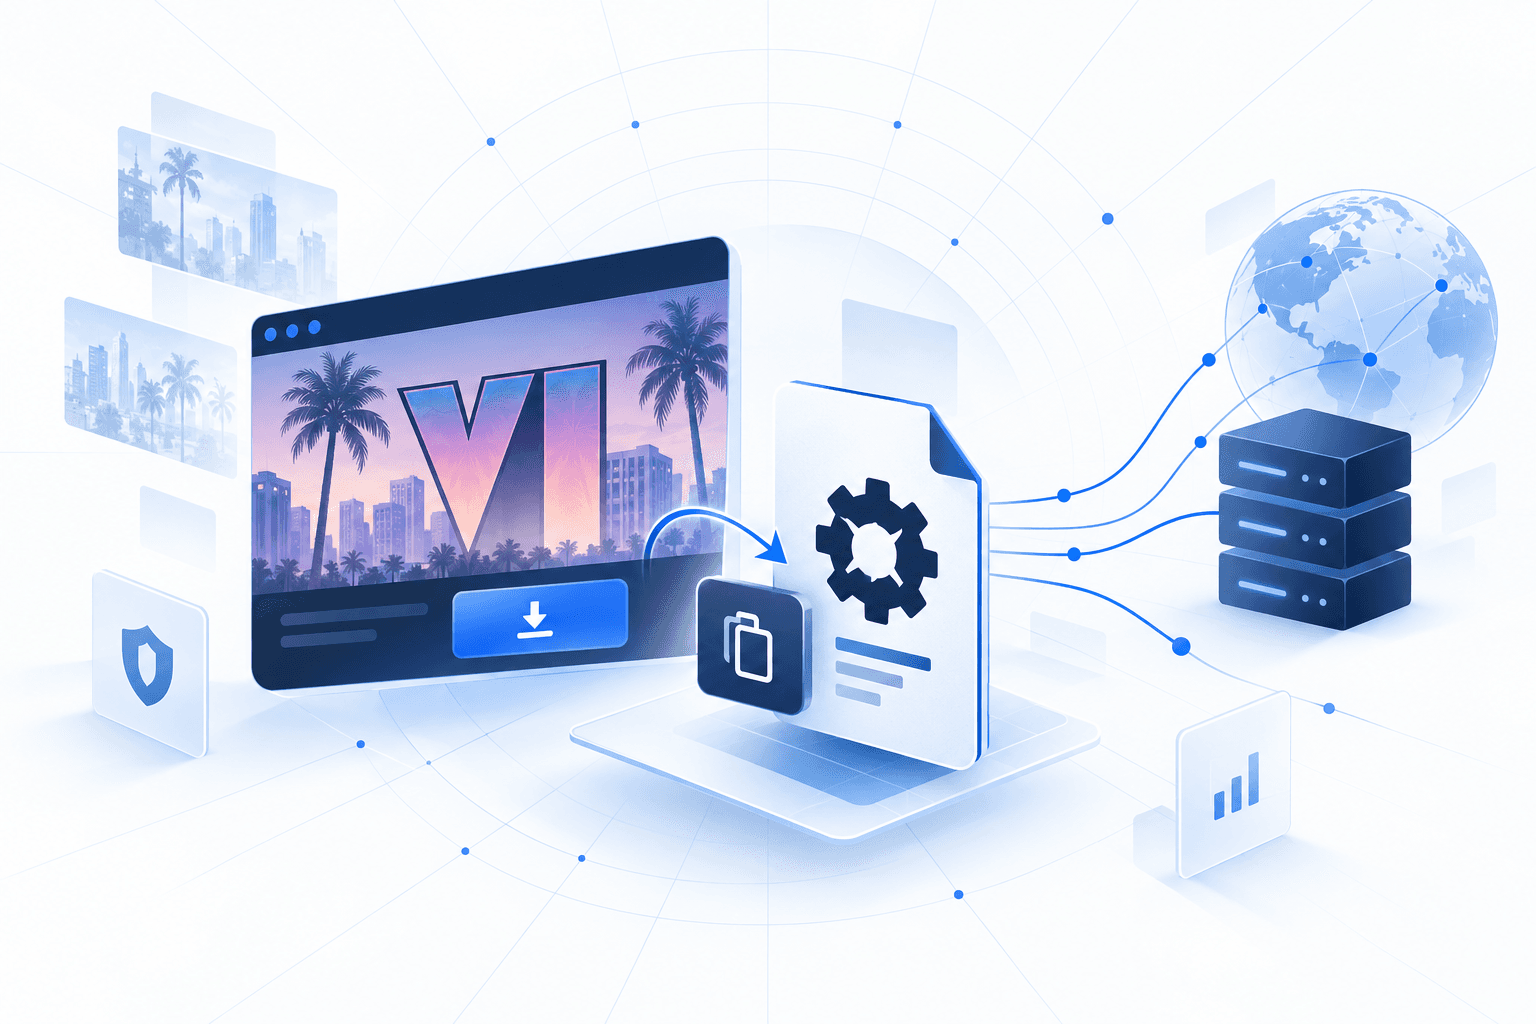
Bitdefender identified a campaign targeting Windows users with a fake Grand Theft Auto VI cloud-streaming client that installs information-stealing malware. The site gta6cloud.nexus exploits demand for a PC version, offering a ZIP download and a ClickFix lure that persuades visitors to execute a PowerShell command. The GTA6Cloud launcher displays a decoy game page while downloading a DLL loader, which abuses a legitimate Windows executable for DLL sideloading and injects a Rust-based infostealer into legitimate processes.

The malware steals browser credentials and session data, gaming and cryptocurrency wallet information, AI and developer credentials, clipboard contents, and screenshots, then sends the data to attacker-controlled infrastructure. Encrypted configuration, hidden files, process injection, and registry-based persistence help conceal and sustain the infection. Users who executed the command should treat their computers as compromised: Bitdefender advises disconnecting affected devices from the internet, scanning for malware, and securing accounts and changing important passwords from a clean device.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event
  1. Reported Nov 20, 20261d ago

    Bitdefender uncovers fake GTA VI client distributing a Rust-based infostealer

    Bitdefender identified gta6cloud.nexus distributing a fake GTA VI streaming client through a ZIP download and a ClickFix lure that persuades Windows users to execute PowerShell. The infection chain uses DLL sideloading and process injection to deploy a Rust-based information stealer capable of collecting browser secrets, gaming and cryptocurrency data, developer credentials, clipboard contents, and screenshots.

    Fake GTA VI PC client spreads malware through a ClickFix attack
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

1 linked
Windows

Observables

11 linked

Indicator values are masked on this page. View all 11 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.