
Intel-led Threat and Exposure Management.
Mallory unifies threat intelligence with your attack surface, ranks what matters by what's exposed and what attackers are actually doing, and routes that prioritized work into the tools you already run.
- Nearly 9,000Intelligence sources processed continuously
- Intelligence GraphActors, campaigns, CVEs, products, observables
- Your stackCloud, code, identity, SIEM, SOAR, ticketing, chat, MCP, and more
Answer it in seconds.
Mallory investigates your attack surface and the relevant threat intelligence, gathers the evidence, and gives you a prioritized view of the potential exposure.
One platform for all of your threat and exposure needs.
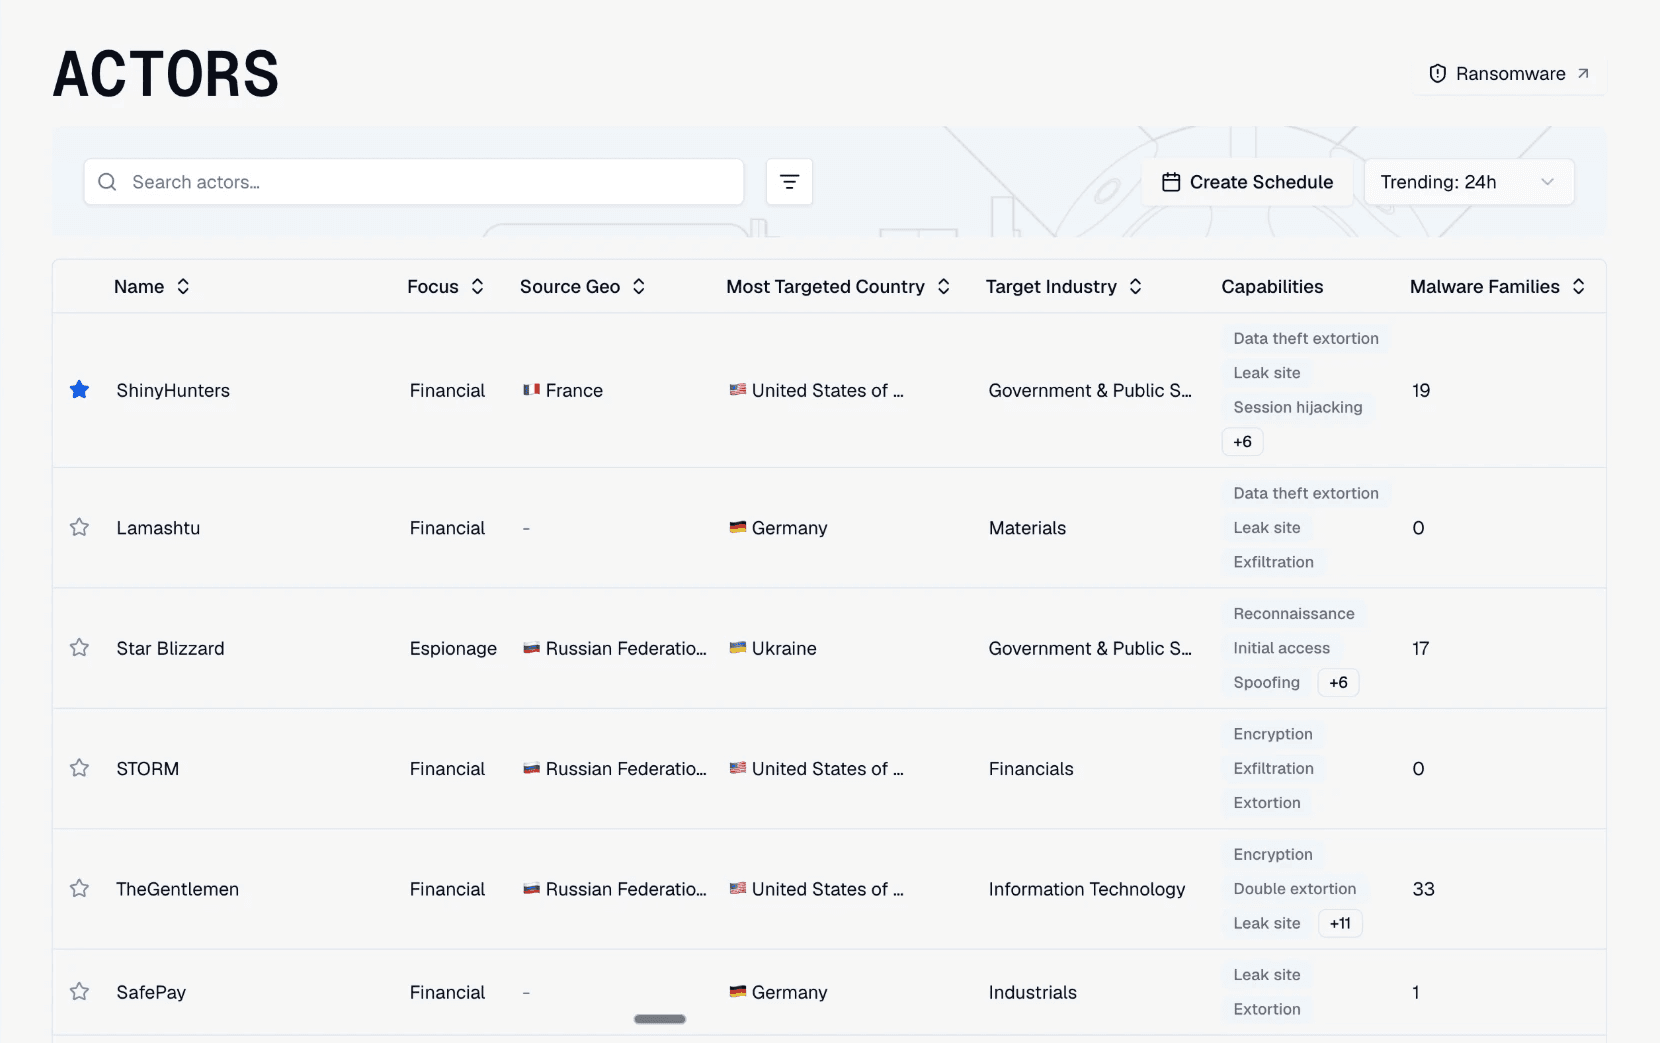
Threat Intelligence
Cut the manual correlation work out of your morning triage.
Mallory attaches asset, actor, and exploit context to a finding automatically, correlating nearly 9,000sources (vendor feeds, OSINT, dark web monitoring, ISAC/ISAO shares, and advisories) into one entity graph. What reaches your team is already scoped to your environment.
Exposure Management
Fix what's actually exploitable first.
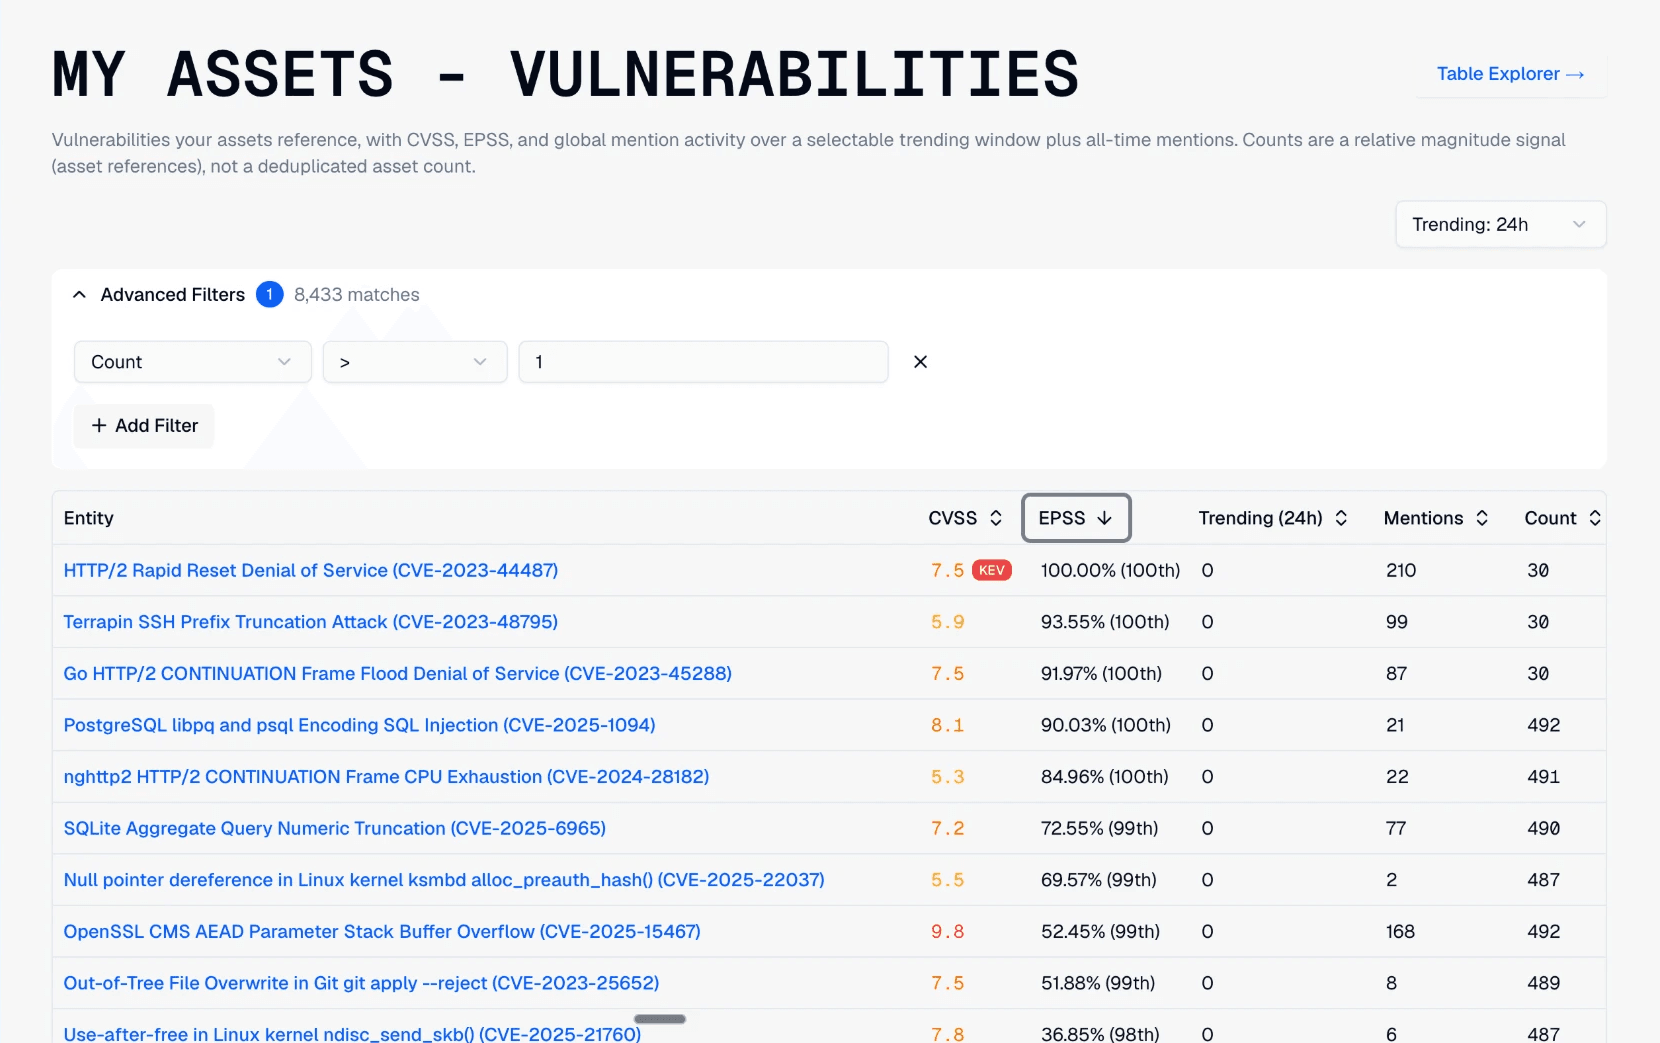
Mallory prioritizes vulnerabilities by what adversaries relevant to your industry are targeting, whether the exploit path is reachable in your environment, and whether the exposure is confirmed present, not by CVSS alone.
- Targeted by adversaries in your industry
- Exploit path reachable
- Exposure confirmed present
A finding that would sit mid-queue on severity moves to the top when all three are true.
From collection to action, on the stack you already run.
Follow one finding through the four stages.
Vendor feeds, OSINT, dark web monitoring, and Mallory's own collection. Records are deduplicated and entity-resolved on arrival.
- Vendor feeds
- OSINT
- Dark web monitoring
- Mallory's own collection
- Deduplicated records
- Entity-resolved records
The Intelligence and Exposure Graph matches findings against your asset inventory and tech stack before they reach your team.
- Intelligence and Exposure Graph
- Your asset inventory
- Your tech stack
- Findings scoped to your environment
The Mallory Agent turns findings into prioritized cases for CVE triage, red team recon, threat hunts, and detection gap assessment.
- Scoped findings
- CVE triage
- Red team recon
- Threat hunts
- Detection gap assessment
Runs on the AI you've already bought and routes work into your cloud, identity, ticketing, chat, SIEM, and SOAR tools.
- Prioritized cases
- Cloud
- Identity
- Ticketing
- Chat
- SIEM
- SOAR
Pick your role.
Reduce risk faster by turning thousands of exposures into the few risks that need remediation.
One queue replaces five disconnected dashboards.
Spend your mornings acting on what's relevant, not skimming a feed of everything published that day.
Walk into an engagement with the recon already done.
TTPs, reachable assets, and confirmed exposure.
Hunt with a hypothesis, not a blank page.
See which of your assets an adversary is already targeting.
Mallory closes the loop, not just the alert.
The queue reflects live exploitation and reachability.
What's under the hood.
Platform details. Deployment, API and data-handling specifics are available from your Mallory rep.
- Sources
- nearly 9,000 sources processed continuously: vendor feeds, OSINT, dark web monitoring, ISAC/ISAO shares, and advisories, plus Mallory's own collection.
- Ingest
- Records are deduplicated and entity-resolved on arrival.
- Intelligence Graph
- Actors, campaigns, CVEs, products, and observables in one entity graph.
- Correlation
- Findings are matched against your asset inventory and tech stack before they reach your team.
- Prioritization signals
- Adversaries relevant to your industry are targeting it. The exploit path is reachable in your environment. The exposure is confirmed present.
- Mallory Agent output
- Prioritized cases for CVE triage, red team recon, threat hunts, and detection gap assessment.
- Where work goes
- Cloud, code, identity, SIEM, SOAR, ticketing, chat, MCP, and more.
- AI
- Runs on the AI you've already bought.
- Compliance
- AICPA SOC 2 Type 2.
Why you can check the work.
Provenance
Every answer is evidence-based and cites its sources.
Policy guardrails
Agents act within your own policy.
Human in the loop
Analysts and agents work the same thread. You can see, question, and override the agent's work.
Accuracy
Verdicts are validated.
See what Mallory ranks first in your environment.
Start a free trial, or ask your Mallory rep for a walkthrough.