ClickFix and Cache Smuggling Techniques Used for Malware Delivery
Social Engineering & Fraud · 3 sources · Updated 4mo ago · First seen Oct 27, 2025
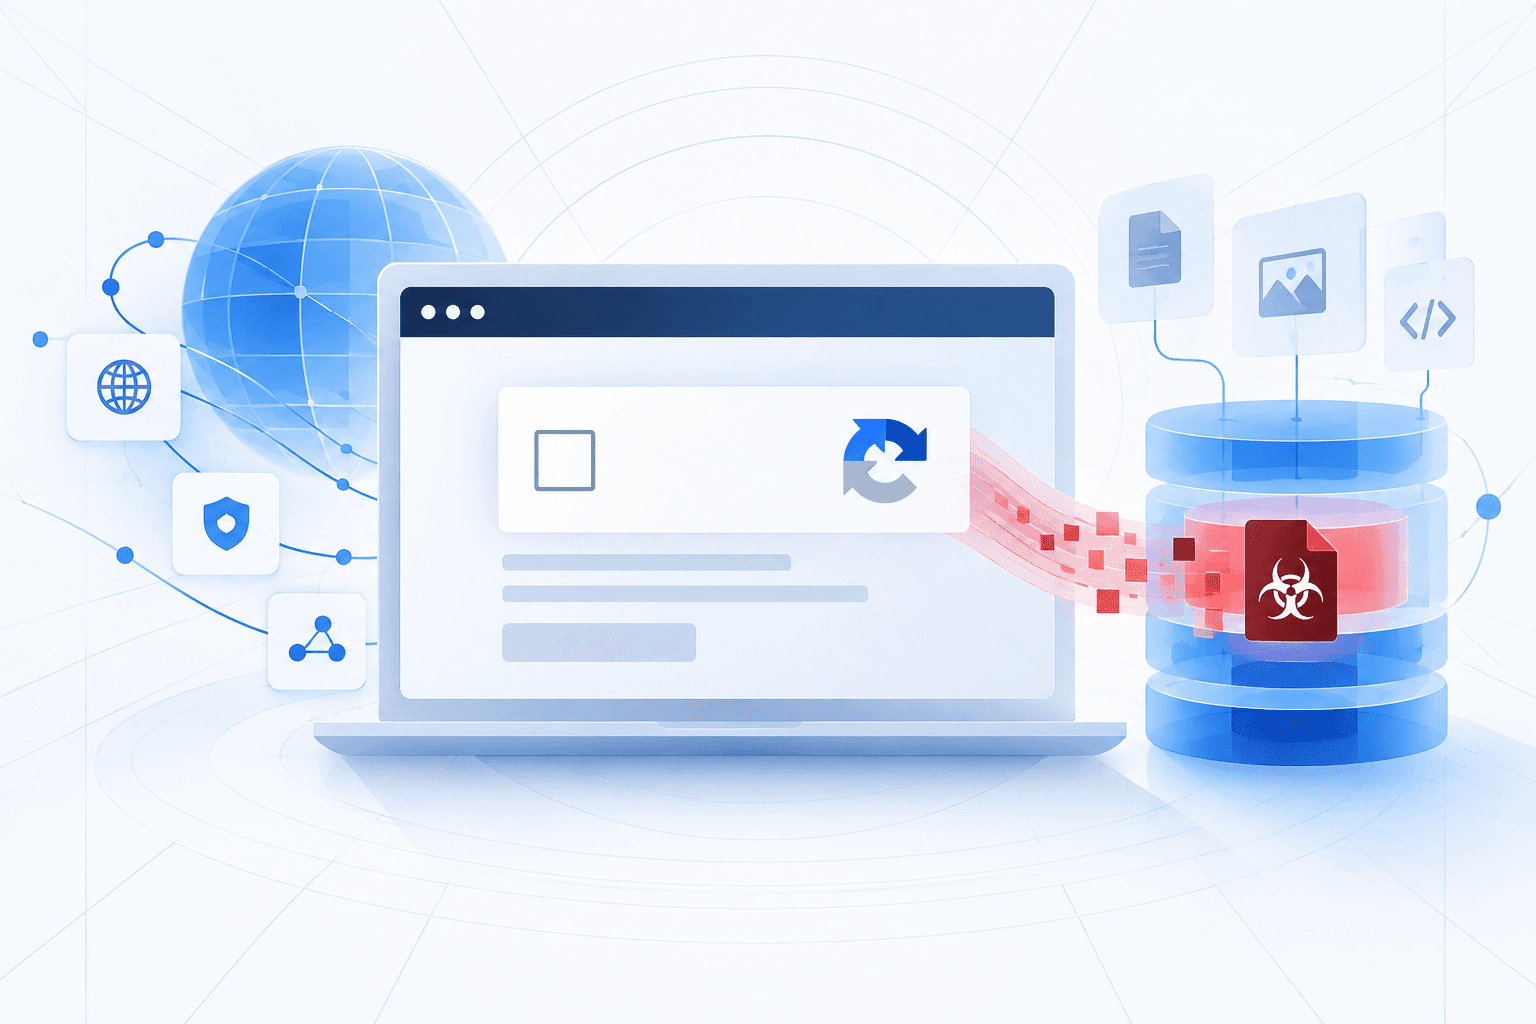
Attackers are leveraging ClickFix-style phishing pages to deliver malware by exploiting browser cache mechanisms and social engineering tactics. In these campaigns, malicious websites masquerade as Captcha tests and prompt users to execute clipboard-injected commands via the Windows Run dialog, enabling the execution of arbitrary code. A notable evolution of this technique involves using cache smuggling, where the initial loader extracts the second-stage payload directly from the browser's cache, bypassing the need for direct web requests and evading some detection mechanisms.
Recent campaigns have combined these methods with the deployment of remote access tools such as NetSupport RAT, using ClickFix lures to infect hosts and establish covert access. Multiple threat clusters have been observed utilizing remote monitoring and management (RMM) software for persistent, stealthy access to compromised systems. These developments highlight the increasing sophistication of social engineering and technical delivery mechanisms in modern malware campaigns, emphasizing the need for heightened user awareness and advanced detection strategies.