
Loading story…
The European Union Agency for Cybersecurity (ENISA) has been elevated to a "Root"-level participant in the Common Vulnerabilities and Exposures (CVE) program, granting it the authority to assign CVE identifiers and publish CVE records. This new role positions ENISA as a central coordinator for vulnerability disclosures across the European Union, aiming to reduce fragmentation, strengthen cross-border coordination, and accelerate responsible disclosure processes. ENISA will also serve as a primary contact point for vulnerabilities reported by or to the European Union Computer Security Incident Response Teams (CSIRTs).
This development is part of broader EU efforts to enhance cybersecurity, including the launch of the European Union Vulnerability Database as a counterpart to the U.S. National Vulnerability Database. ENISA is also developing a "Single Reporting Platform" for manufacturers to disclose actively exploited vulnerabilities, a requirement that will become mandatory under the Cyber Resilience Act starting in 2026. These initiatives are expected to improve the EU's ability to manage and coordinate cybersecurity vulnerabilities and bolster digital security across the union.
See the reporting duties and controls this puts on the clock.
1 event from the most recent confirmed update back to the earliest known activity.
ENISA was designated a CVE Program Root, giving it authority to oversee and delegate CVE Numbering Authority functions within its scope and expanding its role in the vulnerability disclosure ecosystem in Europe.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See what this changes for your reporting obligations and which controls it puts on the clock.
3 references tracked. Mallory keeps watching after this page renders.
socket.dev
Open sourcebankinfosecurity.com
Open sourcegovinfosecurity.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
ENISA announced that the **NATO Cyber Security Centre** and AI startup **AISLE** have become **CVE Numbering Authorities** under the **ENISA Root**, giving them the ability to assign `CVE` identifiers to disclosed software vulnerabilities. NATO’s authority covers eligible flaws across the NATO enterprise, while AISLE is limited to vulnerabilities discovered in its own products. The move expands the organizations able to name and track vulnerabilities and adds to ENISA’s growing role in the CVE ecosystem. The designation comes amid broader changes in vulnerability management after continuity and governance concerns around the CVE program in 2025 and as AI speeds up vulnerability discovery. ENISA now oversees 20 numbering authorities under its root, including organizations added directly and others transitioned from the MITRE Root, while parallel initiatives such as CIRCL’s **Global CVE Allocation System (GCVE)** highlight a wider push to diversify how software flaws are cataloged and tracked.
Aug 10, 2026
European Union officials said they want to help strengthen and modernize the **Common Vulnerabilities and Exposures (CVE) Program** after a 2025 contracting scare involving MITRE raised concerns about the long-term resilience of a system widely used to track and identify software flaws. ENISA cybersecurity official Hans de Vries said EU member states asked the agency to examine how to reinforce the process, arguing that such a critical global mechanism should not rely on a single U.S. government contract, while U.S. policymakers are weighing legislation that could formalize the program and expand **CISA** oversight. Officials and experts also warned that weak governance or political fragility could splinter vulnerability tracking into competing systems, undermining a core pillar of global cyber defense. The debate has also turned to improving the quality and machine-readability of CVE records at issuance, as **AI-enabled** attacks accelerate exploitation and reduce the value of delayed enrichment; CISA said a brief renewal delay in April 2025 did not interrupt operations and that **MITRE** remains the program operator.
Jun 29, 2026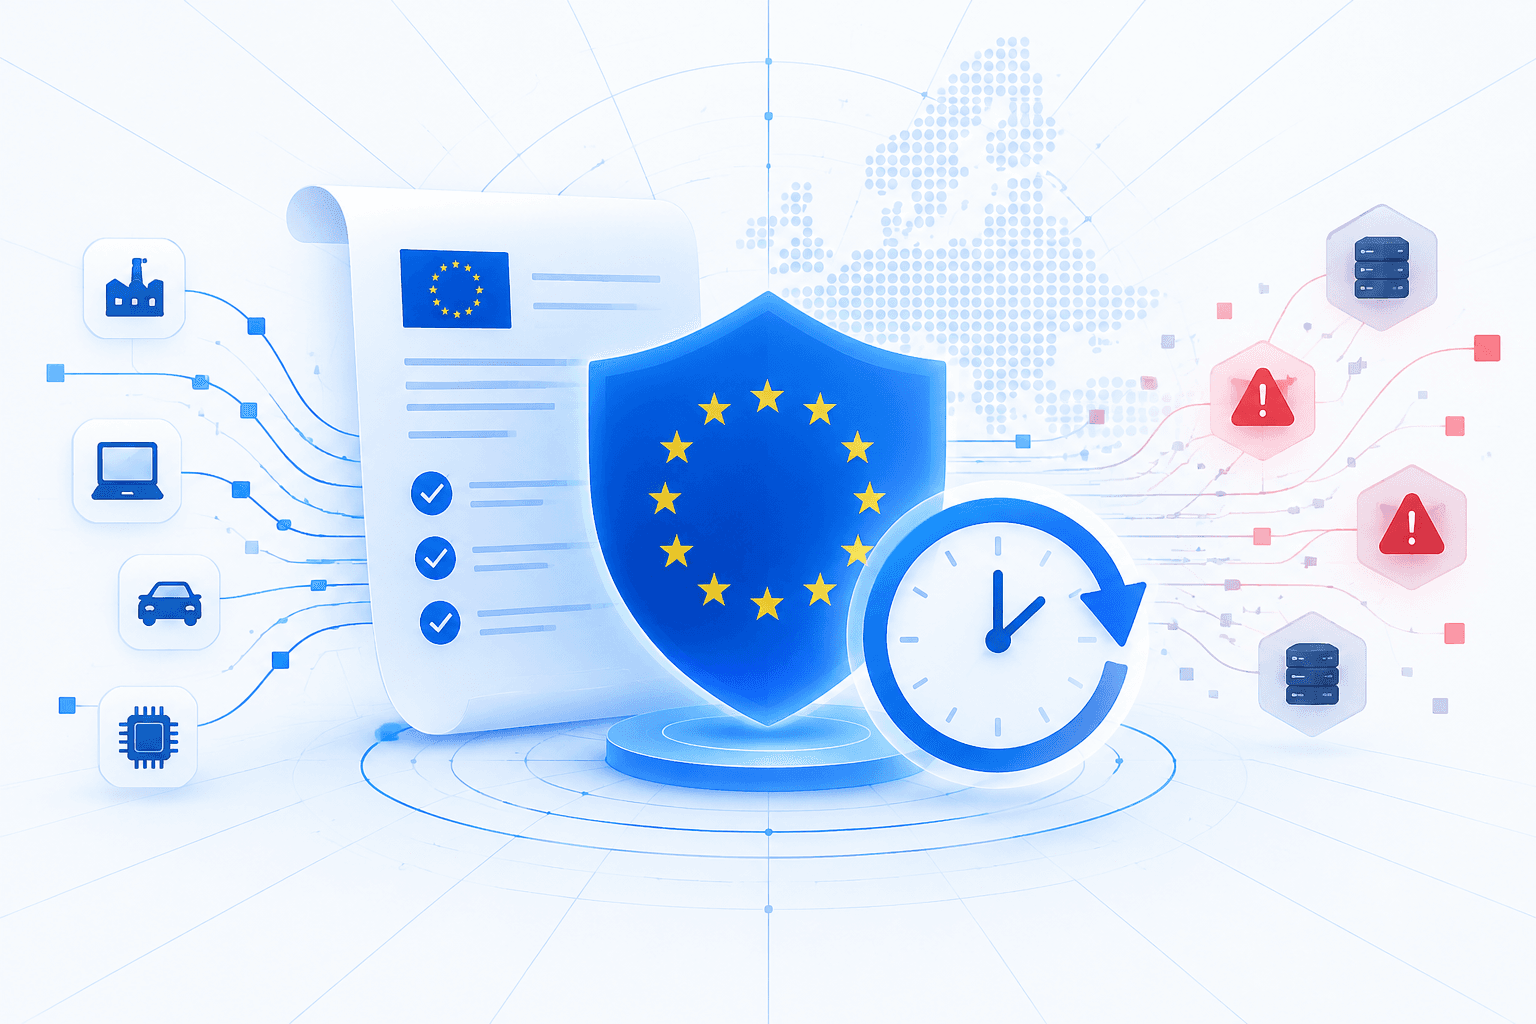
The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, has begun its vulnerability-reporting phase: manufacturers of hardware and software products with digital elements sold in the EU must report actively exploited vulnerabilities and severe incidents to ENISA and relevant national CSIRTs. The staged reporting obligations, including an initial report within 24 hours, apply to products already on the market as well as new offerings. The CRA took effect in December 2024, with conformity-assessment body notifications beginning in June 2026; full enforcement and mandatory CE marking are scheduled for December 2027. Organizations subject to the regulation need established processes to rapidly classify incidents, verify production impact, coordinate legal, security, and product stakeholders, and make defensible disclosures amid overlapping requirements under GDPR, NIS2, DORA, SEC rules, and anticipated CIRCIA obligations.
Sep 21, 2026