OpenAI Codex CLI Command Injection Vulnerability
Emerging Technology Risk · 3 sources · Updated 5mo ago · First seen Dec 3, 2025
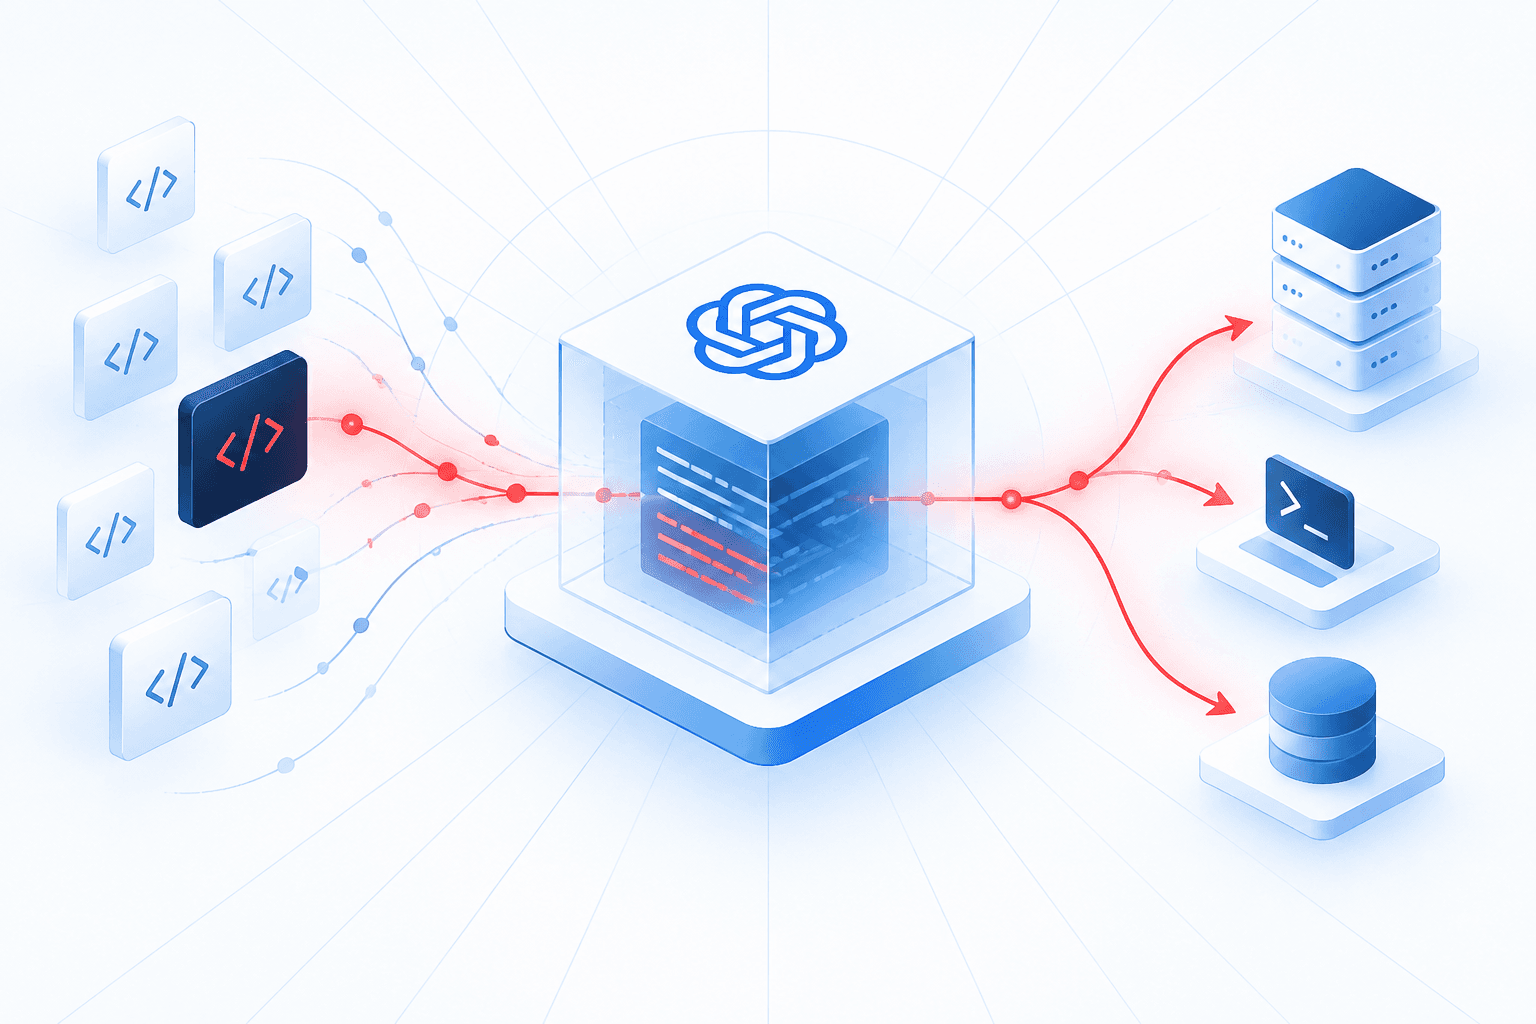
OpenAI addressed a critical command-injection vulnerability in its Codex CLI tool that allowed attackers to execute arbitrary commands on developer machines by hiding malicious configuration files within code repositories. The flaw, disclosed by Check Point and patched in Codex CLI version 0.23.0, exploited the way the tool automatically loaded and executed MCP server entries from project-local configuration files. If a repository contained a file that redirected the configuration directory and included a malicious MCP server command, Codex CLI would execute those commands as soon as a developer ran the Codex command, potentially compromising the system.
This vulnerability turned routine developer workflows into attack vectors, as simply running Codex CLI in a tampered repository could result in the execution of hidden commands without the user's knowledge. OpenAI released a fix for the issue after being notified by Check Point, mitigating the risk of attackers hijacking developer machines through this vector. Security teams are advised to ensure all Codex CLI installations are updated to the latest version and to review repository sources before running AI-powered development tools.