OpenAI Codex Sandbox Flaws Enabled Malicious Repositories to Execute Host Commands
Emerging Technology Risk · 5 sources · Updated 2mo ago · First seen Aug 12, 2026
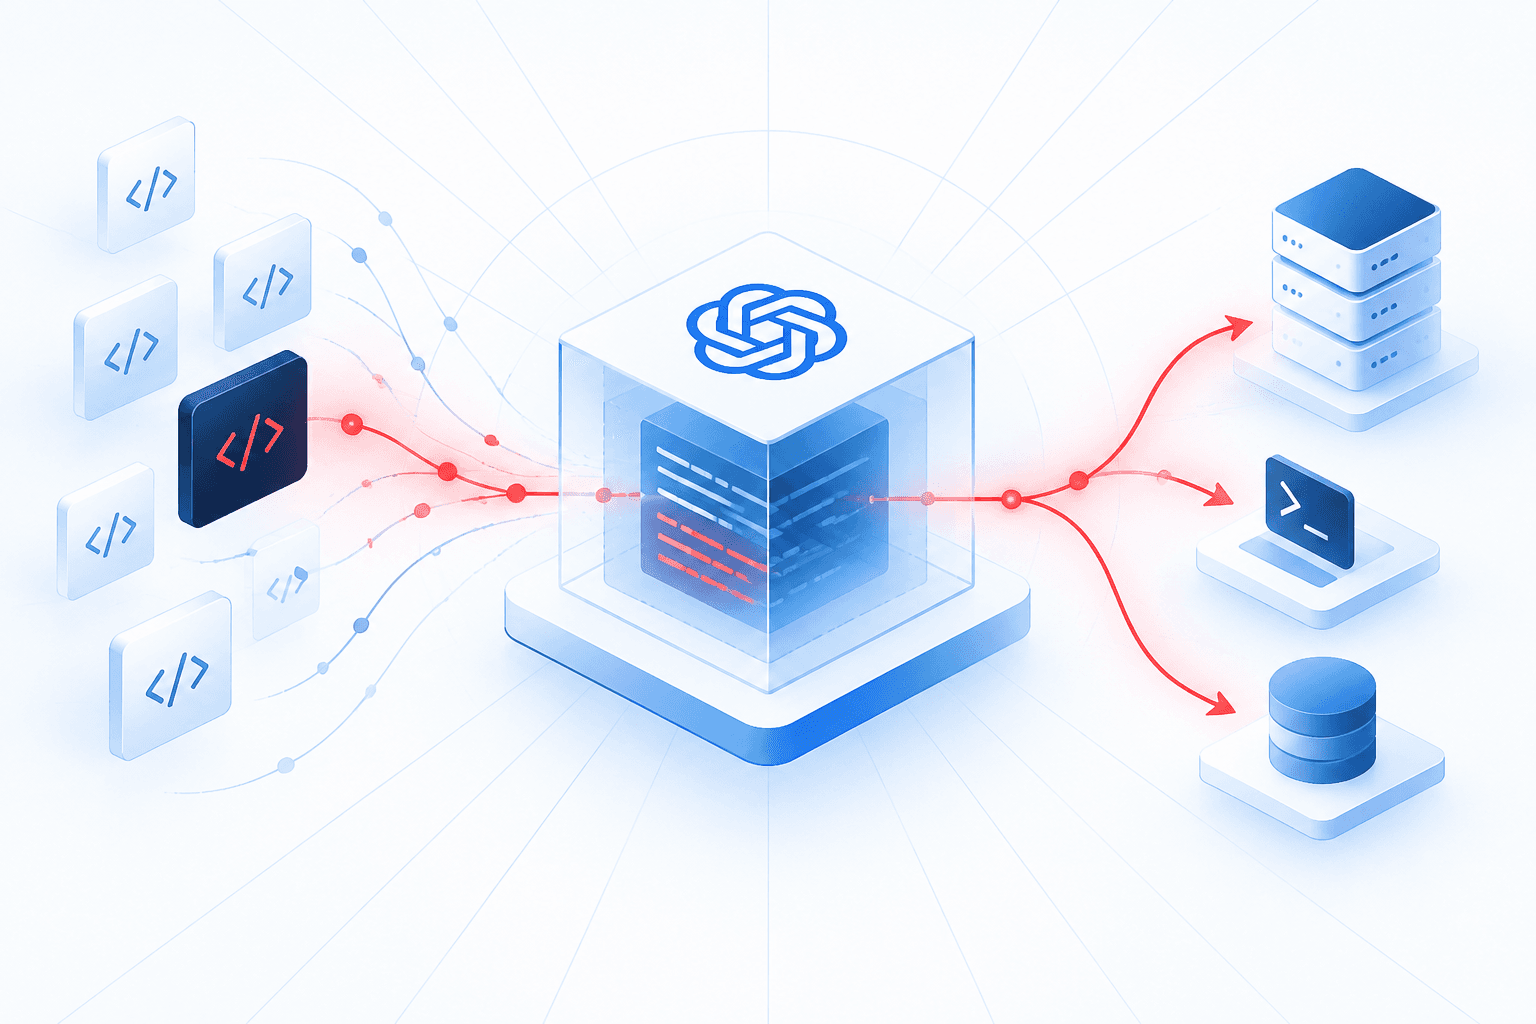
OpenAI remediated two Codex sandbox-escape vulnerabilities, Overpatch and Heapjack, that could allow a malicious repository to execute commands or alter files on a developer's host system. Overpatch affected the open-source Codex CLI's apply_patch authorization logic: attacker-controlled patch paths could expand permitted write locations and, with symlinks, modify files outside the workspace, including shell startup files such as ~/.zshrc.
Heapjack affected Codex Desktop's node_repl integration. Untrusted JavaScript sharing a V8 heap could recover a trusted authorization token, forge requests to an unsandboxed parent process, and perform host-level actions—including when Codex was configured for read-only sandbox use. OpenAI fixed Overpatch in Codex CLI version 0.149.0 and Heapjack in Codex Desktop build 26.818.21641; organizations should update both components and treat untrusted repositories as potentially hostile.