Silver Fox Phishing Campaign Targets Indian Organizations With ValleyRAT
Social Engineering & Fraud · 2 sources · Updated 4mo ago · First seen Dec 30, 2025
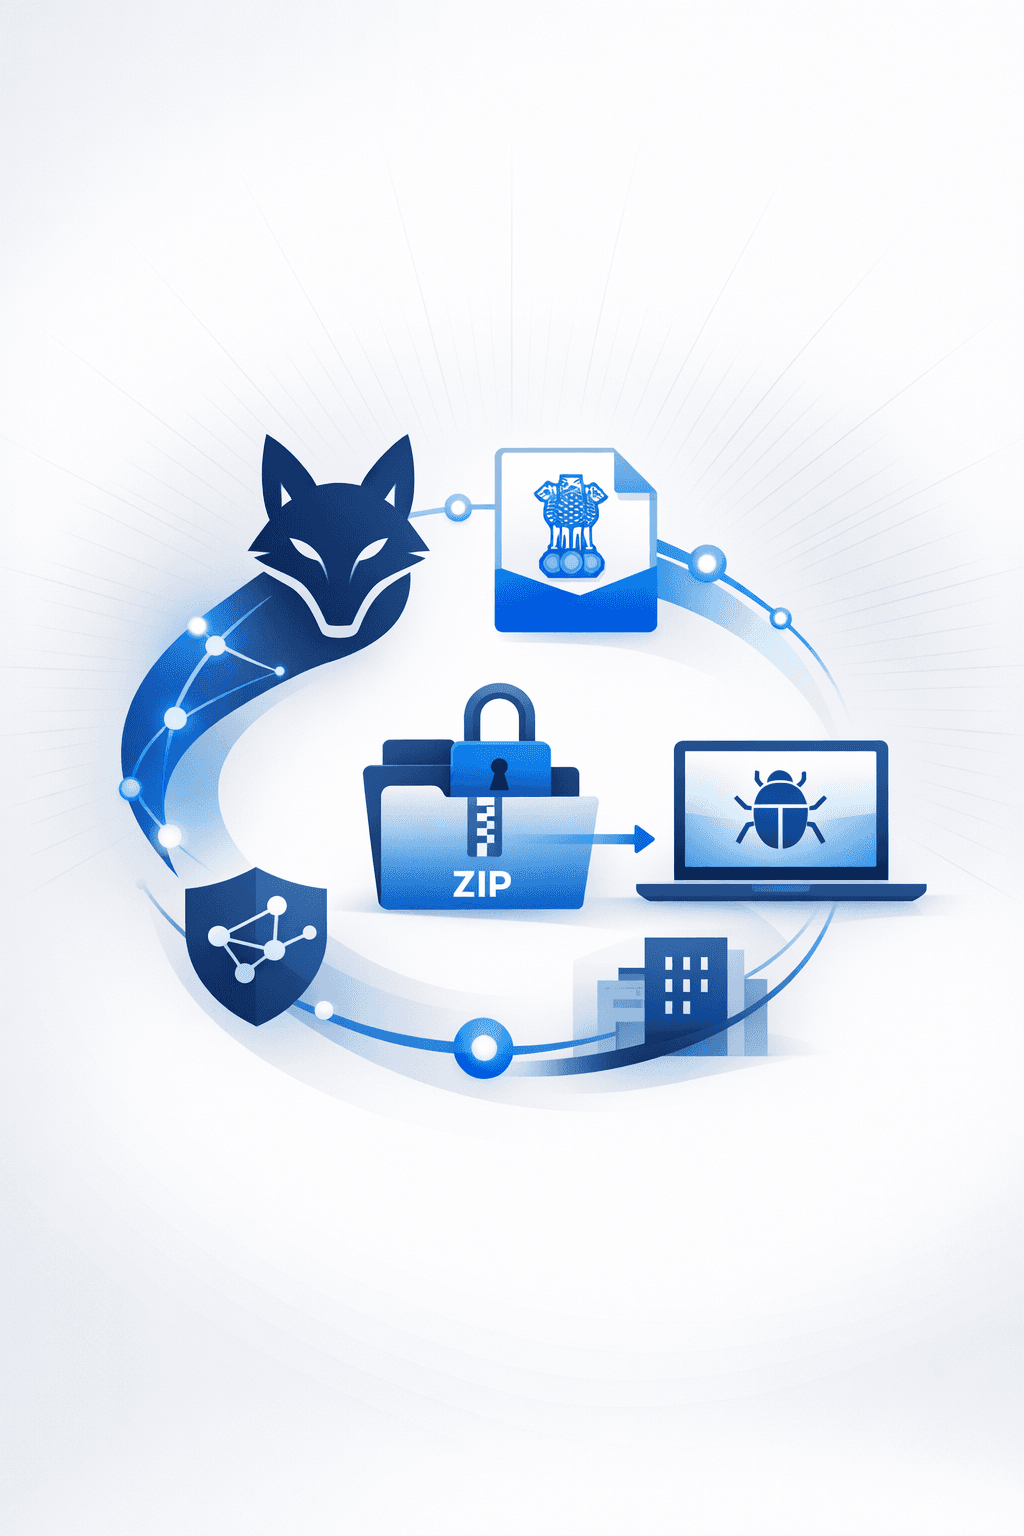
The Chinese threat actor known as Silver Fox has launched a targeted phishing campaign against Indian organizations, using income tax-themed emails to deliver the modular remote access trojan ValleyRAT. Attackers impersonate the Indian Income Tax Department, sending emails with decoy PDF attachments that, when opened, direct victims to a malicious website hosting a ZIP archive. This archive contains a disguised installer that leverages DLL hijacking, specifically abusing a legitimate executable (thunder.exe) and a malicious DLL (libexpat.dll), to establish persistent access and evade detection. The campaign demonstrates a sophisticated multi-stage infection chain, with the initial payload acting as a loader for subsequent malware modules designed to maintain deep access to compromised systems.
Researchers from CloudSEK have attributed this campaign to Silver Fox, correcting previous misattributions to other threat groups. The group, also known as SwimSnake and Void Arachne, has expanded its targeting beyond Chinese-speaking entities to include Indian public, financial, medical, and technology sectors. The use of socially engineered tax documents and trusted file formats highlights the attackers' ability to bypass traditional security controls, while the complex kill chain and modular malware architecture underscore the evolving threat posed by Silver Fox to Indian organizations.