LockBit 5.0 Ransomware Introduces Advanced Encryption and Maintains Global Dominance
Threat Actor Intelligence · 2 sources · Updated 4mo ago · First seen Jan 9, 2026
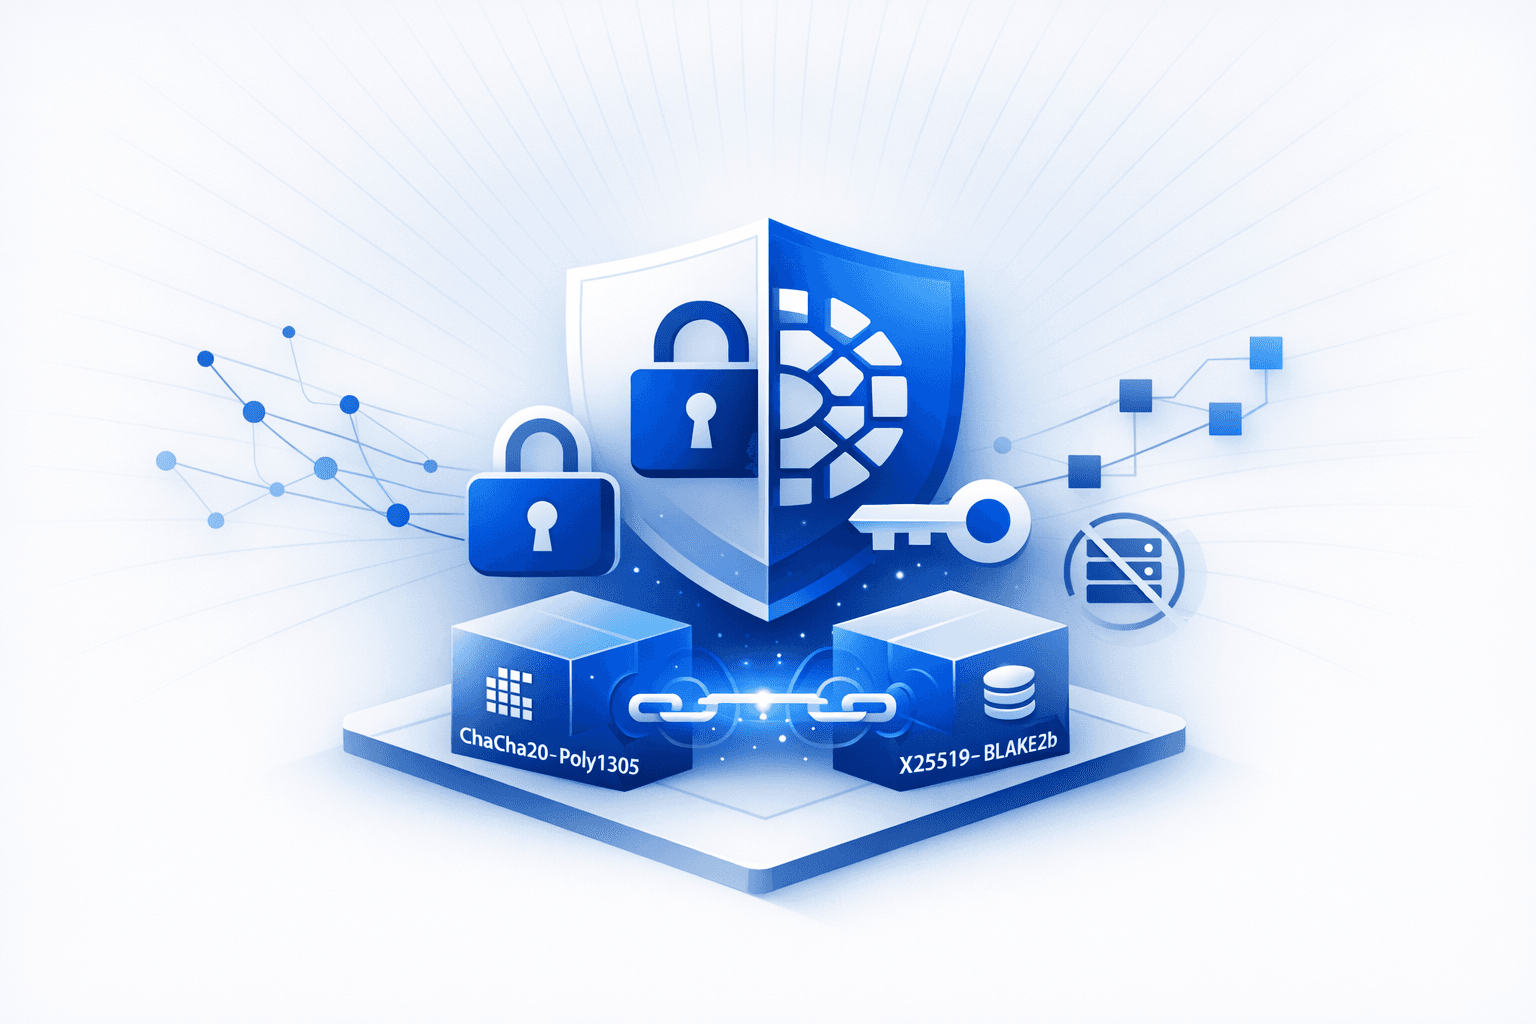
LockBit 5.0 has emerged as the latest evolution of the notorious ransomware-as-a-service operation, introducing sophisticated encryption algorithms and advanced anti-analysis techniques that significantly complicate detection and recovery efforts for targeted organizations. The malware now employs a combination of ChaCha20-Poly1305 for file encryption and X25519 with BLAKE2b for secure key exchange, while also terminating Volume Shadow Copy Service processes to prevent system recovery. LockBit 5.0’s runtime flexibility allows it to operate even without specific parameters, and its use of advanced packing and obfuscation further hinders static analysis by security professionals.
Despite increased law enforcement pressure, LockBit has sustained its position as a dominant global ransomware threat, accounting for a substantial share of attacks worldwide. The group’s operations have impacted a wide range of sectors, including IT, electronics, law firms, and religious institutions, resulting in billions of dollars in ransom payments and recovery costs. LockBit continues to leverage its dark web platform to publicly list compromised organizations and stolen data, using these tactics to pressure victims into paying ransoms.