Weaponized Document Lures Used to Deliver Malware and Remote Access
Social Engineering & Fraud · 2 sources · Updated 5mo ago · First seen Jan 14, 2026
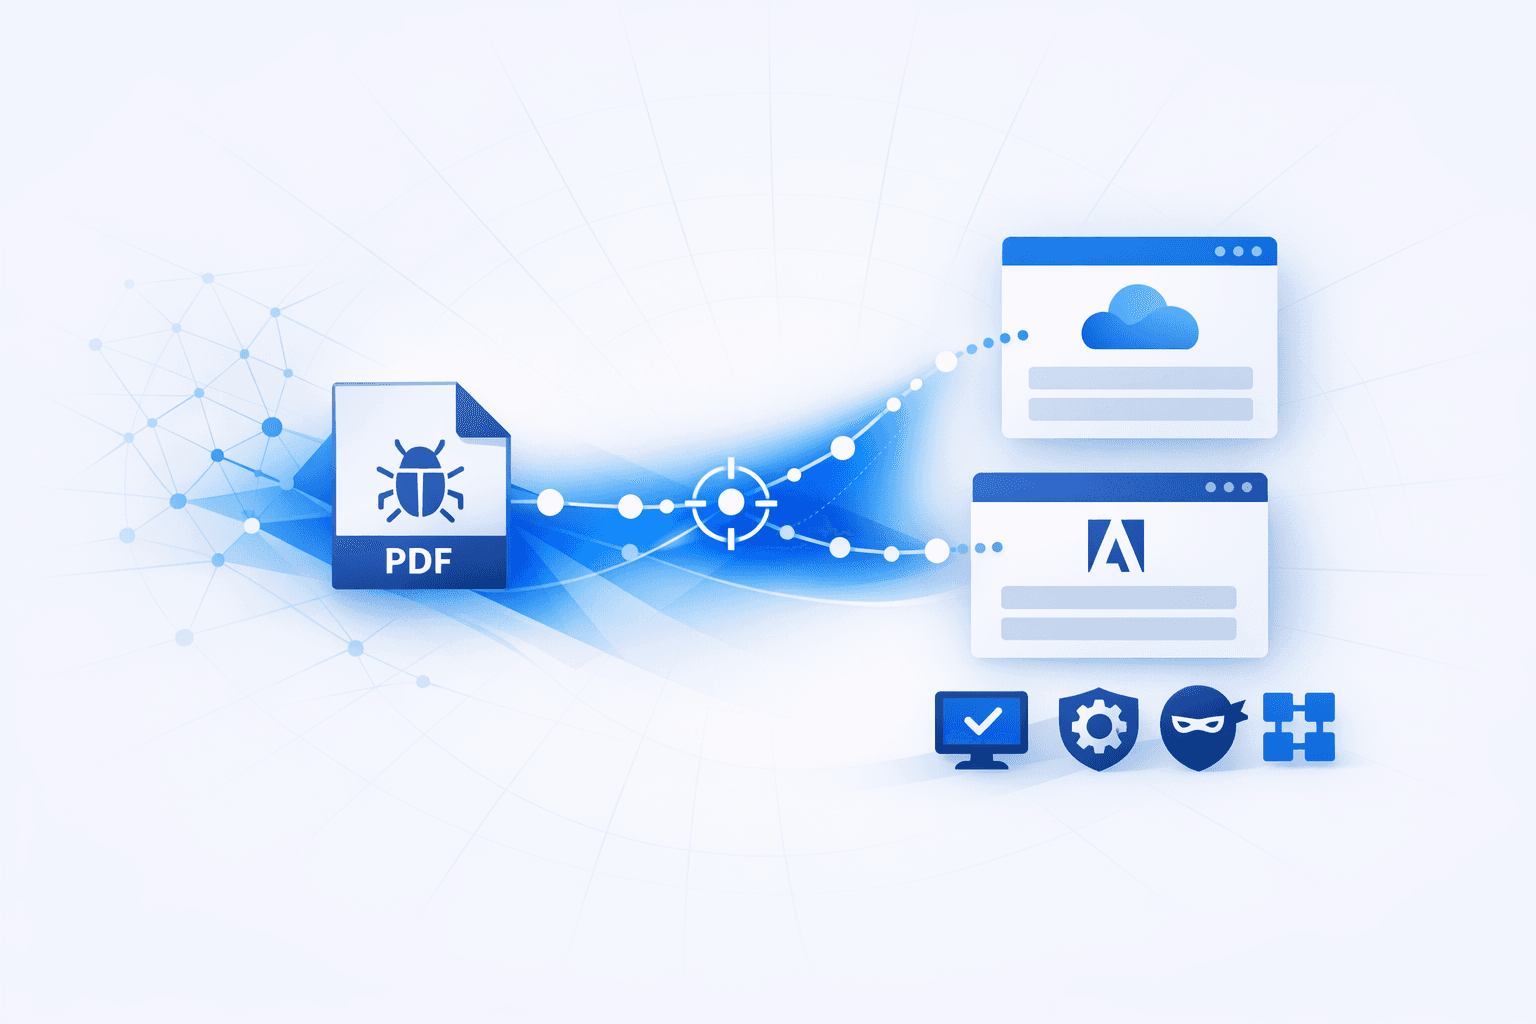
Multiple reports describe threat actors using document-themed lures to deliver malicious payloads while evading user scrutiny and defensive controls. ASEC-reported activity shows weaponized PDF files distributed via phishing (e.g., “Invoice,” “Payment”) that display a decoy image or a “Failed to load PDF document” error to push victims to click through to fake Google Drive/Adobe pages, ultimately installing legitimate RMM tools (e.g., Syncro, SuperOps, NinjaOne, ConnectWise ScreenConnect) signed with a valid certificate to blend in as administrative software rather than obvious malware.
Separately, research on APT36 / Transparent Tribe details a targeted espionage operation against Indian government, academic, and strategic entities using spear-phishing ZIP attachments containing oversized LNK files masquerading as PDFs; execution chains leverage mshta.exe to retrieve remote HTA content, decrypt and reconstruct payloads in memory, and deploy a RAT (tracked as ReadWriteRAT) with capabilities including encrypted C2, remote command execution, screenshot capture, clipboard access, and data theft. Other items in the set cover unrelated threats—WordPress SEO cloaking that selectively serves malicious content to verified Googlebot IP ranges, a vendor blog overview of Medusa ransomware activity, and reporting on CrazyHunter ransomware impacting Taiwan healthcare—indicating the commonality here is document/SEO deception techniques, not a single unified incident.