CNIL Fines Iliad Subsidiaries Free and Free Mobile for Security Failures Behind 2024 Data Breach
Regulatory & Policy · 5 sources · Updated 4mo ago · First seen Jan 14, 2026
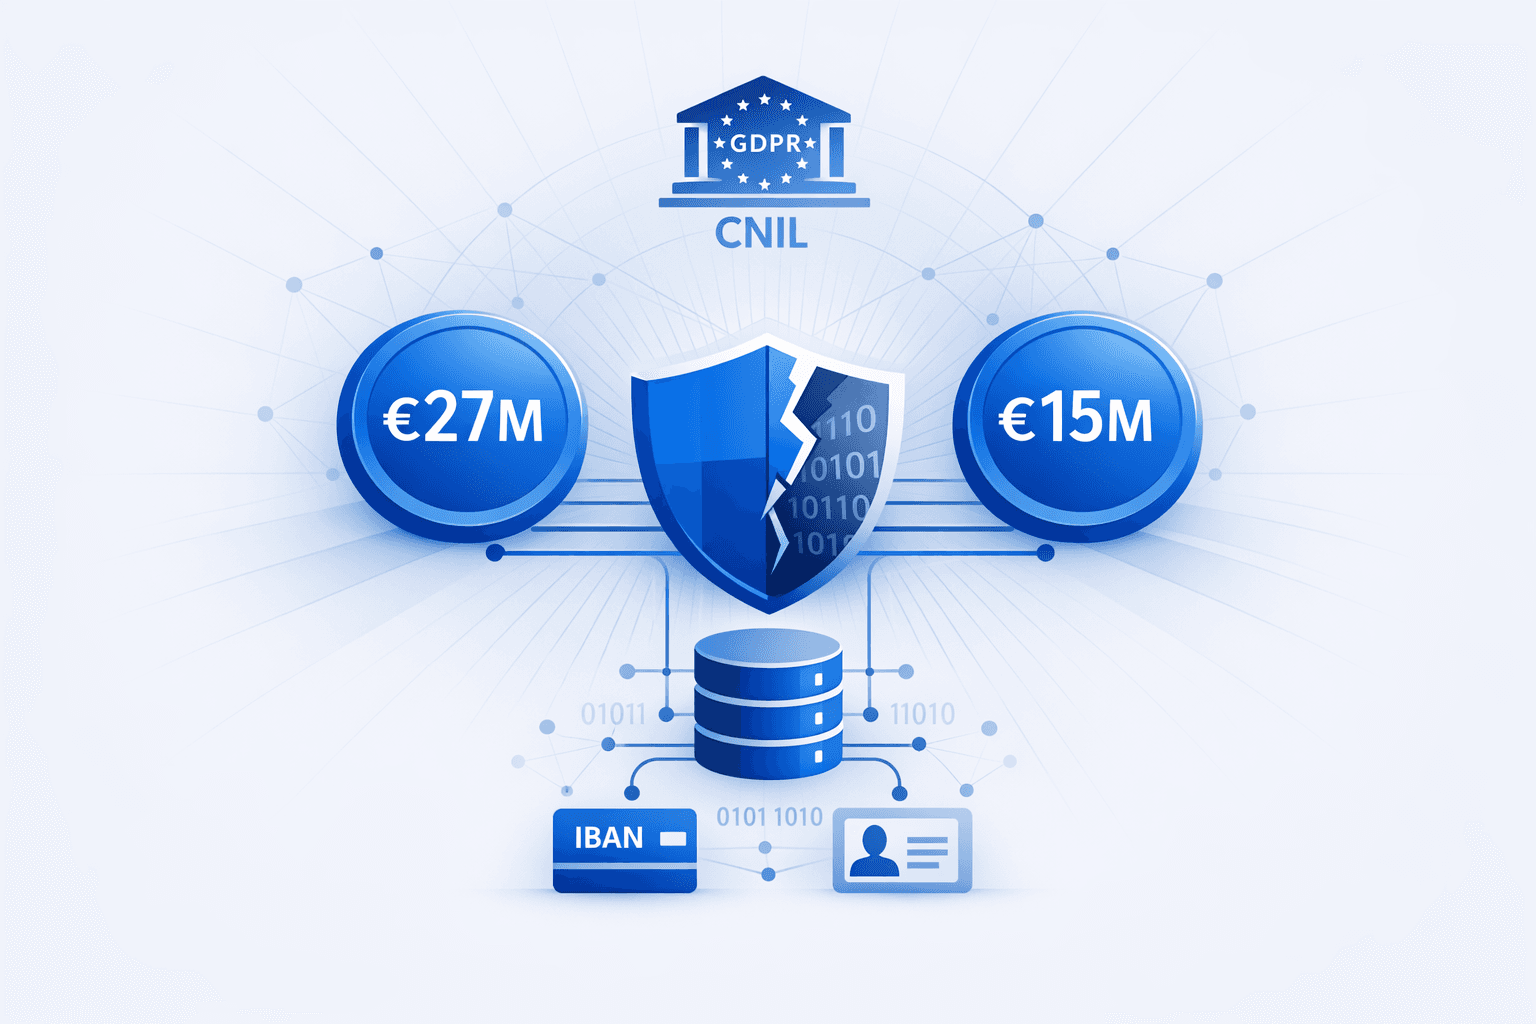
France’s data protection regulator CNIL issued a collective €42 million fine against Iliad Group subsidiaries Free and Free Mobile for GDPR violations tied to an October 2024 breach that exposed personal data for more than 24 million individuals, including sensitive financial identifiers such as IBANs. CNIL cited the scale and sensitivity of the compromised data, as well as the companies’ profits, in setting penalties of €27 million for Free and €15 million for Free Mobile.
Regulators said the intrusion was enabled by inadequate security controls, including a weak VPN authentication process and insufficient monitoring to detect anomalous activity. Reporting indicates the attacker accessed Free’s network via the corporate VPN, then reached Free Mobile’s subscriber management tool MOBO, which at the time allowed searches across both Free and Free Mobile customer datasets; exfiltration reportedly began in early October 2024 after initial access in late September. CNIL also faulted the companies for insufficient breach communications to impacted customers and for improper data retention (including retaining former subscribers’ data), while noting remediation steps have been initiated and further security improvements were ordered.