Backdoored LA-Studio Element Kit WordPress Plugin Enables Unauthenticated Admin Account Creation
Active Exploitation · 3 sources · Updated 5mo ago · First seen Jan 23, 2026
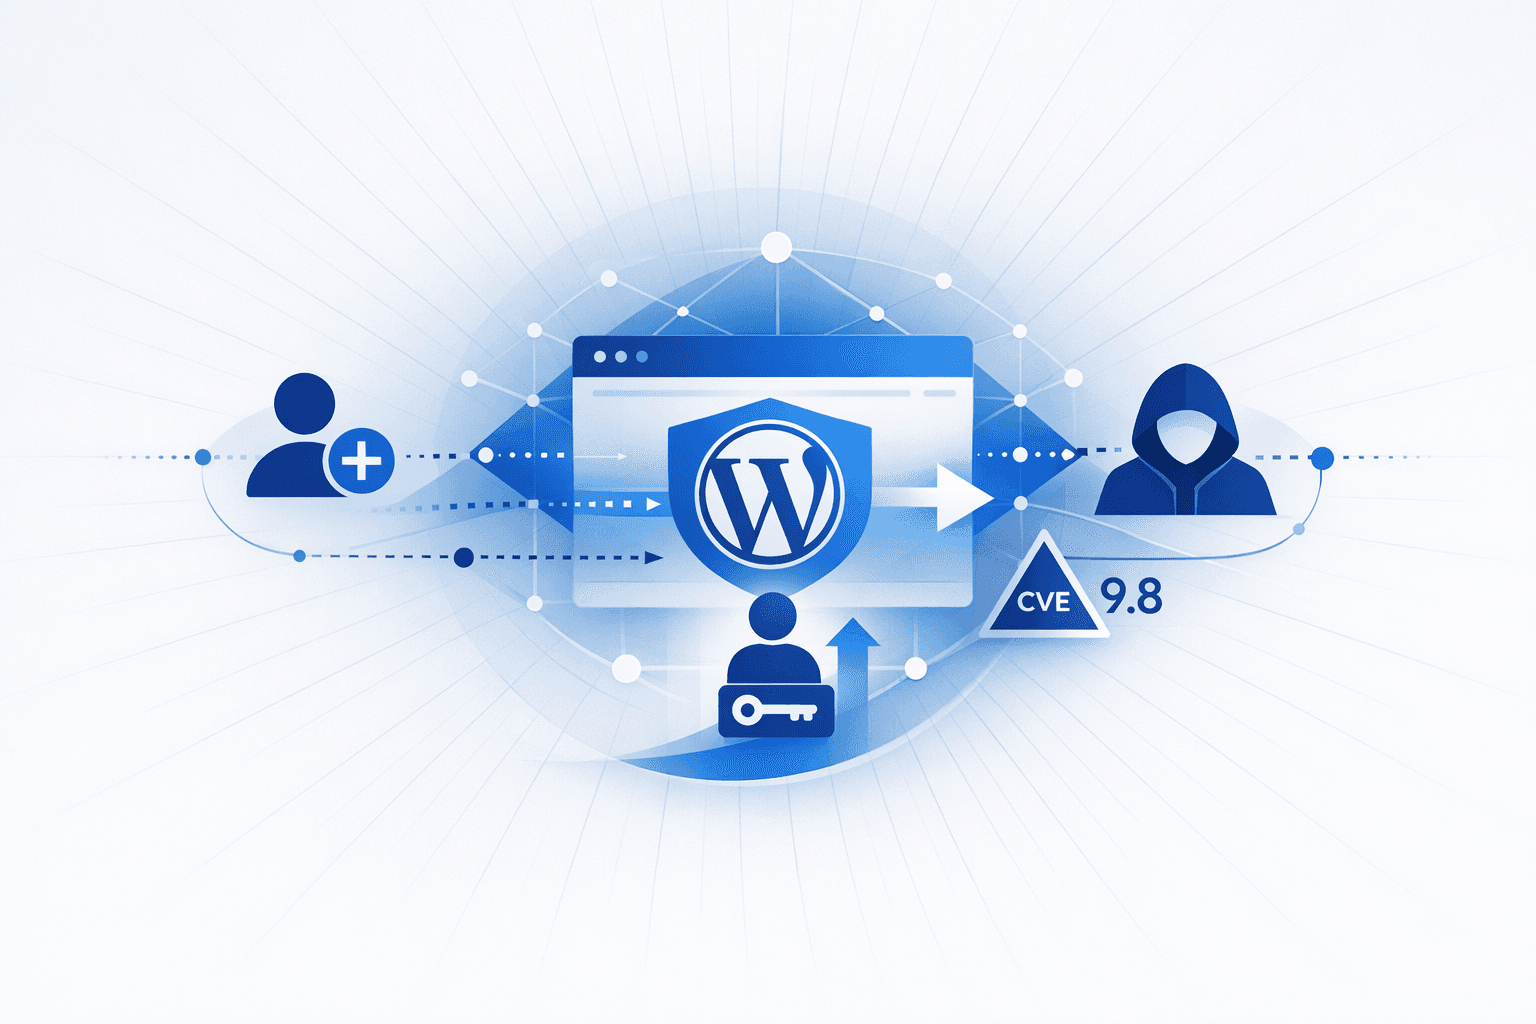
A critical backdoor was identified in the LA-Studio Element Kit for Elementor WordPress plugin (active on 20,000+ sites), enabling unauthenticated attackers to create administrator accounts and take full control of affected websites. The issue is tracked as CVE-2026-0920 with a CVSS 9.8 rating, and exploitation has been reported in the wild. The malicious logic was embedded in the plugin’s registration flow, allowing attackers to elevate privileges during account creation and then perform typical admin-level actions such as uploading malicious files, injecting spam, or redirecting visitors.
Technical reporting attributes the backdoor to sabotage: the vendor stated the malicious code was planted by a former employee, with changes occurring around the time their employment ended. The vulnerable path is the ajax_register_handle() function, where attackers can supply a specific registration parameter, lakit_bkrole, to obtain administrator capability; the code was described as obfuscated to evade detection. CVE documentation characterizes the weakness as improper restriction of user role assignment during registration (mapped to CWE-269) and points to the affected versions up to and including 1.5.6.3, along with upstream code references and the associated Wordfence advisory.