GitLab 2FA Login Protection Bypass Enabling Account Takeover
Vulnerability Disclosure · 2 sources · Updated 5mo ago · First seen Jan 23, 2026
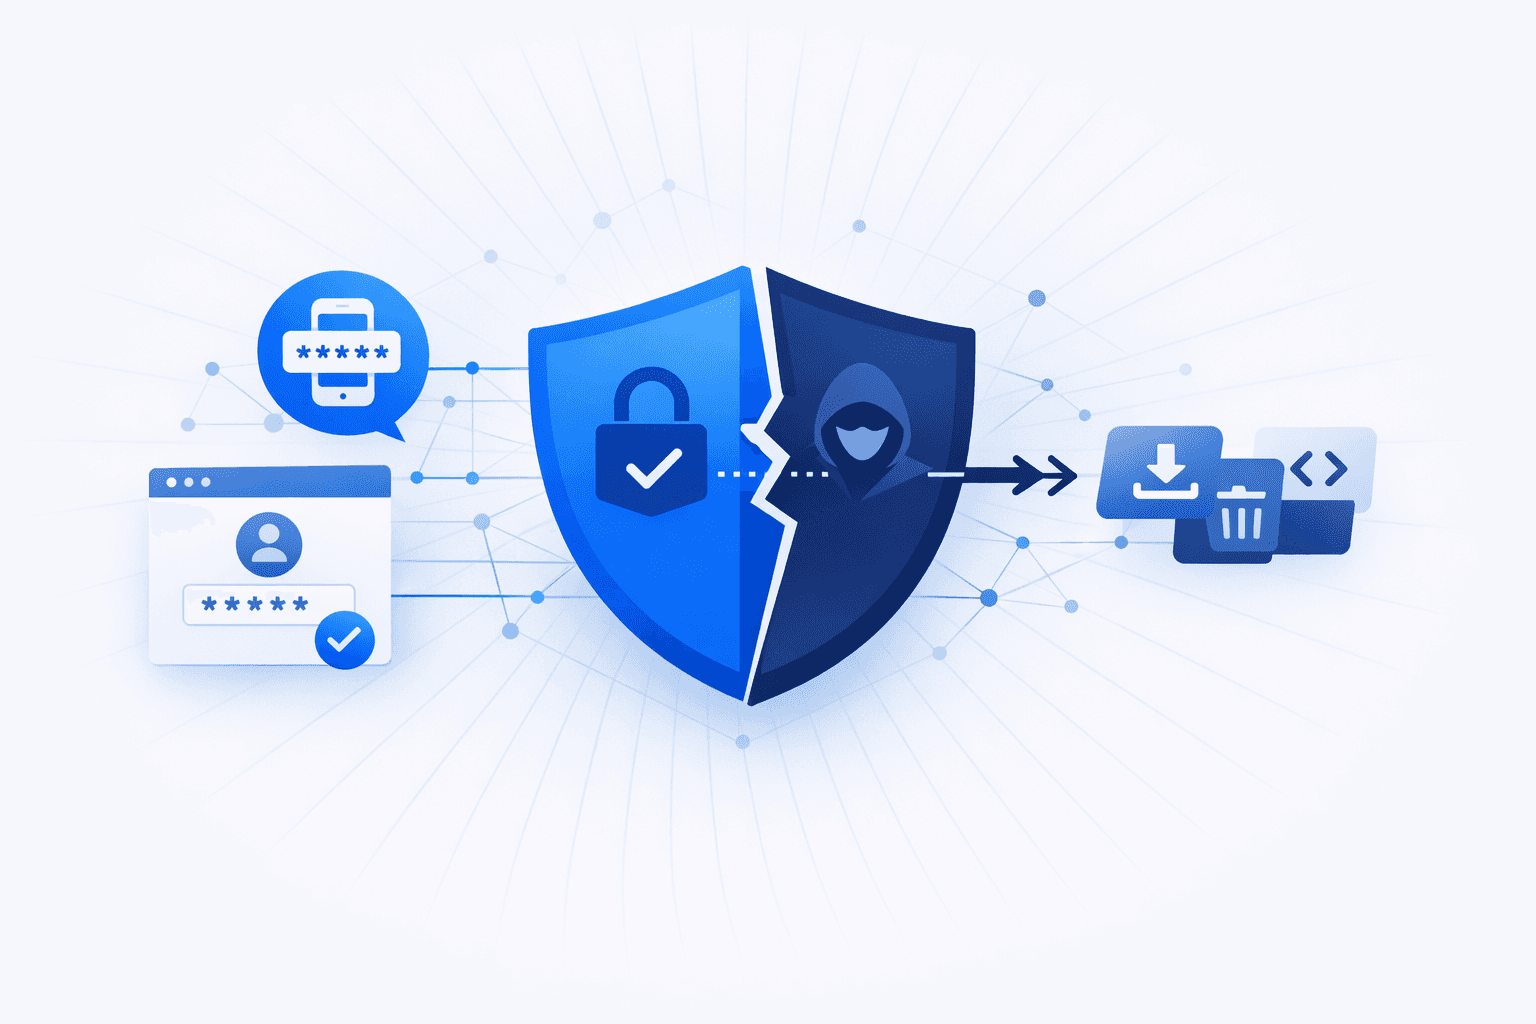
Reporting highlighted a GitLab authentication weakness in which a 2FA login protection bypass could allow attackers to take over accounts, enabling unauthorized access to GitLab instances and the ability to act as legitimate users. With access, an attacker could perform source-code actions such as downloading, altering, or deleting repositories, creating direct risks to software integrity and the SDLC.
Commentary from SANS Institute’s Johannes Ullrich noted that, in practice, attackers may find phishing and other social engineering more efficient for obtaining valid credentials than attempting to forge device credentials to exploit the bypass, but the end-state risk remains the same once passwords are obtained. Recommended defensive measures emphasized layered identity controls: enforce long/unique passwords, monitor for anomalous access patterns (e.g., logins without a corresponding MFA challenge), and ensure an incident response plan is ready if account compromise is suspected.