
Loading story…
Threat actors are running malware-free phishing campaigns designed to steal cloud-storage credentials by pushing victims through believable, multi-step lures. One observed operation sends corporate users emails requesting review of a fake “request order” via a linked PDF; the PDF then directs recipients to a convincing fake Dropbox login page that captures credentials and location data while returning an “incorrect username/password” error to reduce suspicion and encourage retries.
Separately, a large-scale cloud storage subscription/payment scam has been flooding inboxes worldwide with repeated “renewal” and “payment declined” messages claiming accounts will be blocked or files deleted unless immediate action is taken. The campaign uses many randomized sender domains and high-urgency, frequently personalized subject lines to drive clicks, indicating broad, high-volume social engineering aimed at harvesting account access or payment details rather than delivering traditional malware.

Get the infrastructure and lures behind it.
3 events from the most recent confirmed update back to the earliest known activity.
Forcepoint published research on a malware-free phishing campaign stealing corporate Dropbox credentials through fake 'request order' PDF lures. The multi-stage attack used a cloud-hosted blurred document and a convincing fake Dropbox login page, while also sending victim system and location data to an attacker-controlled Telegram bot.
Researchers reported that the cloud storage scam used static HTML redirectors hosted on storage.googleapis.com to send victims to scam domains. The landing pages impersonated cloud service portals, showed fake storage warnings, and funneled users toward affiliate offers and credit-card collection pages.
A large-scale phishing campaign began targeting users with repeated fake cloud storage renewal and payment-failure emails claiming accounts would be blocked or files deleted. The messages used personalized subject lines and urgency to drive victims into the scam flow.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
4 references tracked. Mallory keeps watching after this page renders.
forcepoint.com
Open sourcedarkreading.com
Open sourcecsoonline.com
Open sourcebleepingcomputer.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
A sophisticated, multi-stage phishing campaign has been observed targeting organizations globally to steal Microsoft 365 credentials. The operation, monitored since early November 2025, employs advanced evasion techniques such as nested PDFs, use of legitimate content delivery networks, and mouse tracking to bypass secure email gateways and multi-factor authentication. The final credential harvesting site is engineered to block security tools and analysts, and leverages legitimate Microsoft infrastructure to circumvent MFA, granting attackers immediate access to compromised accounts. These attacks highlight the increasing complexity of phishing operations and their ability to evade traditional security controls. In parallel, threat actors are exploiting free cloud hosting platforms like Cloudflare Pages to host convincing phishing portals impersonating banking and healthcare providers. These sites not only harvest credentials but also collect additional security information, such as answers to secret questions, and exfiltrate data via Telegram bots to evade detection. Attackers use compromised legitimate domains as redirectors, increasing the likelihood of bypassing spam filters and making takedown efforts more challenging. The convergence of advanced phishing techniques and abuse of trusted cloud services underscores the need for enhanced detection and response strategies for organizations relying on Microsoft 365 and similar platforms.
Jun 29, 2026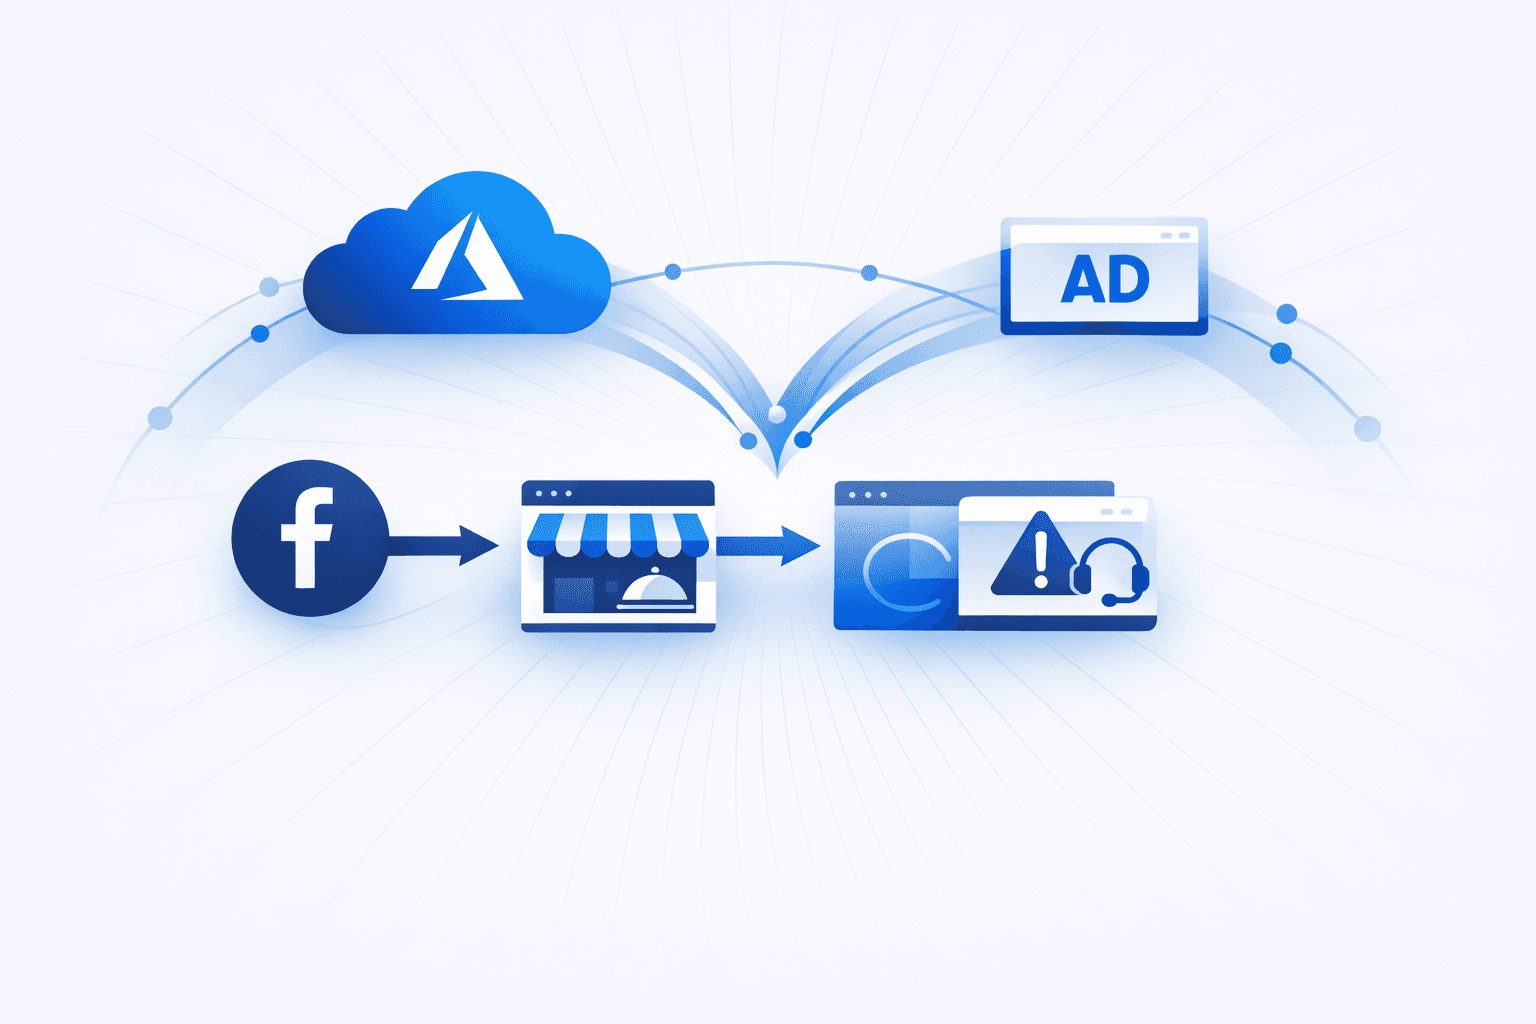
Threat actors are increasingly using **trusted platforms**—including cloud hosting and major ad networks—to deliver multi-stage phishing and scam campaigns that evade traditional URL and domain reputation controls. Recent activity includes a **three-step malvertising chain** delivered via **Facebook paid ads** that redirects victims through a decoy site (e.g., a fake Italian restaurant page) before landing on a **tech support scam (TSS) kit** hosted on **Microsoft Azure** infrastructure (including `web.core.windows.net`). Researchers reported rapid infrastructure churn, with **100+ domains rotated in seven days**, and targeting focused on **U.S. users** with activity concentrated on weekdays. Parallel enterprise-focused campaigns are hosting phishing infrastructure on **Microsoft Azure Blob Storage**, **Google Firebase**, and **AWS CloudFront**, using **redirect chains, CAPTCHA gates, and QR codes** to bypass automated analysis and email defenses. Analysis highlighted the use of **Adversary-in-the-Middle (AiTM)** phishing-as-a-service kits—**Tycoon2FA**, **Sneaky2FA**, and **EvilProxy**—to steal credentials and **session tokens** even when MFA is enabled. Separately, researchers documented a “clean email” approach to steal **Dropbox** credentials: benign-looking procurement-themed emails deliver **PDF attachments** that hide clickable elements (e.g., via *AcroForms* and `FlateDecode`), which then route victims to a second-stage file hosted on **Vercel Blob** and ultimately to a fake Dropbox login page that captures credentials and collects victim telemetry (IP address, location, and device details).
Jun 29, 2026
Multiple campaigns are abusing *legitimate* cloud and platform workflows to make phishing and fraud harder to detect. Attackers are generating real Apple and PayPal invoice/dispute emails and embedding scam phone numbers in user-controlled fields (e.g., “seller notes”), resulting in messages that carry valid **DKIM** signatures and originate from high-reputation domains; this “**DKIM replay**” style abuse bypasses many email controls because authentication validates the sender domain, not the safety of the embedded content. In parallel, threat actors are leveraging free **Google Firebase** developer accounts to host brand-mimicking phishing pages on trusted `firebaseapp.com` / `web.app` subdomains, increasing delivery and click-through rates by exploiting domain reputation and common allowlisting of Google infrastructure. A separate but related social-engineering technique targets **Telegram** users by manipulating Telegram’s official authentication workflows to obtain fully authorized sessions rather than simply stealing passwords. Victims are lured to Telegram-lookalike pages (often on ephemeral domains) that prompt QR scanning or phone-number entry; user interaction triggers a real login attempt initiated by the attacker, and once the victim approves the authorization prompt on their device, the attacker gains persistent account access and can pivot to follow-on attacks via the victim’s contacts. These incidents collectively highlight a shift toward “living off trusted services,” where adversaries avoid compromising vendors and instead weaponize legitimate features, trusted domains, and sanctioned authentication flows to reduce detection and increase victim compliance.
Jun 29, 2026