
Loading story…
Infoblox Threat Intel reported a previously unreported phishing technique that abuses the infrastructure-focused .arpa TLD—normally used for reverse DNS mapping—to host and deliver phishing content in ways that can bypass common enterprise controls. Threat actors obtain control of IPv6 address space via free IPv6 tunnel services, then exploit DNS management weaknesses at some providers to create records that should not exist for reverse-DNS zones (e.g., creating A records instead of expected PTR records). This results in long, reverse-DNS-style domains under ip6.arpa that resolve and can serve malicious content, while appearing “infrastructure-like” and therefore less likely to be blocked by reputation-based defenses.
The observed campaigns use malspam impersonating major consumer brands and typically present a single image containing an embedded hyperlink, obscuring the unusual .arpa destination from the user. Clicking the image sends victims through a Traffic Distribution System (TDS) that fingerprints traffic (including device targeting such as mobile) and then redirects to fraudulent pages. Reporting emphasized that because .arpa is critical to Internet operations and is rarely treated as a web-hosting namespace, defenders may have blind spots in URL filtering, domain reputation, and DNS policy enforcement when attackers weaponize ip6.arpa-style hostnames.
Get the infrastructure and lures behind it.
4 events from the most recent confirmed update back to the earliest known activity.
CloudSEK reported that large-scale scanning of 127,906 IPv6 prefixes uncovered 384 suspicious ip6.arpa zones delegated to Cloudflare nameservers and confirmed two zones as actively malicious. In addition to infrastructure overlapping with the earlier Infoblox-observed activity, the researchers identified a separate active campaign using the zone 0.d.7.2.7.0.1.b.e.0.a.2.ip6.arpa on IONOS infrastructure in Frankfurt, Germany.
Infoblox publicly disclosed the campaign and explained how attackers used .arpa, IPv6 address space, traffic distribution systems, and short-lived redirect chains to bypass common security controls. The report also linked the activity to related techniques such as dangling CNAME hijacking and subdomain shadowing, and shared indicators and defensive recommendations.
Infoblox Threat Intel identified a previously unreported phishing technique that abuses the .arpa namespace and IPv6 reverse-DNS names under ip6.arpa to host or route victims to phishing content. The campaign used free IPv6 tunnel services, unexpected DNS record creation, and infrastructure-looking hostnames to evade reputation and registration-based defenses.
Infoblox observed some hijacked CNAMEs being used consistently from September 2025 as part of the same broader evasion ecosystem tied to the phishing activity. In some cases, expired service domains enabled takeover of many dependent subdomains belonging to trusted organizations.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 22 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
6 references tracked. Mallory keeps watching after this page renders.
cloudsek.com
Open sourcecloudsek.com
Open sourcehackread.com
Open sourcescworld.com
Open sourcecybersecuritynews.com
Open sourceinfoblox.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
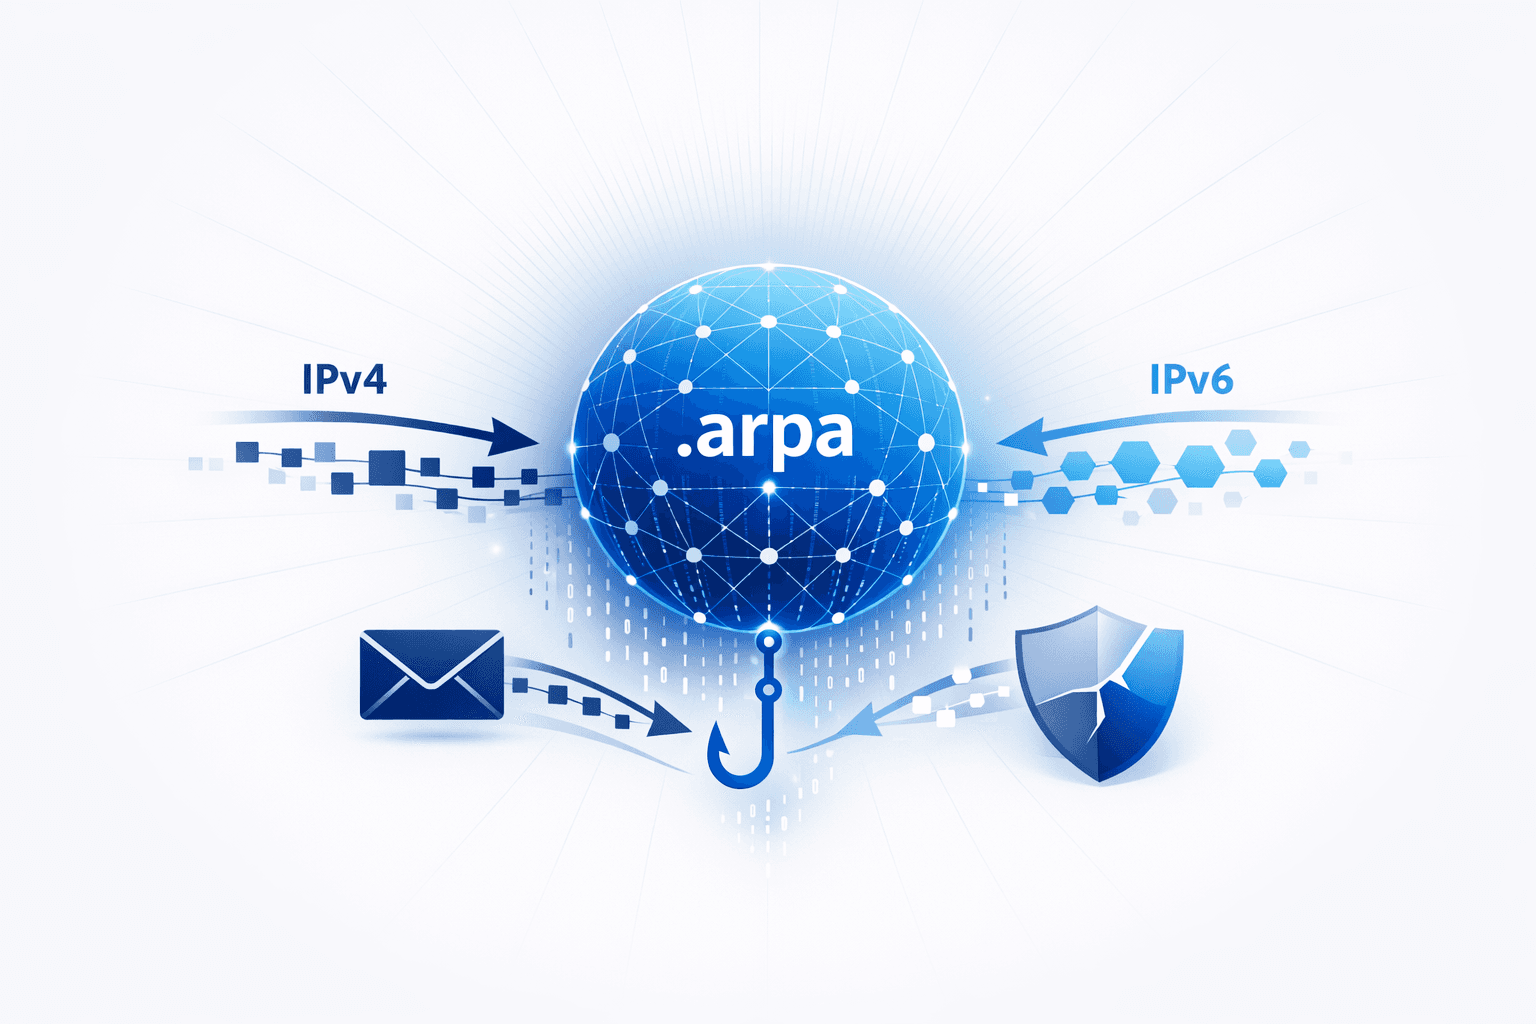
Threat actors are abusing the special-use **`.arpa`** DNS namespace—intended for internet infrastructure and reverse-DNS lookups—to make phishing infrastructure harder for email security gateways and reputation systems to evaluate. The activity leverages reverse-DNS conventions (IPv4 `in-addr.arpa` and IPv6 `ip6.arpa`) but uses **atypical forward-lookups** (e.g., `A`/`AAAA` records) and non-standard hostnames under `.arpa`, which can slip past controls that treat `.arpa` traffic as benign or “internal plumbing.” Reporting attributed the technique to observations shared by **Infoblox**, noting it combines legacy DNS assumptions with modern **IPv6** usage to reduce detection efficacy for “basic scam-type” phishing, with concern it may be applicable to more targeted operations. Defensive guidance highlighted that legitimate `in-addr.arpa` names follow a strict IP-derived format ending in the suffix, so **any `.arpa` query that is not a PTR-style reverse lookup or does not match expected naming patterns** should be blocked or at least alerted on, and organizations should review DNS/email filtering logic to ensure `.arpa` is not implicitly trusted.
Jun 29, 2026
Threat actors are increasingly hosting phishing infrastructure on legitimate cloud and decentralized platforms, including **Cloudflare Workers**, **Cloudflare Pages**, **Vercel**, **GitHub Pages**, **Netlify**, and **IPFS** gateways, to evade detection and benefit from trusted shared-domain reputation and free-tier scalability. Securelist reported that defenders blocked **224,984** unique third-level domains tied to phishing on these services between August 2025 and July 2026, and identified and neutralized more than **390,000** phishing pages. One documented campaign used a compromised website as an initial relay before directing victims to Cloudflare Workers subdomains for staging, where attackers deployed service workers and the **Ultraviolet** proxy library to transparently intercept traffic in an adversary-in-the-middle attack. The operation also used a browser-in-the-browser spoof to imitate Microsoft login prompts and steal **credentials**, **MFA codes**, and **session tokens**, underscoring how legitimate cloud infrastructure is being repurposed to support large-scale credential theft.
Aug 4, 2026
Multiple reports describe **phishing-led malware delivery** that abuses trusted services and “living off the land” execution paths to evade controls and deploy remote access tooling. Cloudflare-tracked activity shows attackers using **Vercel-hosted** pages to lend legitimacy to malicious links and bypass email/security filtering, with lures themed around invoices, payments, shipping, and document portals; the infrastructure includes **Telegram-based filtering** and browser fingerprinting/conditional delivery to hinder researchers and sandboxes before serving payloads that install a **remote access tool (RAT)**. A separate campaign (tracked as **PHALT#BLYX**) targets hospitality staff with Booking[.]com-style reservation emails and uses a **fake browser error + fake BSOD** to coerce victims into running the **ClickFix** technique (Win+R paste/execute), launching PowerShell that pulls malicious project files and executes them via **`MSBuild.exe`** to deliver **DCRat**, consistent with **LOLBins**-based evasion; researchers noted Russian-language artifacts in the malware. Broader weekly/newsletter roundups also highlight the same risk theme—attackers increasingly blend social engineering with trusted infrastructure and tools—while mixing in unrelated items (e.g., firewall CVEs, general malware research links) that are not part of a single, specific incident narrative.
Jun 29, 2026