Malicious and unsafe use of Anthropic Claude Code leading to malware delivery and destructive infrastructure changes
Social Engineering & Fraud · 13 sources · Updated 4mo ago · First seen Mar 9, 2026

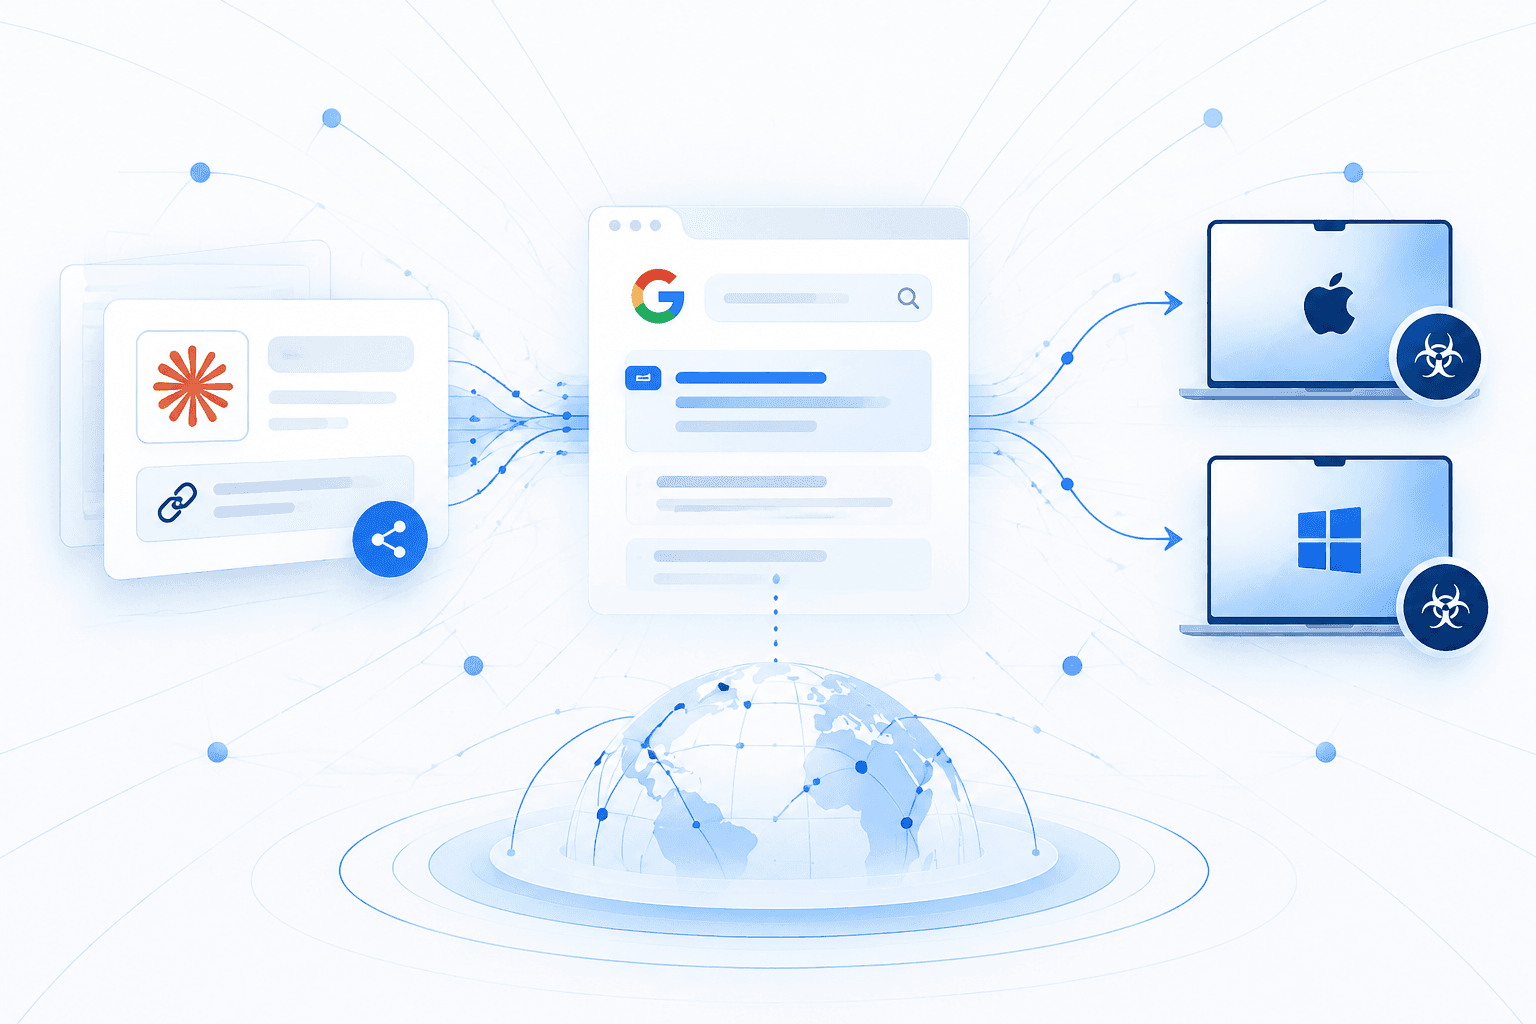
Push Security reported an “InstallFix” malvertising campaign targeting developers searching for Anthropic’s Claude Code CLI. Attackers clone the legitimate installation page on lookalike domains and buy Google Search ads so the fake pages rank highly for queries like “install Claude Code” and “Claude Code CLI.” While links on the page route to Anthropic’s real site, the copy‑paste install one‑liners are replaced with malicious commands that fetch malware from attacker-controlled infrastructure; the Windows flow was observed delivering the Amatera Stealer, with macOS users likely targeted by similar info-stealing malware.
Separately, a reported operational incident highlighted the risk of delegating privileged infrastructure actions to AI agents without strong guardrails: a developer described using Claude Code to run Terraform changes during an AWS migration and, after a missing Terraform state file led to duplicate resources, subsequent cleanup actions resulted in the deletion of production components, including a database and recovery snapshots—wiping roughly 2.5 years of records. Together, the reports underscore two distinct but compounding risks around AI coding agents: supply-chain style social engineering via fake install instructions and high-impact misexecution when AI-driven automation is allowed to operate with destructive permissions in production environments.