Zero Trust Access Models and Their Limits in Enterprise, IoT, and OT Environments
Attack Tradecraft · 2 sources · Updated 4mo ago · First seen Mar 13, 2026
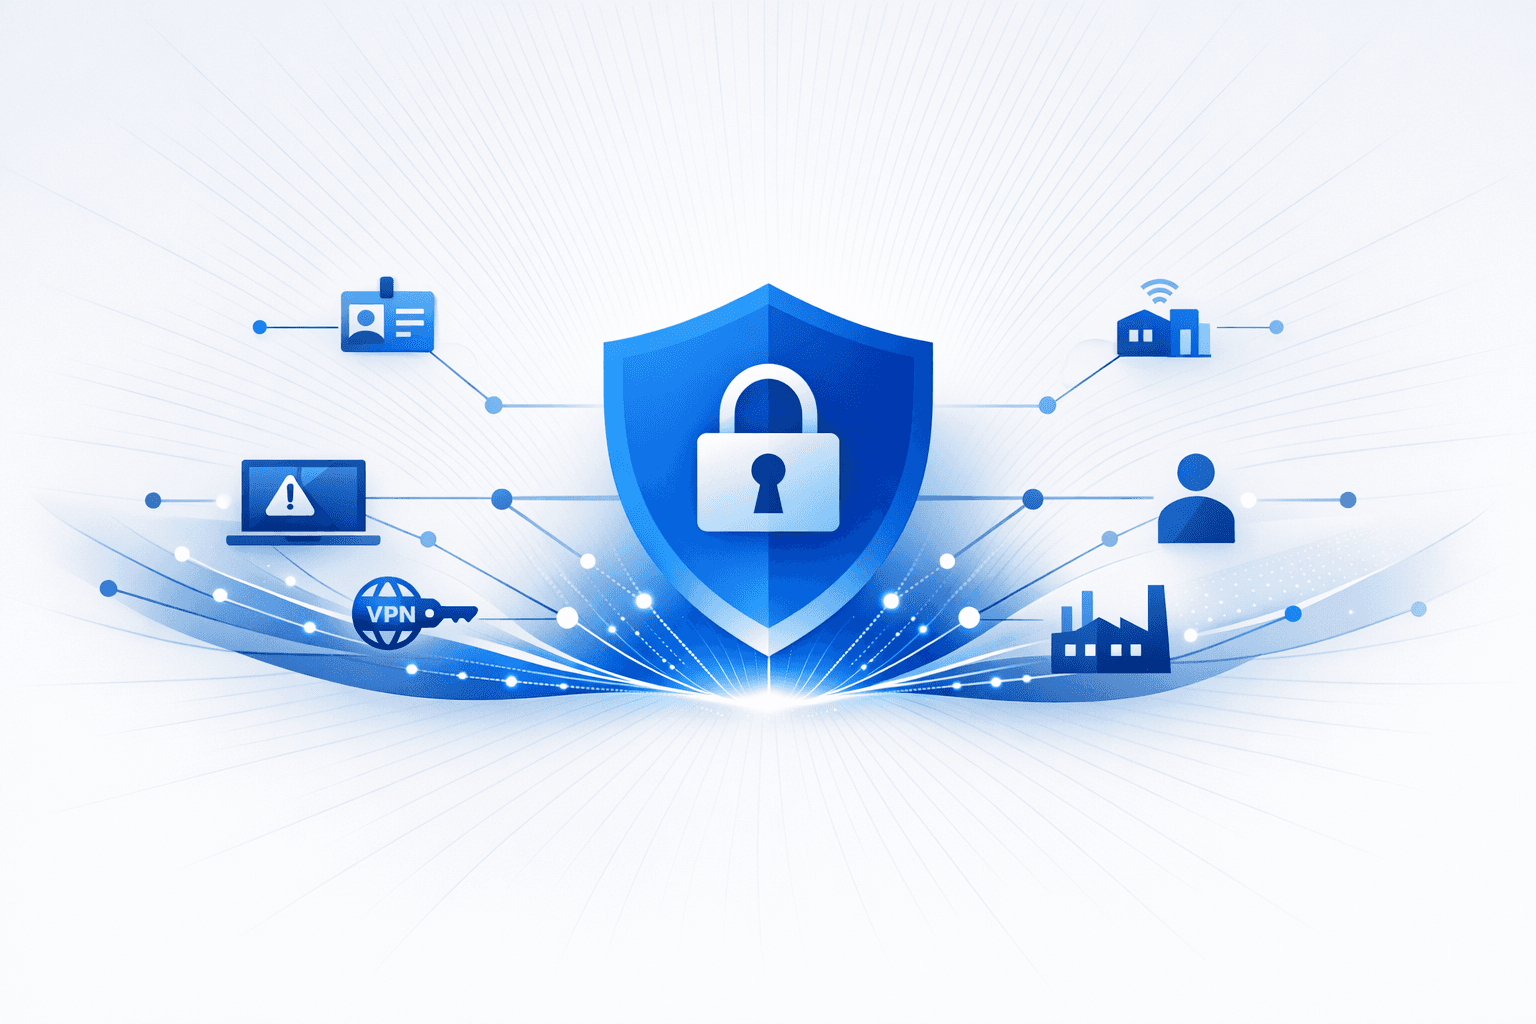
Zero trust was the common topic across the relevant coverage, focusing on how identity, device health, and contextual access controls can reduce the impact of compromised credentials, infected endpoints, and third-party access. One report used practical scenarios such as stolen VPN credentials, a compromised employee laptop, and contractor connectivity to show how ZTNA can limit lateral movement compared with traditional VPN-based access.
A second relevant article argued that zero trust is harder to implement effectively in IoT and OT environments, where legacy systems, operational constraints, and device limitations can undermine standard identity- and policy-based controls. The material is not fluff because it contains substantive security analysis, but one reference is not actually about the same topic and appears to be a different opinion piece mixed into the page metadata rather than coverage of zero trust itself.